IAM
229 items from kdeldycke/awesome-iam ★2,303
-
An Overview of Cryptography garykessler.net
“This paper has two major purposes. The first is to define some of the terms and concepts behind basic cryptographic methods, and to offer a way to compare the myriad cryptographic schemes in use today. The second is to provide some real examples of cryptography in use today.”
-
GDPR Enforcement Tracker enforcementtracker.com
List of GDPR fines and penalties.
-
OAuth 2.0 Security Best Current Practice datatracker.ietf.org
“Updates and extends the OAuth 2.0 Security Threat Model to incorporate practical experiences gathered since OAuth 2.0 was published and covers new threats relevant due to the broader application”.
-
HTML attributes to improve your users' two factor authentication experience twilio.com
“In this post we will look at the humble <input> element and the HTML attributes that will help speed up our users' two factor authentication experience”.
-
Magic Links – Are they Actually Outdated? zitadel.com
What are magic links, their origin, pros and cons.
-
Become an AWS IAM Policy Ninja youtube.com
“In my nearly 5 years at Amazon, I carve out a little time each day, each week to look through the forums, customer tickets to try to find out where people are having trouble.”
-
Still Logged In: What AR and VR Can Learn from MMOs youtube.com
“If you host an online community, where people can harm another person: you are on the hook. And if you can't afford to be on the hook, don't host an online community”.
-
Scaling backend authentication at Facebook youtube.com
How-to in a nutshell: 1. Small root of trust; 2. TLS isn't enough; 3. Certificate-based tokens; 4. Crypto Auth Tokens (CATs). See the slides for more details.
-
Secret at Scale at Netflix youtube.com
Solution based on blind signatures. See the slides.
-
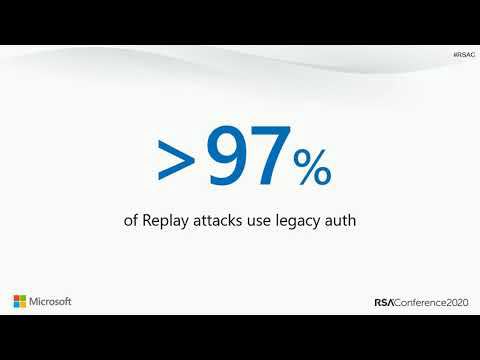
Breaking Password Dependencies: Challenges in the Final Mile at Microsoft youtube.com
The primary source of account hacks is password spraying (on legacy auth like SMTP, IMAP, POP, etc.), second is replay attack. Takeaway: password are insecure, use and enforce MFA.
-
OAuth 2.0 and OpenID Connect (in plain English) youtube.com
Starts with an historical context on how these standards came to be, clears up the inaccuracies in the vocabulary, then details the protocols and its pitfalls to make it less intimidating.
-
High Availability in Google's Internal KMS youtube.com
Not GCP's KMS, but the one at the core of their infrastructure. See the slides.
-
WebAuthn guide webauthn.guide
Introduce WebAuthn as a standard supported by all major browsers, and allowing “servers to register and authenticate users using public key cryptography instead of a password”.
-
Real World Crypto Symposium web.archive.org
Aims to bring together cryptography researchers with developers, focusing on uses in real-world environments such as the Internet, the cloud, and embedded devices.
-
HSM: What they are and why it's likely that you've (indirectly) used one today web.archive.org
Really basic overview of HSM usages.
-
Getting started with security keys web.archive.org
A practical guide to stay safe online and prevent phishing with FIDO2, WebAuthn and security keys.
-
163 AWS services explained in one line each web.archive.org
Help makes sense of their huge service catalog. In the same spirit: AWS In Plain English.
-
GCP's IAM syntax is better than AWS's web.archive.org
The minutiae of permission design in GCP improves the developer's experience.
-
What is BeyondCorp? What is Identity-Aware Proxy? web.archive.org
More companies add extra layers of VPNs, firewalls, restrictions and constraints, resulting in a terrible experience and a slight security gain. There's a better way.
-
Mitigating Cloud Vulnerabilities web.archive.org
“This document divides cloud vulnerabilities into four classes (misconfiguration, poor access control, shared tenancy vulnerabilities, and supply chain vulnerabilities)”.
-
Google's Macaroons in Five Minutes or Less web.archive.org
If I'm given a Macaroon that authorizes me to perform some action(s) under certain restrictions, I can non-interactively build a second Macaroon with stricter restrictions that I can then give to you.
-
In Search For a Perfect Access Control System web.archive.org
The historical origins of authorization schemes. Hints at the future of sharing, trust and delegation between different teams and organizations.
-
After Car2Go eased its background checks, 75 of its vehicles were stolen in one day. web.archive.org
Why background check are sometimes necessary.
-
SAML vs. OAuth web.archive.org
“OAuth is a protocol for authorization: it ensures Bob goes to the right parking lot. In contrast, SAML is a protocol for authentication, or allowing Bob to get past the guardhouse.”
-
JWT, JWS and JWE for Not So Dummies! web.archive.org
A signed JWT is known as a JWS (JSON Web Signature). In fact a JWT does not exist itself — either it has to be a JWS or a JWE (JSON Web Encryption). Its like an abstract class — the JWS and JWE are the concrete implementations.
-
The False Allure of Hashing for Anonymization web.archive.org
Hashing is not sufficient for anonymization no. But still it is good enough for pseudonymization (which is allowed by the GDPR).
-
Hardcoded secrets, unverified tokens, and other common JWT mistakes web.archive.org
A good recap of all JWT pitfalls.
-
How Radix trees made blocking IPs 5000 times faster web.archive.org
Radix trees might come handy to speed-up IP blocklists.
-
IAM is hard. It's really hard. web.archive.org
“Overly permissive AWS IAM policies that allowed s3:GetObject to * (all) resources”, led to $80 million fine for Capital One. The only reason why you can't overlook IAM as a business owner.
-
A Child's Garden of Inter-Service Authentication Schemes web.archive.org
In the same spirit as above, but this time at the service level.
-
Conversion Optimization web.archive.org
A collection of tactics to increase the chance of users finishing the account creation funnel.
-
Zanzibar: Google's Consistent, Global Authorization System web.archive.org
Scales to trillions of access control lists and millions of authorization requests per second to support services used by billions of people. It has maintained 95th-percentile latency of less than 10 milliseconds and availability of greater than 99.999% over 3 years of…
-
Macaroons: Cookies with Contextual Caveats for Decentralized Authorization in the Cloud web.archive.org
Google's original paper.
-
You (probably) don't need ReCAPTCHA web.archive.org
Starts with a rant on how the service is a privacy nightmare and is tedious UI-wise, then list alternatives.
-
An argument for passwordless web.archive.org
Passwords are not the be-all and end-all of user authentication. This article tries to tell you why.
-
Lifetimes of cryptographic hash functions valerieaurora.org
“If you are using compare-by-hash to generate addresses for data that can be supplied by malicious users, you should have a plan to migrate to a new hash every few years”.
-
A Comparison of Personal Name Matching: Techniques and Practical Issues users.cecs.anu.edu.au
Customer name matching has lots of application, from account deduplication to fraud monitoring.
-
The 2020 State of SaaS Product Onboarding userpilot.com
Covers all the important facets of user onboarding.
-
User Onboarding Teardowns useronboard.com
A huge list of deconstructed first-time user signups.
-
BeyondCorp: A New Approach to Enterprise Security usenix.org
Quick overview of Google's Zero-trust Network initiative.
-
Attacking Google Authenticator unix-ninja.com
Probably on the verge of paranoia, but might be a reason to rate limit 2FA validation attempts.
-
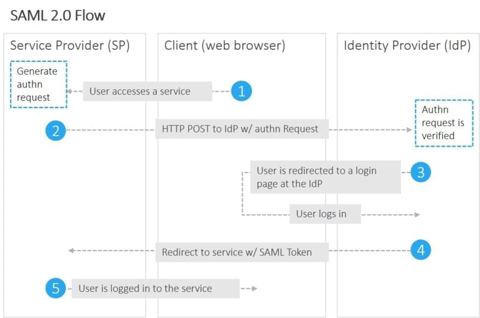
The Difference Between SAML 2.0 and OAuth 2.0 ubisecure.com
“Even though SAML was actually designed to be widely applicable, its contemporary usage is typically shifted towards enterprise SSO scenarios. On the other hand, OAuth was designed for use with applications on the Internet, especially for delegated authorisation.”
-
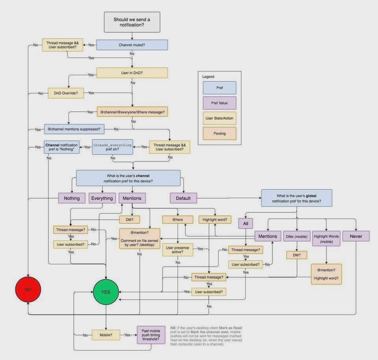
For anybody who thinks "I could build that in a weekend," this is how Slack decides to send a notification twitter.com
Notifications are hard. Really hard.
-
Why are the username and password on two different pages? twilio.com
To support both SSO and password-based login. Now if breaking the login funnel in 2 steps is too infuriating to users, solve this as Dropbox does: an AJAX request when you enter your username.
-
Beyond Passwords: 2FA, U2F and Google Advanced Protection troyhunt.com
An excellent walk-trough over all these technologies.
-
Banks, Arbitrary Password Restrictions and Why They Don't Matter troyhunt.com
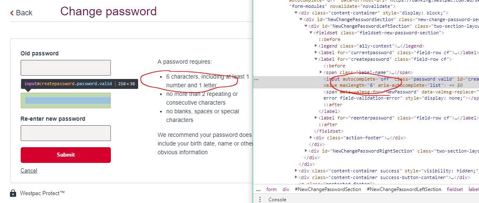
“Arbitrary low limits on length and character composition are bad. They look bad, they lead to negative speculation about security posture and they break tools like password managers.”
-
Standards related to Threat Intelligence threat-intelligence.eu
Open standards, tools and methodologies to support threat intelligence analysis.
-
The Cleaners thoughtmaybe.com
A documentary on these teams of underpaid people removing posts and deleting accounts.
-
AT&T rep handed control of his cellphone account to a hacker theregister.com
-
Facebook Dangerous Individuals and Organizations List theintercept.com
Some groups and content are illegal in some juridictions. This is an example of a blocklist.
- next page of items loading…