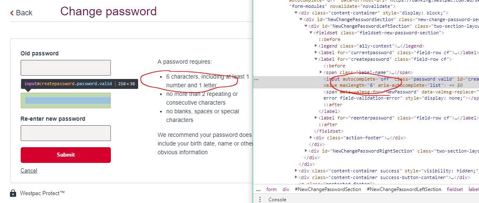
Banks, Arbitrary Password Restrictions and Why They Don't Matter
“Arbitrary low limits on length and character composition are bad. They look bad, they lead to negative speculation about security posture and they break tools like password managers.”
- from
- IAM
- added
- 2026-10-10
- likes
- 0
similar
-
Password expiration is dead techcrunch.com
Recent scientific research calls into question the value of many long-standing password-security practices such as password expiration policies, and points instead to better alternatives such as enforcing banned-password lists and MFA.
-
An argument for passwordless web.archive.org
Passwords are not the be-all and end-all of user authentication. This article tries to tell you why.
-
Practical Recommendations for Stronger, More Usable Passwords andrew.cmu.edu
This study recommend the association of: blocklist checks against commonly leaked passwords, password policies without character-class requirements, minimum-strength policies.
-
-
Password Storage Cheat Sheet cheatsheetseries.owasp.org
The only way to slow down offline attacks is by carefully choosing hash algorithms that are as resource intensive as possible.
-
Password Manager Resources github.com
🆓 A collection of password rules, change URLs and quirks by sites.
IAM › Password-based auth: ““Arbitrary low limits on length and character composition are bad. They look bad, they lead to negative speculation about security posture and they break tools like password managers.””