Breaking Password Dependencies: Challenges in the Final Mile at Microsoft
The primary source of account hacks is password spraying (on legacy auth like SMTP, IMAP, POP, etc.), second is replay attack. Takeaway: password are insecure, use and enforce MFA.
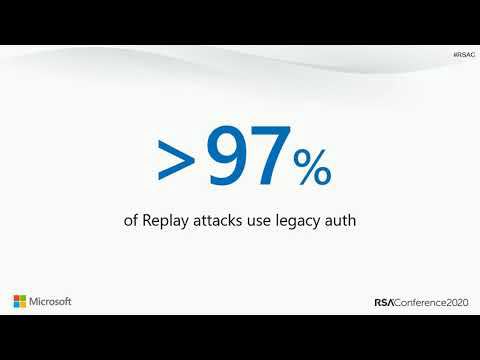
- from
- IAM
- added
- 2026-10-10
- likes
- 0
similar
-
Your Pa$$word doesn't matter techcommunity.microsoft.com
Same conclusion as above from Microsoft: “Based on our studies, your account is more than 99.9% less likely to be compromised if you use MFA.”
-
Compromising online accounts by cracking voicemail systems martinvigo.com
Or why you should not rely on automated phone calls as a method to reach the user and reset passwords, 2FA or for any kind of verification. Not unlike SMS-based 2FA, it is currently insecure and can be compromised by the way of its weakest link: voicemail systems.
-
Password expiration is dead techcrunch.com
Recent scientific research calls into question the value of many long-standing password-security practices such as password expiration policies, and points instead to better alternatives such as enforcing banned-password lists and MFA.
-
An argument for passwordless web.archive.org
Passwords are not the be-all and end-all of user authentication. This article tries to tell you why.
-
Hidden OAuth attack vectors portswigger.net
How to identify and exploit some of the key vulnerabilities found in OAuth 2.0 authentication mechanisms.
-
IAM › Multi-factor auth: “The primary source of account hacks is password spraying (on legacy auth like SMTP, IMAP, POP, etc.), second is replay attack. Takeaway: password are insecure, use and enforce MFA.”