An argument for passwordless
Passwords are not the be-all and end-all of user authentication. This article tries to tell you why.
- from
- IAM
- added
- 2026-10-10
- likes
- 0
similar
-
Clearing up some misconceptions about Passkeys stavros.io
Or why passkeys are not worse than passwords.
-
Don't get clever with login forms bradfrost.com
Create login forms that are simple, linkable, predictable, and play nicely with password managers.
-
Password expiration is dead techcrunch.com
Recent scientific research calls into question the value of many long-standing password-security practices such as password expiration policies, and points instead to better alternatives such as enforcing banned-password lists and MFA.
-
A Comparative Long-Term Study of Fallback Authentication maximiliangolla.com
Key take-away: “schemes based on email and SMS are more usable. Mechanisms based on designated trustees and personal knowledge questions, on the other hand, fall short, both in terms of convenience and efficiency.”
-
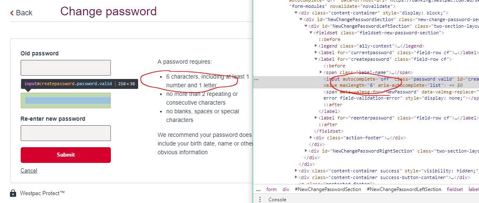
Banks, Arbitrary Password Restrictions and Why They Don't Matter troyhunt.com
“Arbitrary low limits on length and character composition are bad. They look bad, they lead to negative speculation about security posture and they break tools like password managers.”
-
Hypr hypr.com
State of Passwordless Identity Assurance (2026) - Analyzes the current state of passwordless identity assurance and the transition toward industrializing security practices amidst a shifting threat landscape. Key findings reveal that generative and agentic artificial…
IAM › Password-less auth: “Passwords are not the be-all and end-all of user authentication. This article tries to tell you why.”