Back-End Development
4,701 items in 32 lists
-
Getting started with security keys web.archive.org
A practical guide to stay safe online and prevent phishing with FIDO2, WebAuthn and security keys.
-
163 AWS services explained in one line each web.archive.org
Help makes sense of their huge service catalog. In the same spirit: AWS In Plain English.
-
GCP's IAM syntax is better than AWS's web.archive.org
The minutiae of permission design in GCP improves the developer's experience.
-
What is BeyondCorp? What is Identity-Aware Proxy? web.archive.org
More companies add extra layers of VPNs, firewalls, restrictions and constraints, resulting in a terrible experience and a slight security gain. There's a better way.
-
Mitigating Cloud Vulnerabilities web.archive.org
“This document divides cloud vulnerabilities into four classes (misconfiguration, poor access control, shared tenancy vulnerabilities, and supply chain vulnerabilities)”.
-
Google's Macaroons in Five Minutes or Less web.archive.org
If I'm given a Macaroon that authorizes me to perform some action(s) under certain restrictions, I can non-interactively build a second Macaroon with stricter restrictions that I can then give to you.
-
In Search For a Perfect Access Control System web.archive.org
The historical origins of authorization schemes. Hints at the future of sharing, trust and delegation between different teams and organizations.
-
After Car2Go eased its background checks, 75 of its vehicles were stolen in one day. web.archive.org
Why background check are sometimes necessary.
-
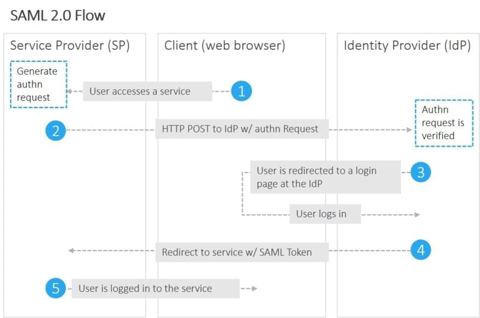
SAML vs. OAuth web.archive.org
“OAuth is a protocol for authorization: it ensures Bob goes to the right parking lot. In contrast, SAML is a protocol for authentication, or allowing Bob to get past the guardhouse.”
-
JWT, JWS and JWE for Not So Dummies! web.archive.org
A signed JWT is known as a JWS (JSON Web Signature). In fact a JWT does not exist itself — either it has to be a JWS or a JWE (JSON Web Encryption). Its like an abstract class — the JWS and JWE are the concrete implementations.
-
The False Allure of Hashing for Anonymization web.archive.org
Hashing is not sufficient for anonymization no. But still it is good enough for pseudonymization (which is allowed by the GDPR).
-
Hardcoded secrets, unverified tokens, and other common JWT mistakes web.archive.org
A good recap of all JWT pitfalls.
-
How Radix trees made blocking IPs 5000 times faster web.archive.org
Radix trees might come handy to speed-up IP blocklists.
-
IAM is hard. It's really hard. web.archive.org
“Overly permissive AWS IAM policies that allowed s3:GetObject to * (all) resources”, led to $80 million fine for Capital One. The only reason why you can't overlook IAM as a business owner.
-
A Child's Garden of Inter-Service Authentication Schemes web.archive.org
In the same spirit as above, but this time at the service level.
-
Conversion Optimization web.archive.org
A collection of tactics to increase the chance of users finishing the account creation funnel.
-
Zanzibar: Google's Consistent, Global Authorization System web.archive.org
Scales to trillions of access control lists and millions of authorization requests per second to support services used by billions of people. It has maintained 95th-percentile latency of less than 10 milliseconds and availability of greater than 99.999% over 3 years of…
-
Macaroons: Cookies with Contextual Caveats for Decentralized Authorization in the Cloud web.archive.org
Google's original paper.
-
You (probably) don't need ReCAPTCHA web.archive.org
Starts with a rant on how the service is a privacy nightmare and is tedious UI-wise, then list alternatives.
-
An argument for passwordless web.archive.org
Passwords are not the be-all and end-all of user authentication. This article tries to tell you why.
-
Lifetimes of cryptographic hash functions valerieaurora.org
“If you are using compare-by-hash to generate addresses for data that can be supplied by malicious users, you should have a plan to migrate to a new hash every few years”.
-
A Comparison of Personal Name Matching: Techniques and Practical Issues users.cecs.anu.edu.au
Customer name matching has lots of application, from account deduplication to fraud monitoring.
-
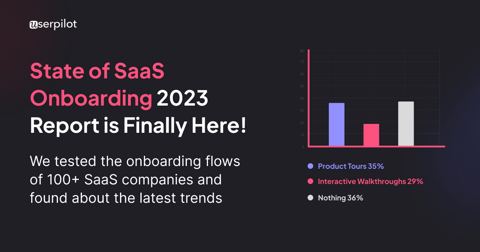
The 2020 State of SaaS Product Onboarding userpilot.com
Covers all the important facets of user onboarding.
-
User Onboarding Teardowns useronboard.com
A huge list of deconstructed first-time user signups.
-
BeyondCorp: A New Approach to Enterprise Security usenix.org
Quick overview of Google's Zero-trust Network initiative.
-
Attacking Google Authenticator unix-ninja.com
Probably on the verge of paranoia, but might be a reason to rate limit 2FA validation attempts.
-
The Difference Between SAML 2.0 and OAuth 2.0 ubisecure.com
“Even though SAML was actually designed to be widely applicable, its contemporary usage is typically shifted towards enterprise SSO scenarios. On the other hand, OAuth was designed for use with applications on the Internet, especially for delegated authorisation.”
-
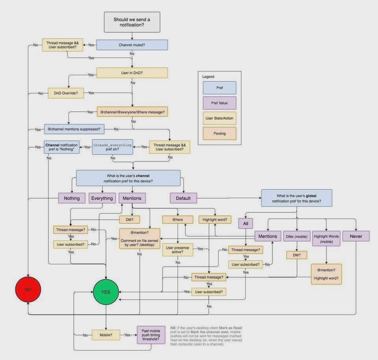
For anybody who thinks "I could build that in a weekend," this is how Slack decides to send a notification twitter.com
Notifications are hard. Really hard.
-
Why are the username and password on two different pages? twilio.com
To support both SSO and password-based login. Now if breaking the login funnel in 2 steps is too infuriating to users, solve this as Dropbox does: an AJAX request when you enter your username.
-
Beyond Passwords: 2FA, U2F and Google Advanced Protection troyhunt.com
An excellent walk-trough over all these technologies.
-
Banks, Arbitrary Password Restrictions and Why They Don't Matter troyhunt.com
“Arbitrary low limits on length and character composition are bad. They look bad, they lead to negative speculation about security posture and they break tools like password managers.”
-
Standards related to Threat Intelligence threat-intelligence.eu
Open standards, tools and methodologies to support threat intelligence analysis.
-
The Cleaners thoughtmaybe.com
A documentary on these teams of underpaid people removing posts and deleting accounts.
-
AT&T rep handed control of his cellphone account to a hacker theregister.com
-
Facebook Dangerous Individuals and Organizations List theintercept.com
Some groups and content are illegal in some juridictions. This is an example of a blocklist.
-
Password expiration is dead techcrunch.com
Recent scientific research calls into question the value of many long-standing password-security practices such as password expiration policies, and points instead to better alternatives such as enforcing banned-password lists and MFA.
-
SMS 2FA auth is deprecated by NIST techcrunch.com
NIST has said that 2FA via SMS is bad and awful since 2016.
-
Your Pa$$word doesn't matter techcommunity.microsoft.com
Same conclusion as above from Microsoft: “Based on our studies, your account is more than 99.9% less likely to be compromised if you use MFA.”
-
GDPR – A Practical guide for Developers techblog.bozho.net
A one-page summary of the above.
-
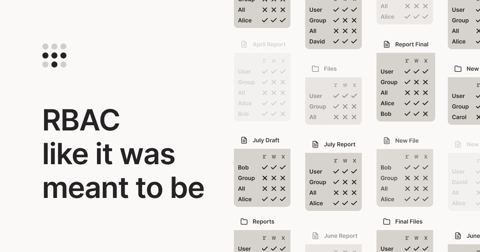
RBAC like it was meant to be tailscale.com
How we got from DAC (unix permissions, secret URL), to MAC (DRM, MFA, 2FA, SELinux), to RBAC. Details how the latter allows for better modeling of policies, ACLs, users and groups.
-
2FA is missing a key feature syslog.ravelin.com
“When my 2FA code is entered incorrectly I'd like to know about it”.
-
Clearing up some misconceptions about Passkeys stavros.io
Or why passkeys are not worse than passwords.
-
Secrets, Lies, and Account Recovery: Lessons from the Use of Personal Knowledge Questions at Google static.googleusercontent.com
“Our analysis confirms that secret questions generally offer a security level that is far lower than user-chosen passwords. (…) Surprisingly, we found that a significant cause of this insecurity is that users often don't answer truthfully. (…) On the usability side, we show…
-
Everybody be cool, this is a robbery! sstic.org
A case study of vulnerability and exploitability of a HSM (in French, sorry).
-
The SSO Wall of Shame sso.tax
A documented rant on the excessive pricing practiced by SaaS providers to activate SSO on their product. The author's point is, as a core security feature, SSO should be reasonably priced and not part of an exclusive tier.
-
The challenges of file formats speakerdeck.com
At one point you will let users upload files in your system. Here is a corpus of suspicious media files that can be leveraged by scammers =to bypass security or fool users.
-
Everything you should know about certificates and PKI but are too afraid to ask smallstep.com
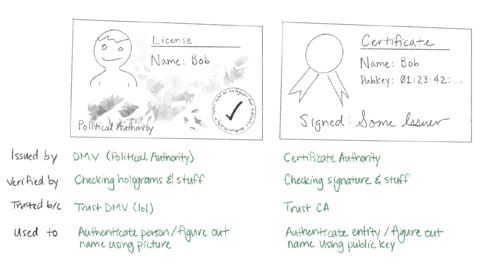
PKI lets you define a system cryptographically. It's universal and vendor neutral.
-
How to Implement a Secure Central Authentication Service in Six Steps shopify.engineering
Got multiple legacy systems to merge with their own login methods and accounts? Here is how to merge all that mess by the way of OIDC.
-
The Difficulties of SAML Single Logout shibboleth.atlassian.net
On the technical and UX issues of single logout implementations.
-
How effective is basic account hygiene at preventing hijacking security.googleblog.com
Google security team's data shows 2FA blocks 100% of automated bot hacks.
- next page of items loading…