How to Implement a Secure Central Authentication Service in Six Steps
Got multiple legacy systems to merge with their own login methods and accounts? Here is how to merge all that mess by the way of OIDC.
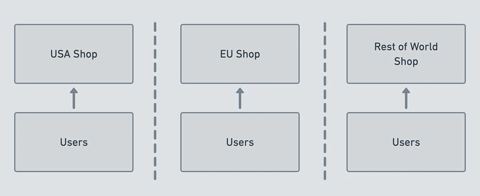
- from
- IAM
- added
- 2026-10-10
- likes
- 0
similar
-
-
GitHub Actions OIDC – Non-Human Identities and Secretless Authentication eparon.me
A two-part guide on moving from static secrets to OIDC-based identities in GitHub Actions, including a practical lab for protecting APIs.
-
Open-Sourcing BuzzFeed's SSO Experience increment.com
OAuth2-friendly adaptation of the Central Authentication Service (CAS) protocol. You'll find there good OAuth user flow diagrams.
-
Separate the account, user and login/auth details news.ycombinator.com
Sound advice to lay down the foundation of a future-proof IAM API.
-
A Child's Garden of Inter-Service Authentication Schemes web.archive.org
In the same spirit as above, but this time at the service level.
-
IAM › OAuth2 & OpenID: “Got multiple legacy systems to merge with their own login methods and accounts? Here is how to merge all that mess by the way of OIDC.”