CI/CD Attacks
88 items from tupletype/awesome-cicd-attacks ★635
-
Why npm lockfiles can be a security blindspot for injecting malicious modules snyk.io
Malicious code can be injected into npm projects via lockfiles (package-lock.json or yarn.lock) because these large, machine-generated files are rarely reviewed thoroughly.
-
Deep dive into Visual Studio Code extension security vulnerabilities snyk.io
VS Code extensions have vulnerabilities (command injection, path traversal, zip slip) that can compromise developer machines.
-
whoAMI: A cloud image name confusion attack securitylabs.datadoghq.com
Dependency Confusion using AWS AMIs.
-
Keeping your GitHub Actions and workflows secure Part 2: Untrusted input securitylab.github.com
GitHub Actions command injection.
-
Keeping your GitHub Actions and workflows secure Part 1: Preventing pwn requests securitylab.github.com
Combining pull_request_target workflow trigger with an explicit checkout of an untrusted PR may lead to repository compromise.
-
CloudQuarry: Digging for secrets in public AMIs securitycafe.ro
Researchers found 500GB of credentials, private repos, and keys in public AWS AMIs, impacting various industries.
-
Risk Explorer for Software Supply Chains riskexplorer.endorlabs.com
-
Publicly Exposed AWS Document DB Snapshots ramimac.me
Publicly exposed AWS DocumentDB snapshot of Cinemark Brazil revealed millions of customer records.
-
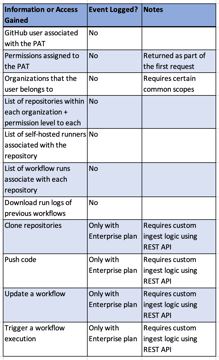
From Self-Hosted GitHub Runner to Self-Hosted Backdoor praetorian.com
Attackers exploit misconfigured runners and weak PAT security to gain persistence, escalate privileges, and move laterally.
-
-
Unpinnable Actions: How Malicious Code Can Sneak into Your GitHub Actions Workflows paloaltonetworks.com
GitHub Actions, even when pinned to a commit SHA, can still pull in malicious code via mutable dependencies like Docker images, unlocked packages, or external scripts.
-
All the Small Things: Azure CLI Leakage and Problematic Usage Patterns paloaltonetworks.com
Azure CLI leaks secrets to CI/CD logs due to usage patterns.
-
Abusing Repository Webhooks to Access Internal CI/CD Systems at Scale paloaltonetworks.com
Repository webhooks, used to trigger CI/CD pipelines, can be abused to access internal systems.
-
The GitHub Actions Worm: Compromising GitHub Repositories Through the Actions Dependency Tree paloaltonetworks.com
A novel GitHub Actions worm exploits the action dependency tree. Attackers compromise an action, then infect dependent actions via branch pushes or tag overwrites, spreading malware recursively.
-
How I hacked into Google's internal corporate assets observationsinsecurity.com
More ways to find dependencies in code for Dependency Confusion.
-
Hidden GitHub Commits and How to Reveal Them neodyme.io
A tool that can reveal deleted GitHub commits that potentially contain sensitive information and are not accessible via the public Git history.
-
10 real-world stories of how we've compromised CI/CD pipelines nccgroup.com
Examples include exploiting S3 misconfigurations, Jenkins plugin flaws, GitLab runner privilege escalations, Kubernetes pod annotation vulnerabilities, and compromised developer laptops.
-
AWS Targeted by a Package Backfill Attack mend.io
Scan commit history for internal packages to execute dependency confusion.
-
PPE — Poisoned Pipeline Execution medium.com
Poisoned Pipeline Execution (PPE) lets attackers run malicious code in a CI/CD system without direct access.
-
Malicious code analysis: Abusing SAST (mis)configurations to hack CI systems medium.com
Misconfigured SAST tools can be exploited to execute malicious code on CI systems, allowing attackers to steal credentials or deploy malicious artifacts.
-
Bypassing required reviews using GitHub Actions medium.com
GitHub Actions can bypass required reviews, allowing malicious code pushes to protected branches.
-
Dependency Confusion: How I Hacked Into Apple, Microsoft and Dozens of Other Companies medium.com
Researchers uploaded malicious packages with internal company names, gaining access to Apple, Microsoft, and others due to dependency confusion.
-
Zuckerpunch - Abusing Self Hosted GitHub Runners at Facebook marcyoung.us
Hide commits in a GitHub PR.
-
How to completely own an airline in 3 easy steps maia.crimew.gay
Misconfigured CI system accessible from the internet.
-
Vulnerable GitHub Actions Workflows Part 1: Privilege Escalation Inside Your CI/CD Pipeline legitsecurity.com
GitHub Actions workflow_run PE.
-
How We Hacked a Software Supply Chain for $50K landh.tech
Scraped JavaScript front-end files of the target and used ASTs to identify import/require statements which lead to discovering a public container with NPM credentials.
-
How a Single Vulnerability Can Bring Down the JavaScript Ecosystem landh.tech
Cache poisoning attack on the NPM registry rendering packages unavailable.
-
Leaking Secrets From GitHub Actions: Reading Files And Environment Variables, Intercepting Network/Process… karimrahal.com
Leaking secrets from vulnerable GitHub Actions workflows is possible via several methods: reading files/environment variables, intercepting communication, and dumping runner memory.
-
Fixing typos and breaching microsoft's perimeter johnstawinski.com
Bypass GitHub workflow approval requirement by becoming a contributor.
-
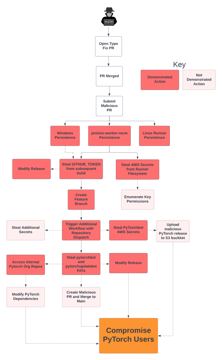
Playing with Fire – How We Executed a Critical Supply Chain Attack on PyTorch johnstawinski.com
Researchers exploited a critical PyTorch vulnerability via a malicious pull request to execute code on self-hosted runners.
-
Forging signed commits on GitHub iter.ca
A bug in GitHub's API allowed forging signed commits. By exploiting a regex flaw in an internal Codespaces API endpoint, an attacker could create commits signed by any user, despite GitHub's web flow signature.
-
Grep.app grep.app
Search GitHub using regex.
-
Security alert: social engineering campaign targets technology industry employees github.blog
Phishing GitHub users to download and execute repositories.
-
GHTorrent Project ghtorrent-downloads.ewi.tudelft.nl
A queryable offline mirror of the GitHub API data. Tutorial.
-
Dependency Confusions in Docker and remote pwning of your infra errno.fr
Docker dependency confusion occurs when a misconfigured Docker mirror pulls malicious public images instead of private ones.
-
Beyond S3: Exposed Resources on AWS duo.com
Public EBS, RDS, AMI and Elasticsearch clusters exposed to the internet.
-
Hacking GitHub AWS integrations again dagrz.com
Attacking misconfigured pipelines that use OIDC.
-
How We Discovered Vulnerabilities in CI/CD Pipelines of Popular Open-Source Projects cycode.com
Extracting all repository and organization secrets in GitHub Actions.
-
Holes in Your Bitbucket: Why Your CI/CD Pipeline Is Leaking Secrets cloud.google.com
Bitbucket Secured Variables leak secrets via artifact objects; recommendations include using dedicated secrets managers and code scanning.
-
StarJacking – Making Your New Open Source Package Popular in a Snap checkmarx.com
StarJacking is a technique where attackers make malicious open-source packages appear popular.
-
Working as unexpected chainguard.dev
Creating a GitHub branch that matches a branch protection rule pattern with a workflow file that triggers on push to gain access to environment secrets.
-
What the fork? Imposter commits in GitHub Actions and CI/CD chainguard.dev
GitHub Actions vulnerability allows forked commits to bypass workflow security settings.
-
Understanding typosquatting methods - for a secure supply chain bytesafe.dev
Typosquatting involves publishing malicious packages with names similar to legitimate ones, exploiting typos to inject malicious code.
-
Erosion of Trust: Unmasking Supply Chain Vulnerabilities in the Terraform Registry boostsecurity.io
Terraform modules are not protected by the Dependency Lock File, consequently, a seemingly harmless module could potentially introduce malicious code.
-
The massive bug at the heart of the npm ecosystem blog.vlt.sh
NPM Manifest Confusion.
-
Token-Spray blog.projectdiscovery.io
Automate token validation using Nuclei.
-
Hacking Terraform State for Privilege Escalation blog.plerion.com
Modifying a Terraform state file allows attackers to delete infrastructure or execute code via custom providers.
-
Introducing MavenGate: a supply chain attack method for Java and Android applications blog.oversecured.com
Many public and popular libraries that have long been abandoned are still being used in huge projects. Access to projects can be hijacked through domain name purchases.
-
Thousands of images on Docker Hub leak auth secrets, private keys bleepingcomputer.com
Researchers found thousands of Docker Hub images leaking private keys and API secrets.
-
Gitloker attacks abuse GitHub notifications to push malicious OAuth apps bleepingcomputer.com
Attackers use fake GitHub notifications to trick users into authorizing malicious OAuth apps that steal repo access.
- next page of items loading…