Security alert: social engineering campaign targets technology industry employees
Phishing GitHub users to download and execute repositories.
- from
- CI/CD Attacks
- added
- 2026-10-10
- likes
- 0
similar
-
Gitloker attacks abuse GitHub notifications to push malicious OAuth apps bleepingcomputer.com
Attackers use fake GitHub notifications to trick users into authorizing malicious OAuth apps that steal repo access.
-
GitHub comments abused to push malware via Microsoft repo URLs bleepingcomputer.com
Hidden GitHub comment link.
-
Keeping your GitHub Actions and workflows secure Part 1: Preventing pwn requests securitylab.github.com
Combining pull_request_target workflow trigger with an explicit checkout of an untrusted PR may lead to repository compromise.
-
Keeping your GitHub Actions and workflows secure Part 2: Untrusted input securitylab.github.com
GitHub Actions command injection.
-
-
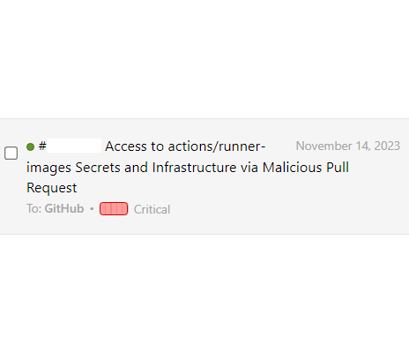
One Supply Chain Attack to Rule Them All – Poisoning GitHub's Runner Images adnanthekhan.com
A critical vulnerability in GitHub Actions, involving a misconfigured self-hosted runner in the actions/runner-images repository, allowed potential compromise of all GitHub and Azure hosted runner images.
CI/CD Attacks › Techniques > Initial Code Execution: “Phishing GitHub users to download and execute repositories.”