Erosion of Trust: Unmasking Supply Chain Vulnerabilities in the Terraform Registry
Terraform modules are not protected by the Dependency Lock File, consequently, a seemingly harmless module could potentially introduce malicious code.
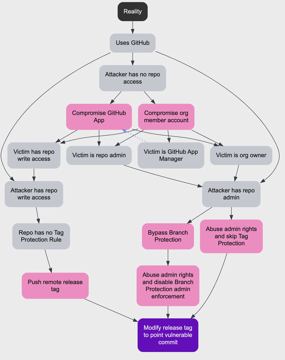
- from
- CI/CD Attacks
- added
- 2026-10-10
- likes
- 0
similar
-
Hacking Terraform State for Privilege Escalation blog.plerion.com
Modifying a Terraform state file allows attackers to delete infrastructure or execute code via custom providers.
-
Terraform Community Modules github.com
-
How a Single Vulnerability Can Bring Down the JavaScript Ecosystem landh.tech
Cache poisoning attack on the NPM registry rendering packages unavailable.
-
-
Fortune 500 at Risk: 250M Artifacts Exposed via Misconfigured Registries aquasec.com
Misconfigured public registries with software artifacts containing sensitive proprietary code and secrets.
-
CI/CD Attacks › Techniques > Initial Code Execution: “Terraform modules are not protected by the Dependency Lock File, consequently, a seemingly harmless module could potentially introduce malicious code.”