From Self-Hosted GitHub Runner to Self-Hosted Backdoor
Attackers exploit misconfigured runners and weak PAT security to gain persistence, escalate privileges, and move laterally.
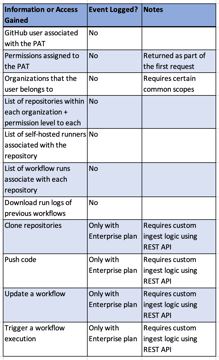
- from
- CI/CD Attacks
- added
- 2026-10-10
- likes
- 0
similar
-
Hijacking GitHub runners to compromise the organization synacktiv.com
Registering a GitHub runner with the ubuntu-latest tag grants access to jobs originally designated for GitHub-provisioned runners.
-
One Supply Chain Attack to Rule Them All – Poisoning GitHub's Runner Images adnanthekhan.com
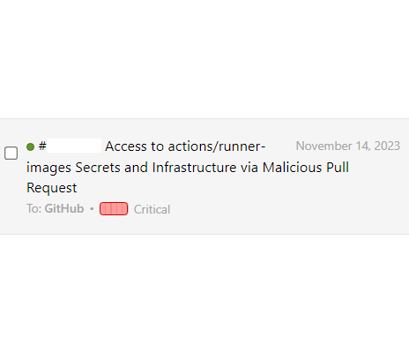
A critical vulnerability in GitHub Actions, involving a misconfigured self-hosted runner in the actions/runner-images repository, allowed potential compromise of all GitHub and Azure hosted runner images.
-
Vulnerable GitHub Actions Workflows Part 1: Privilege Escalation Inside Your CI/CD Pipeline legitsecurity.com
GitHub Actions workflow_run PE.
-
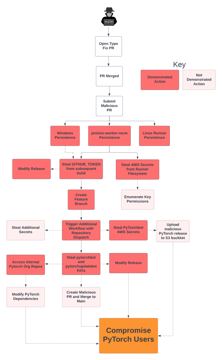
Playing with Fire – How We Executed a Critical Supply Chain Attack on PyTorch johnstawinski.com
Researchers exploited a critical PyTorch vulnerability via a malicious pull request to execute code on self-hosted runners.
-
GitHub Enterprise Remote Code Execution bounty.github.com
-
CI/CD Attacks › Techniques > Post Exploitation: “Attackers exploit misconfigured runners and weak PAT security to gain persistence, escalate privileges, and move laterally.”