One Supply Chain Attack to Rule Them All – Poisoning GitHub's Runner Images
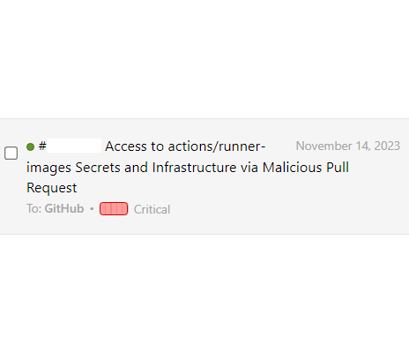
A critical vulnerability in GitHub Actions, involving a misconfigured self-hosted runner in the actions/runner-images repository, allowed potential compromise of all GitHub and Azure hosted runner images.
- from
- CI/CD Attacks
- added
- 2026-10-10
- likes
- 0
similar
-
Hijacking GitHub runners to compromise the organization synacktiv.com
Registering a GitHub runner with the ubuntu-latest tag grants access to jobs originally designated for GitHub-provisioned runners.
-
Keeping your GitHub Actions and workflows secure Part 2: Untrusted input securitylab.github.com
GitHub Actions command injection.
-
The (In)security Landscape of AI-Powered GitHub Actions (Part 2/2) wiz.io
Vulnerabilities in AI-powered GitHub Actions. Syntactical permission checks that let attackers impersonate trusted apps and Dependabot Deputy Confusion Injection.
-
The Monsters in Your Build Cache – GitHub Actions Cache Poisoning adnanthekhan.com
Allows attackers to compromise workflows even with limited permissions by exploiting vulnerabilities or dependency flaws, attackers steal cache tokens, fill the cache to force evictions, and replace legitimate entries with malicious code.
-
From Self-Hosted GitHub Runner to Self-Hosted Backdoor praetorian.com
Attackers exploit misconfigured runners and weak PAT security to gain persistence, escalate privileges, and move laterally.
-
Unpinnable Actions: How Malicious Code Can Sneak into Your GitHub Actions Workflows paloaltonetworks.com
GitHub Actions, even when pinned to a commit SHA, can still pull in malicious code via mutable dependencies like Docker images, unlocked packages, or external scripts.
CI/CD Attacks › Techniques > Defense Evasion: “A critical vulnerability in GitHub Actions, involving a misconfigured self-hosted runner in the actions/runner-images repository, allowed potential compromise of all GitHub and Azure hosted runner images.”