Security
5,347 items in 29 lists
-
Descope descope.com
State of Customer Identity Report (2025) - Analyzes the pervasive authentication stagnation noting 87% of organizations use passwords despite only 2% viewing them as effective. Highlights that open-source solutions nearly double revenue loss compared to commercial platforms…
-
Zuckerpunch - Abusing Self Hosted GitHub Runners at Facebook marcyoung.us
Hide commits in a GitHub PR.
-
How to completely own an airline in 3 easy steps maia.crimew.gay
Misconfigured CI system accessible from the internet.
-
Deloitte deloitte.com
Global Cyber Threat Intelligence Report (2025) - Analyzes global cyber threat trends throughout 2024, focusing on the evolution of ransomware, nation-state espionage, and shifting initial access techniques. Key findings include the continued dominance of ransomware driven by…
-
Vulnerable GitHub Actions Workflows Part 1: Privilege Escalation Inside Your CI/CD Pipeline legitsecurity.com
GitHub Actions workflow_run PE.
-
Deloitte deloitte.com
NASCIO Cybersecurity Study (2026) - Analyzes the evolving cybersecurity landscape for state governments, focusing on the impact of sophisticated threats, artificial intelligence, and shifting resource allocations. Key findings reveal that the percentage of state chief…
-
How We Hacked a Software Supply Chain for $50K landh.tech
Scraped JavaScript front-end files of the target and used ASTs to identify import/require statements which lead to discovering a public container with NPM credentials.
-
How a Single Vulnerability Can Bring Down the JavaScript Ecosystem landh.tech
Cache poisoning attack on the NPM registry rendering packages unavailable.
-
Deloitte deloitte.com
Future of Cyber Survey (2025) - Surveys the state of global cybersecurity leadership, analyzing strategic paradoxes and organizational maturity across various industries. Key findings reveal that 17 percent of surveyed enterprises qualify as frontrunners with advanced…
-
Leaking Secrets From GitHub Actions: Reading Files And Environment Variables, Intercepting Network/Process… karimrahal.com
Leaking secrets from vulnerable GitHub Actions workflows is possible via several methods: reading files/environment variables, intercepting communication, and dumping runner memory.
-
Cyber Edge delinea.com
Cyberthreat Defense Report (2025) - Analyzes the current state of cybersecurity defenses and the perceptions of IT security professionals. Key insights reveal a plateauing trend in successful cyberattacks, a significant preference for AI in security products, and persistent…
-
Fixing typos and breaching microsoft's perimeter johnstawinski.com
Bypass GitHub workflow approval requirement by becoming a contributor.
-
Delinea delinea.com
State Of Ransomware Report (2025) - Analyzes the evolving ransomware threat landscape and organizational responses, highlighting key trends and challenges. Key findings indicate a surge in ransomware breaches and data extortion, alongside increasing executive concern despite…
-
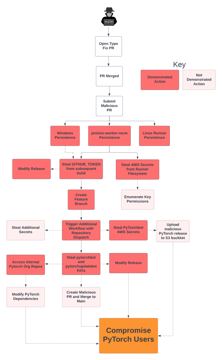
Playing with Fire – How We Executed a Critical Supply Chain Attack on PyTorch johnstawinski.com
Researchers exploited a critical PyTorch vulnerability via a malicious pull request to execute code on self-hosted runners.
-
Forging signed commits on GitHub iter.ca
A bug in GitHub's API allowed forging signed commits. By exploiting a regex flaw in an internal Codespaces API endpoint, an attacker could create commits signed by any user, despite GitHub's web flow signature.
-
Delinea delinea.com
AI In Identity Security Report (2025) - Analyzes the widespread adoption of AI in IT operations and the associated risks, emphasizing the necessity for updated identity governance frameworks to manage agentic and generative AI entities. Key findings indicate that while 94% of…
-
Grep.app grep.app
Search GitHub using regex.
-
United States Air Force defenseinnovationmarketplace.dtic.mil
Science and Technology Vision (2025) - Examines the cyberspace science and technology vision of the United States Air Force across multiple operational domains through the year 2025. Key insights detail strategic planning across 10 core sections to address escalating threats…
-
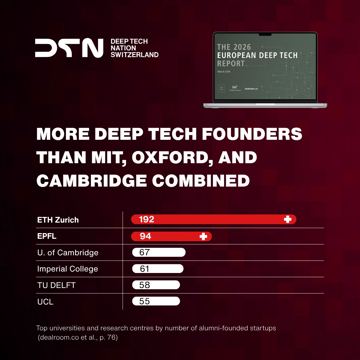
TableMedia deeptechnation.ch
European Deep Tech Report (2026) - Examines the state of European Deep Tech, focusing on its funding landscape, talent pool, and market opportunities. Key findings reveal that European Deep Tech VC funding reached $20.3 billion, comprising an.
-
Deepstrike deepstrike.io
Vulnerabilities Statistics (2025) - Analyzes the global surge in cybersecurity vulnerabilities throughout 2025, documenting a record pace of disclosures and the increasing speed of weaponization by threat actors. Key findings reveal that over 21,500 vulnerabilities were…
-
Deepstrike deepstrike.io
Cybersecurity Statistics (2026) - Analyzes the global cybersecurity landscape by evaluating incident volumes, financial impacts, and evolving threat vectors across diverse industries. Key findings reveal a 32 percent year over year increase in global ransomware attacks reaching…
-
DeepInstinct deepinstinct.com
Voice of SecOps (2025) - Examines the integration of artificial intelligence within security operations and its impact on organizational defense strategies based on a survey of 500 senior cybersecurity experts. Findings reveal that while 86 percent of organizations have…
-
Data Dog datadoghq.com
State Of DevSecOps (2026) - Analyzes the current state of DevSecOps by investigating the prevalence of exploitable vulnerabilities and the risks associated with rapid software dependency updates. Findings indicate that 87 percent of organizations maintain at least one…
-
Data Dog datadoghq.com
State Of Cloud Security (2025) - Analyzes cloud security posture across AWS, Azure, and Google Cloud with a focus on identity risks, default security gaps, and the uneven adoption of guardrails like IMDSv2, data perimeters, and public access blocks. The study highlights…
-
Darktrace darktrace.com
State Of AI Cybersecurity (2025) - Analyzes the transformative impact of artificial intelligence on the global threat landscape and the corresponding shift in defensive strategies within security operations centers. Key insights reveal that while 89% of CISOs anticipate…
-
Darktrace darktrace.com
Annual Threat Report (2026) - Analyzes the global cyber threat landscape through behavioral analysis and real world customer data from across international regions. Key findings reveal that software as a service and email based social engineering account for nearly 70% of all…
-
Darktrace darktrace.com
The State Of Cybersecurity In The Finance Sector (2025) - Examines the state of cybersecurity in the finance sector, detailing evolving risks to confidentiality, integrity, and availability. Key findings reveal a significant increase in sophisticated phishing techniques like…
-
Darktrace darktrace.com
Remote Workforce Security Report (2026) - Examines the cybersecurity risks and operational challenges introduced by the sudden shift to a remote workforce across global organizations. Key findings reveal that 80% of security professionals are moderately to extremely concerned…
-
Cypress Data Defense cypressdatadefense.com
State of Application Security (2025) - Analyzes the state of application security and its impact on product velocity, revealing significant challenges in detection and integration. Key findings indicate that 62% of companies ship insecure code, 60% experience release delays due…
-
Security alert: social engineering campaign targets technology industry employees github.blog
Phishing GitHub users to download and execute repositories.
-
Cyfirma cyfirma.com
Tracking Ransomware (2026) - Investigates the evolving ransomware landscape in early 2026, highlighting a shift toward user-mediated access, browser-centric exploitation, and psychological coercion over traditional encryption. Data indicates that ransomware activity reached 683…
-
GHTorrent Project ghtorrent-downloads.ewi.tudelft.nl
A queryable offline mirror of the GitHub API data. Tutorial.
-
Cyera cyera.com
State of AI Data Security Reportw. (2025) - Examines the rapid integration of artificial intelligence within enterprise environments and the resulting systemic risks caused by inadequate governance and visibility. Key findings reveal that while 83 percent of organizations have…
-
Dependency Confusions in Docker and remote pwning of your infra errno.fr
Docker dependency confusion occurs when a misconfigured Docker mirror pulls malicious public images instead of private ones.
-
Cyentia cyentia.com
State of HRM Insight Report (2025) - Examines the landscape of human risk management by analyzing over two hundred real-time behavioral and threat signals across more than one hundred organizations. Findings indicate that human risk is highly concentrated, with 10 percent of…
-
Beyond S3: Exposed Resources on AWS duo.com
Public EBS, RDS, AMI and Elasticsearch clusters exposed to the internet.
-
Hacking GitHub AWS integrations again dagrz.com
Attacking misconfigured pipelines that use OIDC.
-
Cyentia cyentia.com
CISO Engagement Study (2025) - Focuses on how cybersecurity buyers engage with AI driven topics, evolving content formats, and shifting sponsor behavior across global regions and industries. The data shows AI dominates user interest, OT security is underserved despite growing…
-
How We Discovered Vulnerabilities in CI/CD Pipelines of Popular Open-Source Projects cycode.com
Extracting all repository and organization secrets in GitHub Actions.
-
Cyentia cyentia.com
Information Risk Insights Study (2025) - Analyzes incident probability and the increasing risks associated with third-party relationships. A key finding is that incident probability has almost quadrupled in the last 15 years, driven in part by threat actors exploiting trusted…
-
Holes in Your Bitbucket: Why Your CI/CD Pipeline Is Leaking Secrets cloud.google.com
Bitbucket Secured Variables leak secrets via artifact objects; recommendations include using dedicated secrets managers and code scanning.
-
Cycode cycode.com
State Of Product Security (2026) - Examines the current state of product security in the era of artificial intelligence, focusing on the rapid adoption of coding assistants and the resulting expansion of the organizational attack surface. Research indicates that while 97…
-
StarJacking – Making Your New Open Source Package Popular in a Snap checkmarx.com
StarJacking is a technique where attackers make malicious open-source packages appear popular.
-
Cycode cycode.com
State of Application Security Posture Management (2025) - Examines application security challenges and strategies from the perspectives of CISOs, AppSec Directors, and DevSecOps managers across the UK, US, and Germany. Key findings reveal inefficiencies strain the relationship…
-
Working as unexpected chainguard.dev
Creating a GitHub branch that matches a branch protection rule pattern with a workflow file that triggers on push to gain access to environment secrets.
-
Cyble cyble.com
Global Threat Landscape (2025) - Analyzes the global threat landscape of H1 2025, highlighting a significant 54% increase in ransomware attacks compared to the previous year. The report identifies CL0P, Akira, and Qilin as the top ransomware operators, with North America being…
-
What the fork? Imposter commits in GitHub Actions and CI/CD chainguard.dev
GitHub Actions vulnerability allows forked commits to bypass workflow security settings.
-
The Cyber Threat Alliance (CTA) cyberthreatalliance.org
An industry-driven group of cybersecurity organizations that share threat intelligence and conduct collaborative research to combat cyber threats.
-
Understanding typosquatting methods - for a secure supply chain bytesafe.dev
Typosquatting involves publishing malicious packages with names similar to legitimate ones, exploiting typos to inject malicious code.
-
Cybersecurityventures cybersecurityventures.com
Cybersecurity Market Report (2026) - Analyzes the global cybersecurity market trajectory and the factors driving record levels of investment across diverse industrial and consumer sectors. Projections indicate that global cybersecurity spending will reach one trillion dollars…
- next page of items loading…