Malware Persistence
57 items from karneades/awesome-malware-persistence ★312
-
Atomic Red Team (ART) github.com
Small and highly portable detection tests mapped to the MITRE ATT&CK Framework.
-
TripleCross github.com
A Linux eBPF rootkit with a backdoor, C2, library injection, execution hijacking, persistence and stealth capabilities.
-
-
-
ebpfkit github.com
A rootkit that leverages multiple eBPF features to implement offensive security techniques.
-
Diamorphine github.com
A loadable kernel module (LKM) rootkit for Linux Kernels (x86/x86_64 and ARM64).
-
PersistenceSniper github.com
Powershell module to hunt for persistence implanted in Windows machines.
-
PANIX github.com
A highly customizable Linux persistence tool. Perform various persistence techniques against Linux systems, among others Debian and RHEL.
-
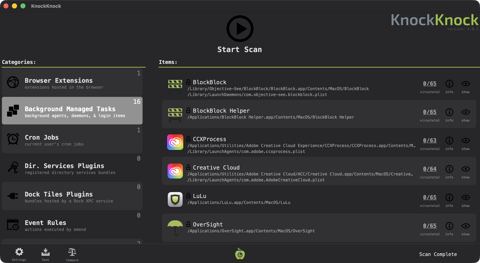
BlockBlock github.com
A tool which provides continual protection by monitoring persistence locations and protects them accordingly. Similar to KnockKnock but for blocking.
-
Linux Security and Monitoring Scripts github.com
Security and monitoring scripts you can use to monitor your Linux installation for security-related events or for an investigation. Among other finding systemd unit files used for malware persistence.
-
-
PyrsistenceSniper github.com
A Python-based offline Windows persistence detection tool. Point it at a KAPE dump, a Velociraptor collection, or a mounted disk image and get offline Windows persistence detection. Runs on Windows, Linux, and macOS.
-
hasherezade persistence demos github.com
Various (also non standard) persistence methods used by malware for testing own detection, among others COM hijacking demo is found in the repo.
-
-
RECmd github.com
Extract various persistence mechanisms, e.g. by using the config file UserClassesASEPs to extract user's CLSID information.
-
PowerSponse github.com
PowerSponse is a PowerShell module focused on targeted containment and remediation during security incident response.
-
-
AWSDoor: Persistence on AWS github.com
Access persistence tool for AWS. The corresponding article describes the techniques adversaries can use to hide themselves within a cloud environment and its AWSDoor implementation to simplify and automate the deployment of persistence techniques in AWS environments.
-
-
Database Triggers as Persistence Mechanisms trustwave.com
An in-depth write up about database triggers providing persistence.
-
theevilbit's series "Beyond the good ol' LaunchAgents" theevilbit.github.io
List of macOS persistence beyond just the LaunchDaemons or LaunchAgents.
-
Autoruns technet.microsoft.com
A powerful persistence collection tool on Windows is Autoruns. It collects different categories and persistence information from a live system and in limited ways from offline images. There is a UI and a command line program and the output format can be set to CSV which can…
-
Hunting for persistence via Microsoft Exchange Server or Outlook speakerdeck.com
Blog post about Microsoft Exchange server persistence.
-
-
MoonBounce: the dark side of UEFI firmware securelist.com
An in-depth write up about one particular UEFI bootkit.
-
Linux Malware Persistence with Cron sandflysecurity.com
Blog post about Linux persistence using cron jobs.
-
-
Common malware persistence mechanisms resources.infosecinstitute.com
Different persistence mechanisms for different vectors are described.
-
-
Persistence – COM Hijacking, 2020 pentestlab.blog
- next page of items loading…