Security
5,347 items in 29 lists
-
Appknox appknox.com
not free
-
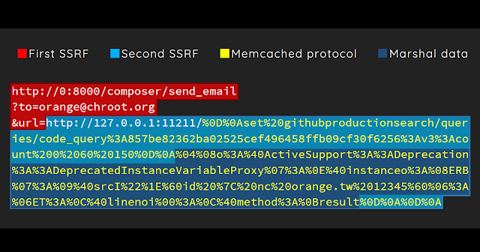
GitHub Enterprise Remote Code Execution bounty.github.com
-
-
App Detonator appdetonator.run
Detonate APK binary to provide source code-level details, including app author, signature, build, and manifest information. 3 Analysis/day free quota.
-
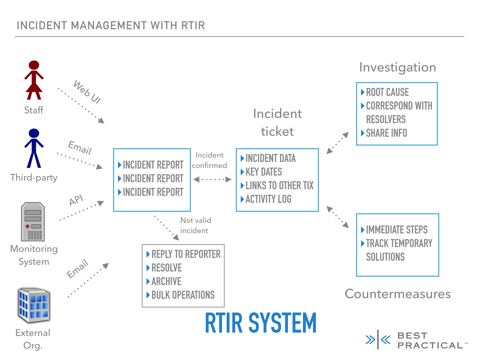
RTIR bestpractical.com
Request Tracker for Incident Response (RTIR) is the premier open source incident handling system targeted for computer security teams. We worked with over a dozen CERT and CSIRT teams around the world to help you handle the ever-increasing volume of incident reports. RTIR…
-
-
AppCritique appcritique.boozallen.com
Upload your Android APKs and receive comprehensive free security assessments
-
SSD Advisory – Chrome Turbofan Remote Code Execution blogs.securiteam.com
-
Taintdroid appanalysis.org
requires AOSP compilation
-
Laravel Content Security Policy: Complete Implementation Guide blog.shakiltech.com
-
Fraunhofer App-ray app-ray.co
expired domain
-
Belkasoft Live RAM Capturer belkasoft.com
Tiny free forensic tool to reliably extract the entire content of the computer’s volatile memory – even if protected by an active anti-debugging or anti-dumping system.
-
Remote Code Execution on a Facebook server blog.scrt.ch
-
NVISO ApkScan apkscan.nviso.be
sunsetting on Oct 31, 2019
-
A Methodical Approach to Browser Exploitation blog.ret2.io
-
Belkasoft Evidence Center belkasoft.com
The toolkit will quickly extract digital evidence from multiple sources by analyzing hard drives, drive images, memory dumps, iOS, Blackberry and Android backups, UFED, JTAG and chip-off dumps.
-
-
Apkpure apkpure.com
Online apk downloader. Also, it provides its own app for downloading.
-
GitHub Enterprise SQL Injection blog.orange.tw
-
APK Downloader apkcombo.com
Online Service to download APK from the Play Store for a specific Android Device Configuration
-
Orange blog.orange.tw
-
Threat.Zone app.threat.zone
Cloud based threat analysis platform which include sandbox, CDR and interactive analysis for researchers.
-
Hacking with JSP Shells blog.netspi.com
-
Anubis anubis.iseclab.org
-
Forcing XXE Reflection through Server Error Messages blog.netspi.com
-
-
HQL for pentesters blog.h3xstream.com
-
Advisory: Java/Python FTP Injections Allow for Firewall Bypass blog.blindspotsecurity.com
-
[dev.twitter.com] XSS blog.blackfan.ru
-
Another XSS in Google Colaboratory blog.bentkowski.info
-
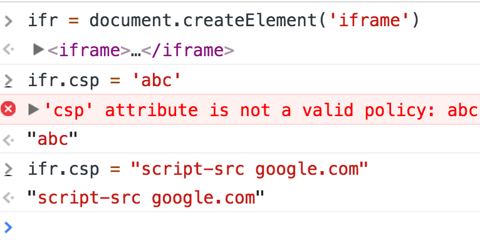
XSS in Google Colaboratory + CSP bypass blog.bentkowski.info
-
Setting arbitrary request headers in Chromium via CRLF injection blog.bentkowski.info
-
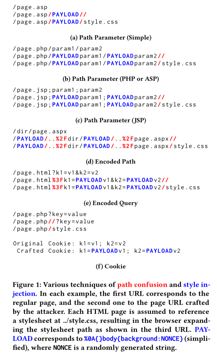
Large-scale analysis of style injection by relative path overwrite blog.acolyer.org
-
0Day Labs blog.0daylabs.com
-
-
-
Bypassing Mobile Browser Security For Fun And Profit blackhat.com
-
The Magic of Learning bitvijays.github.io
-
Cybersecurity Campaign Playbook belfercenter.org
-
-
SSL & TLS Penetration Testing aptive.co.uk
-
DRUPAL 7.X SERVICES MODULE UNSERIALIZE() TO RCE ambionics.io
-
alert(1) to win alf.nu
-
James Kettle albinowax.skeletonscribe.net
-
The 200 That Proved Nothing aivist.dev
-
-
Where the LLM Stops: Deterministic Scoring in an AI-Assisted VAPT Pipeline aayushyadav.hashnode.dev
-
The bug bounty program that changed my life 10degres.net
-
AWS takeover through SSRF in JavaScript 10degres.net
-
An example why NAT is NOT security 0day.work
- next page of items loading…