DON'T TRUST THE DOM: BYPASSING XSS MITIGATIONS VIA SCRIPT GADGETS
- from
- Web Security
- added
- 2026-10-10
- likes
- 0
similar
-
Evading CSP with DOM-based dangling markup portswigger.net
-
CSP: bypassing form-action with reflected XSS labs.detectify.com
-
C.XSS Guide excess-xss.com
-
Cross-Site Scripting attack detection gizra.com
-
-
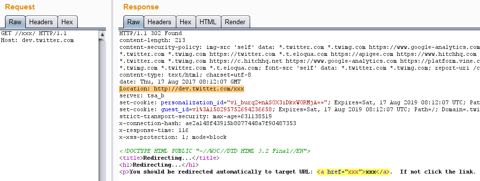
[dev.twitter.com] XSS blog.blackfan.ru
Web Security › Tricks > XSS: “Written by Sebastian Lekies, Krzysztof Kotowicz, and Eduardo Vela.”