Security
5,347 items in 29 lists
-
AWS Security manning.com
This early-access book covers commong AWS security issues and best practices for access policies, data protection, auditing, continuous monitoring, and incident response.
-
API Security in Action manning.com
Book covering API security including secure development, token-based authentication, JSON Web Tokens, OAuth 2, and Macaroons. (early access, published continuously, final release summer 2020)
-
DNS-BH malwaredomains.com
The DNS-BH project creates and maintains a listing of domains that are known to be used to propagate malware and spyware. This project creates the Bind and Windows zone files required to serve fake replies to localhost for any requests to these, thus preventing many spyware…
-
leakedin.com leakedin.com
The primary purpose of leakedin.com is to make visitors aware about the risks of loosing data. This blog just compiles samples of data lost or disclosed on sites like pastebin.com.
-
Kojoney kojoney.sourceforge.net
Kojoney is a low level interaction honeypot that emulates an SSH server. The daemon is written in Python using the Twisted Conch libraries.
-
justniffer justniffer.sourceforge.net
Justniffer is a network protocol analyzer that captures network traffic and produces logs in a customized way, can emulate Apache web server log files, track response times and extract all "intercepted" files from the HTTP traffic.
-
netmap info.iet.unipi.it
netmap is a framework for high speed packet I/O. Together with its companion VALE software switch, it is implemented as a single kernel module and available for FreeBSD, Linux and now also Windows.
-
docker-metasploit hub.docker.com
-
official Kali Linux hub.docker.com
-
OWASP WrongSecrets hub.docker.com
-
Cyware Threat Response Docker hub.docker.com
-
OWASP Juice Shop hub.docker.com
-
Holistic Info-Sec for Web Developers holisticinfosecforwebdevelopers.com
Free and downloadable book series with very broad and deep coverage of what Web Developers and DevOps Engineers need to know in order to create robust, reliable, maintainable and secure software, networks and other, that are delivered continuously, on time, with no nasty…
-
Hardening Windows 10 hardenwindows10forsecurity.com
Guide for hardening Windows 10
-
Glastopf glastopf.org
Glastopf is a Honeypot which emulates thousands of vulnerabilities to gather data from attacks targeting web applications. The principle behind it is very simple: Reply the correct response to the attacker exploiting the web application.
-
Spam Scanner github.com
Anti-Spam Scanning Service and Anti-Spam API by @niftylettuce.
-
Anevicon github.com
The most powerful UDP-based load generator, written in Rust.
-
Scanmycode CE (Community Edition) github.com
Code Scanning/SAST/Static Analysis/Linting using many tools/Scanners with One Report. Currently supports: PHP, Java, Scala, Python, Ruby, Javascript, GO, Secret Scanning, Dependency Confusion, Trojan Source, Open Source and Proprietary Checks (total ca. 1000 checks)
-
TorForge github.com
Advanced transparent Tor proxy with kernel-level iptables routing, post-quantum encryption (Kyber768), kill switch, steganography mode, and AI-powered circuit selection.
-
Curiefense github.com
Curiefense adds a broad set of automated web security tools, including a WAF to Envoy Proxy.
-
Stealth fbb-git.gitlab.io
File integrity checker that leaves virtually no sediment. Controller runs from another machine, which makes it hard for an attacker to know that the file system is being checked at defined pseudo random intervals over SSH. Highly recommended for small to medium deployments.
-
Fail2Ban fail2ban.org
Scans log files and takes action on IPs that show malicious behavior.
-
PACKET_MMAP/TPACKET/AF_PACKET elixir.bootlin.com
It's fine to use PACKET_MMAP to improve the performance of the capture and transmission process in Linux.
-
httpry dumpsterventures.com
httpry is a specialized packet sniffer designed for displaying and logging HTTP traffic. It is not intended to perform analysis itself, but to capture, parse, and log the traffic for later analysis. It can be run in real-time displaying the traffic as it is parsed, or as a…
-
T-Pot Honeypot Distro dtag-dev-sec.github.io
T-Pot is based on the network installer of Ubuntu Server 16/17.x LTS. The honeypot daemons as well as other support components being used have been containerized using docker. This allows us to run multiple honeypot daemons on the same network interface while maintaining a…
-
Internet Storm Center dshield.org
The ISC was created in 2001 following the successful detection, analysis, and widespread warning of the Li0n worm. Today, the ISC provides a free analysis and warning service to thousands of Internet users and organizations, and is actively working with Internet Service…
-
DrKeithJones.com drkeithjones.com
A blog on cyber security and network security monitoring.
-
Emerging Threats - Open Source doc.emergingthreats.net
Emerging Threats began 10 years ago as an open source community for collecting Suricata and SNORT® rules, firewall rules, and other IDS rulesets. The open source community still plays an active role in Internet security, with more than 200,000 active users downloading the…
-
Denyhosts denyhosts.sourceforge.net
Thwart SSH dictionary based attacks and brute force attacks.
-
Cyware Threat Intelligence Feeds cyware.com
Cyware’s Threat Intelligence feeds brings to you the valuable threat data from a wide range of open and trusted sources to deliver a consolidated stream of valuable and actionable threat intelligence. Our threat intel feeds are fully compatible with STIX 1.x and 2.0, giving you…
-
Best Linux Penetration Testing Distributions @ CyberPunk cyberpunk.rs
Description of main penetration testing distributions
-
Conpot conpot.org
ICS/SCADA Honeypot. Conpot is a low interactive server side Industrial Control Systems honeypot designed to be easy to deploy, modify and extend. By providing a range of common industrial control protocols we created the basics to build your own system, capable to emulate…
-
How to Hack Like a Pornstar books2read.com
A step by step process for breaking into a BANK, Sparc Flow, 2017
-
How to Investigate Like a Rockstar books2read.com
Live a real crisis to master the secrets of forensic analysis, Sparc Flow, 2017
-
Security Onion blog.securityonion.net
Security Onion is a Linux distro for intrusion detection, network security monitoring, and log management. It's based on Ubuntu and contains Snort, Suricata, Zeek, OSSEC, Sguil, Squert, Snorby, ELSA, Xplico, NetworkMiner, and many other security tools. The easy-to-use Setup…
-
AlienVault Open Threat Exchange alienvault.com
AlienVault Open Threat Exchange (OTX), to help you secure your networks from data loss, service disruption and system compromise caused by malicious IP addresses.
-
Live HTTP headers addons.mozilla.org
Live HTTP headers is a free firefox addon to see your browser requests in real time. It shows the entire headers of the requests and can be used to find the security loopholes in implementations.
-
abuse.ch abuse.ch
ZeuS Tracker / SpyEye Tracker / Palevo Tracker / Feodo Tracker tracks Command&Control servers (hosts) around the world and provides you a domain- and an IP-blocklist.
-
FinAgent Red-Team: A Benchmark for Regulatory-Control Bypass in Financial LLM Agents github.com
Aug 2026 benchmark measuring whether indirect prompt injection can drive financial LLM agents past regulatory controls (sanctions screening, payment-structuring thresholds, dual-approval, data exfiltration, confused-deputy payee redirection). Replays 48 scenarios under three…
-
Comparison of Consent Management Platforms github.com
-
Rhme-2017/2018 github.com
Riscure Hack Me 3 embedded hardware CTF 2017-2018.
-
Rhme-2015 github.com
First riscure Hack me hardware CTF challenge.
-
XVolkolak github.com
Qt/CMake emulator-unpacker project with a GUI and a console application.
-
HimitsuShell github.com
A shell script protector that converts shell scripts into binaries with an embedded interpreter, obfuscation, and anti-debug protections (shc alternative).
-
Packing induced bias in deep learning malware classifiers: A systematic experimental study ieeexplore.ieee.org
(February 2026)
-
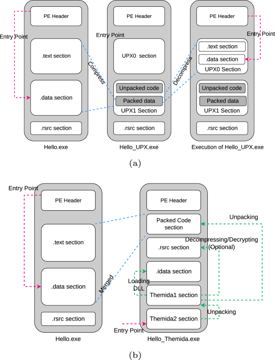
A packer identification method based on section-entropy plot link.springer.com
(February 2026) :star:
-
Security Monitoring Labs | cybersecurity101.net cybersecurity101.net
48 free, step-by-step labs that build a small Wazuh monitoring stack on your own VMs, connect Linux and Windows (Sysmon) log sources, then write and tune detection rules, test them with simulated events, triage alerts and report on coverage. No account or hosted platform.
-
Clankerusecase clankerusecase.com
Threat-led library of 7,800+ MITRE ATT&CK-mapped detections in Defender/Sentinel KQL, Sigma, Splunk SPL, Datadog, Falcon LogScale, and AWS CloudWatch, generated from public threat-intel reporting and schema-validated before publish.
-
Ridgeline Detection Library github.com
Production-validated detections across nine platforms (KQL, Sigma, Splunk, Athena, PowerShell, Velociraptor, YARA, Suricata, osquery), each with triggers, false positives, tuning guidance, and validation steps. Apache-2.0.
-
Control Assurance Lab | Gyubin Lee github.com
Runs reproducible matched-intervention experiments that distinguish target-control failures from failures masked by downstream safeguards.
- next page of items loading…