OpenID Connect
178 items from cerberauth/awesome-openid-connect ★131
-
Proof Key for Code Exchange (PKCE) Extension datatracker.ietf.org
Extension of the Authorization Code flow adding security layer against code interception attack.
-
OAuth 2.0 Dynamic Client Registration Management Protocol datatracker.ietf.org
Endpoints for management of OAuth 2.0 dynamic client registrations.
-
OAuth 2.0 Dynamic Client Registration Protocol datatracker.ietf.org
Defines how an OAuth 2.0 Relying Party (RP) can dynamically register with the OAuth 2.0 server provider.
-
urn:ietf:params:oauth:grant-type:jwt-bearer datatracker.ietf.org
JSON Web Token (JWT) Profile for OAuth 2.0 used to authorize a client to get an access token with another JWT issued by a trusted provider.
-
urn:ietf:params:oauth:grant-type:saml2-bearer datatracker.ietf.org
Security Assertion Markup Language (SAML) 2.0 Profile for OAuth 2.0 used to authorize a client to get an access token with a SAML assertion issued by a trusted provider.
-
JSON Web Token (JWT) datatracker.ietf.org
JWT specifications used for different tokens mentioned in OAuth 2.0 and OpenID Connect specifications.
-
JSON Web Key (JWK) datatracker.ietf.org
JavaScript Object Notation (JSON) data structure that represents a cryptographic key provided by OpenID Connect Provider.
-
JSON Web Encryption (JWE) datatracker.ietf.org
Specifications for JWE which represents encrypted content using JSON-based data structures.
-
JSON Web Signature (JWS) datatracker.ietf.org
Specifications for JWS which represents content secured with digital signatures.
-
OAuth 2.0 Token Revocation datatracker.ietf.org
Endpoint for OAuth authorization servers which allows clients to notify the authorization server that a previously obtained refresh or access token is no longer needed.
-
OAuth 2.0 Threat Model and Security Considerations datatracker.ietf.org
Known threats using OAuth 2.0 / OpenID Connect and countermeasures.
-
OAuth 2.0 Authorization Framework: Bearer Token Usage datatracker.ietf.org
Describes how to use bearer tokens in HTTP requests to access OAuth 2.0 protected resources.
-
refresh_token datatracker.ietf.org
OAuth 2.0 Refresh Token Grant Type used to exchange a refresh token against a short life access token and sometime a new refresh token as well.
-
password datatracker.ietf.org
OAuth 2.0 Resource Owner Password Credentials Grant Type which is not recommended to use anymore.
-
implicit datatracker.ietf.org
OAuth 2.0 Implicit Grant Type which is deprecated and should not be used anymore.
-
client_credentials datatracker.ietf.org
OAuth 2.0 Client Credentials Grant providing a way to get token without user interaction which fit well machine to machine communications.
-
authorization_code datatracker.ietf.org
OAuth 2.0 Authorization Code Grant Type which fit well public client authorization like web apps.
-
The OAuth 2.0 Authorization Framework datatracker.ietf.org
Underlying OAuth 2.0 protocol OpenID Connect is based on.
-
OpenID Connect Standard Claims Registration for CBOR Web Tokens datatracker.ietf.org
Defines how to represent the OpenID Connect standard claims in CBOR Web Tokens (CWTs).
-
OAuth 2.1 datatracker.ietf.org
Consolidation of OAuth 2.0 specifications into a single document, removing deprecated features and clarifying best practices.
-
Selective Disclosure for JWTs (SD-JWT) datatracker.ietf.org
Specification for selective disclosure of JWT elements.
-
OAuth Identity and Authorization Chaining Across Domains datatracker.ietf.org
Preserves user identity, authorization context, and call-chain history across multiple services and trust domains using OAuth token exchange and JWT-based assertions.
-
Cross-App Access (XAA), formally known as the "Identity Assertion Authorization Grant" datatracker.ietf.org
Enables AI agents and apps to securely access and act across multiple services with user consent using standardized and fine-grained OAuth permissions.
-
OAuth 2.0 for First-Party Applications datatracker.ietf.org
Defines the Authorization Challenge Endpoint to enable native applications to obtain user authorization through native user interfaces.
-
OAuth Client ID Metadata Document datatracker.ietf.org
Mechanism through which an OAuth client can identify itself to authorization servers, without prior dynamic client registration or other existing registration.
-
OAuth 2.0 for Browser-Based Apps datatracker.ietf.org
Security and usability best practice for OAuth usage in Browser-based apps.
-
OAuth 2.0 Attestation-Based Client Authentication datatracker.ietf.org
Extension to OAuth 2.0 enabling public clients to authenticate using key-bound attestations.
-
CyberArk Identity cyberark.com
Identity security solution that provides OpenID Connect Provider capabilities.
-
Curity Resources curity.io
Curity solution resources articles about OpenID Connect.
-
Curity Identity Server curity.io
API Security solution that brings identity and API access management together.
-
Connect2id connect2id.com
OpenID Connect SSO and IdP server for enterprise.
-
Cloudentity cloudentity.com
Cloud Identity and Authorization Platform with FAPI and eKYC support.
-
CerberAuth cerberauth.com
A blog talking about OpenID Connect and OAuth 2.0.
-
SiteMinder broadcom.com
An IAM provided by Broadcom with OpenID Connect Provider support.
-
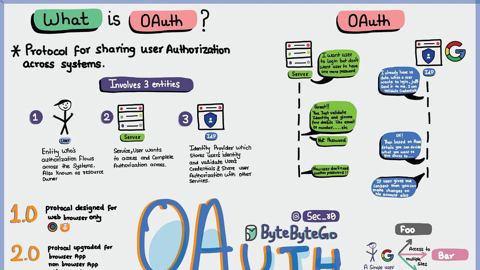
ByteByteGo blog.bytebytego.com
Oauth 2.0 explains using visual and simple terms.
-
Authlete authlete.com
Set of APIs for developers to implement OAuth authorization servers and OpenID Connect identity providers.
-
Authelia authelia.com
Open Source authentication, authorization server and portal fulfilling the identity and access management (IAM) role of information security in providing single sign-on (SSO).
-
Auth0 auth0.com
OpenID Connect and OAuth 2.0 service that is available on the cloud as a SaaS.
-
OpenID Connect for Agents (OIDC-A) 1.0 arxiv.org
A research proposal (not a standard or IETF draft) extending OpenID Connect to support AI agent identity, attestation, delegation chains, and fine-grained authorization within the OAuth ecosystem.
-
Apache APISIX openid-connect apisix.apache.org
OpenID Connect Relying Party plugin for the Apache APISIX API Gateway.
-
-
2018 - OAuth 2.0 Simplified by Aaron Parecki amazon.com
-
-
-
Alibaba Cloud IDaaS alibabacloud.com
Alibaba Cloud OpenID Connect Provider as a service.
-
Alex Bilbie alexbilbie.github.io
Blog posts about OAuth 2.0 topic.
-
Aaron Parecki aaronparecki.com
OAuth WG Member blog posts about OAuth 2.0.
-
OAuth for Model Context Protocol aaronparecki.com
Aaron Parecki article about how OAuth works and how it should be used in the context of model context protocol (MCP) server.