urn:ietf:params:oauth:grant-type:saml2-bearer
Security Assertion Markup Language (SAML) 2.0 Profile for OAuth 2.0 used to authorize a client to get an access token with a SAML assertion issued by a trusted provider.
- from
- OpenID Connect
- added
- 2026-10-10
- likes
- 0
similar
-
urn:ietf:params:oauth:grant-type:jwt-bearer datatracker.ietf.org
JSON Web Token (JWT) Profile for OAuth 2.0 used to authorize a client to get an access token with another JWT issued by a trusted provider.
-
SAML vs. OAuth web.archive.org
“OAuth is a protocol for authorization: it ensures Bob goes to the right parking lot. In contrast, SAML is a protocol for authentication, or allowing Bob to get past the guardhouse.”
-
The Difference Between SAML 2.0 and OAuth 2.0 ubisecure.com
“Even though SAML was actually designed to be widely applicable, its contemporary usage is typically shifted towards enterprise SSO scenarios. On the other hand, OAuth was designed for use with applications on the Internet, especially for delegated authorisation.”
-
OAuth 2.0 Authorization Server Metadata datatracker.ietf.org
A metadata format that an OAuth 2.0 client can use to obtain the information needed to interact with an OAuth 2.0 authorization server.
-
JSON Web Token (JWT) Profile for OAuth 2.0 Access Tokens datatracker.ietf.org
JWT format and validation specifications in the context of OAuth 2.0.
-
urn:ietf:params:oauth:grant-type:token-exchange datatracker.ietf.org
OAuth 2.0 Token Exchange is a Grant Type which provides a way to get tokens from another token and give the ability to add an actor claim.
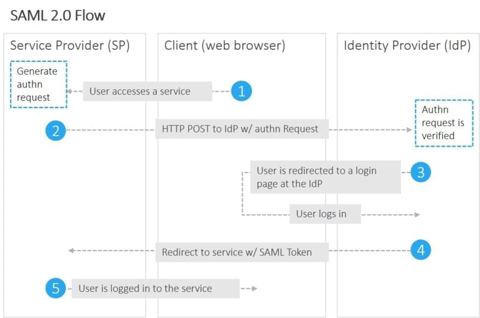
OpenID Connect › Resources > Flows / Grant Types Specifications: “Security Assertion Markup Language (SAML) 2.0 Profile for OAuth 2.0 used to authorize a client to get an access token with a SAML assertion issued by a trusted provider.”