Malware Persistence
57 items from karneades/awesome-malware-persistence ★313
-
osquery osquery.readthedocs.io
Query persistence mechanisms on clients.
-
Persistence using GlobalFlags in Image File Execution Options – Hidden from Autoruns.exe oddvar.moe
Blog post about abusing GlobalFlag for process execution.
-
Shadow Linking: The Persistence Vector of SaaS Identity Threat obsidiansecurity.com
Abuse of additional identity providers to persist in an environment.
-
Removing Backdoors – Powershell Empire Edition n00py.io
Various blog posts handle the removal of WMI implants.
-
Detecting & Removing an Attacker's WMI Persistence medium.com
Blog post about detecting and removing WMI persistence.
-
Linux Red Team Persistence Techniques linode.com
List of persistence techniques.
-
KAPE kroll.com
The tool allows collecting various predefined artifactgs using targets and modules, see KapeFiles which include persistence mechanisms, among others there's a collection of LNK files, scheduled task files and scheduled task listing or a WMI repository auditing module.
-
Hexacorn's blog hexacorn.com
Blog series "Beyond good ol' Run key" covering a lot of Windows persistence mechanisms.
-
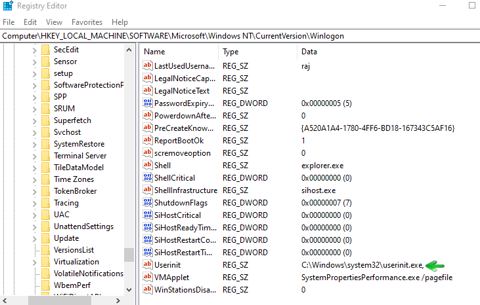
Windows Persistence using WinLogon hackingarticles.in
Blog post about abusing WinLogon.
-
AutorunsToWinEventLog.ps1 github.com
Instead of using CSV output and copy these file to the server, you can use the AutorunsToWinEventLog script to convert the Autoruns output to Windows event logs and rely on standard Windows event log forwarding.
-
PowerShell implementation of Autoruns github.com
Another way to find Windows persistence locations is to look at the source code of the PowerShell version of Autoruns. Bonus: A history of the covered persistence locations for each Autoruns version is found at the end of the module file too, which is so awesome!
-
KnockKnock github.com
A persistence detection tool for macOS to scan for persistence mechanisms on macOS. Specific persistence locations are found in the plugins folder, e.g. LaunchItems or StartupScripts.
-
Sigma rules github.com
Repository of detection rules, covering persistence techniques as well. You can even use filters such as --filter tag=attack.persistence or specifically for one technique tag=attack.t1084.
-
RegRipper github.com
Extracts various persistence mechanisms from the registry files directly.
-
PoisonApple github.com
Learn about various macOS persistence techniques by looking at the source code of PoisonApple.
-
PANIX - Persistence Against *NIX - Features github.com
List of persistence techniques.
-
COM Object hijacking: the discreet way of persistence, 2014 gdatasoftware.com
-
-
Linux Detection Engineering - A primer on persistence mechanisms elastic.co
List of Linux persistence mechanisms.
-
RegDelNull docs.microsoft.com
Removal of registry keys with null bytes - used e.g. in run keys for evasion.
-
Autoruns docs.microsoft.com
You can learn which Windows persistence mechanisms are checked by looking at the output of Autoruns on your own client. Categories and the different locations where things were found are seen in the output. A disassembly of Autoruns lists a subset of the entries which are…
-
Persisting on Entra ID applications and User Managed Identities with Federated Credentials dirkjanm.io
Persist on Entra ID applications and User Managed Identities with Federated Credentials.
-
Borrowing Windows Hello keys for authentication and persistence dirkjanm.io
Ability to perform single-sign on with the backing cryptographic Windows Hello keys from a user session, without needing the PIN or other information/user presence.
-
Uncovering a MyKings Variant With Bootloader Persistence via Managed Detection and Response blog.trendmicro.com
Blog post about bootloader persistence.
-
Untangling Kovter's persistence methods blog.malwarebytes.com
Blog post about Kovter's persistens methos, among others, hiding in registry. Another one is Threat Spotlight: Kovter Malware Fileless Persistence Mechanism.
-
MITRE ATT&CK tactic "TA0003 - Persistence" attack.mitre.org
Persistence tactic information in the MITRE ATT&CK framework.
-
Malware persistence techniques andreafortuna.org
Good summary of multiple persistence mechanisms, ranging from multiple registry keys to more advanced one, like COM hijacking.