AutorunsToWinEventLog.ps1
Instead of using CSV output and copy these file to the server, you can use the AutorunsToWinEventLog script to convert the Autoruns output to Windows event logs and rely on standard Windows event log forwarding.
- from
- Malware Persistence
- added
- 2026-10-10
- likes
- 0
similar
-
Autoruns technet.microsoft.com
A powerful persistence collection tool on Windows is Autoruns. It collects different categories and persistence information from a live system and in limited ways from offline images. There is a UI and a command line program and the output format can be set to CSV which can…
-
PowerShell implementation of Autoruns github.com
Another way to find Windows persistence locations is to look at the source code of the PowerShell version of Autoruns. Bonus: A history of the covered persistence locations for each Autoruns version is found at the end of the module file too, which is so awesome!
-
PowerShell Autoruns github.com
A PowerShell version of Autoruns.
-
Autoruns docs.microsoft.com
You can learn which Windows persistence mechanisms are checked by looking at the output of Autoruns on your own client. Categories and the different locations where things were found are seen in the output. A disassembly of Autoruns lists a subset of the entries which are…
-
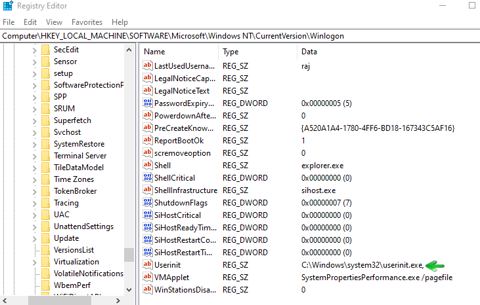
Windows Persistence using WinLogon hackingarticles.in
Blog post about abusing WinLogon.
-
Windows Events (by Emperor) autoitscript.com
Malware Persistence › Collection > Windows: “Instead of using CSV output and copy these file to the server, you can use the AutorunsToWinEventLog script to convert the Autoruns output to Windows event logs and rely on standard Windows event log forwarding.”