eBPF
251 items from zoidbergwill/awesome-ebpf ★5,181
-
P4_16 backend for eBPF github.com
-
OvS Orbit episode (#11), called P4 on the Edge ovsorbit.org
Related to the former item. Audio interview of John Fastabend by Ben Pfaff, one of the core maintainers of Open vSwitch.
-
wachy rubrikinc.github.io
A tracing profiler that aims to make eBPF uprobe-based debugging easier to use. This is done by displaying traces in a UI next to the source code and allowing interactive drilldown analysis.
-
bpf_jit_disasm git.kernel.org
A disassembler for both BPF flavors and could be highly useful for JIT debugging.
-
bpf_dbg git.kernel.org
A small debugger for cBPF programs.
-
bpf_asm git.kernel.org
A minimal cBPF assembler.
-
bpftool git.kernel.org
Also some other tools in the kernel tree, under linux/tools/net/ for versions earlier than 4.15, or linux/tools/bpf/ after that:
-
libbpf git.kernel.org
A C library used for handling BPF objects (programs and maps), and manipulating ELF object files containing them. It is shipped with the kernel and mirrored on GitHub.
-
this commit reviews.llvm.org
.
-
iproute2-next git.kernel.org
The development tree, synchronised with net-next.
-
iproute2 git.kernel.org
Package containing tools for network management on Linux. In particular, it contains tc, used to manage eBPF filters and actions, and ip, used to manage XDP programs. Most of the code related to BPF is in lib/bpf.c.
-
Lua front-end for BCC github.com
Another alternative to C, and even to most of the Python code used in bcc.
-
redbpf examples github.com
Example programs for using RedBPF to write eBPF programs in Rust.
-
bcc/tools github.com
These tools themselves can be seen as example use cases for BPF programs, mostly for tracing and monitoring. bcc tools have been packaged for some Linux distributions.
-
bcc/examples github.com
Examples coming along with the bcc tools, mostly about tracing.
-
iproute2/examples/bpf/ git.kernel.org
Some networking programs to attach to the TC interface.
-
prototype-kernel/kernel/samples/bpf github.com
Jesper Dangaard Brouer's prototype-kernel repository contains some additional examples that can be compiled outside of kernel infrastructure.
-
linux/tools/testing/selftests/bpf git.kernel.org
In the kernel tree: Linux BPF selftests, with many eBPF programs.
-
linux/samples/bpf/ git.kernel.org
In the kernel tree: some sample eBPF programs.
-
ebpf.io labs ebpf.io
List of community developed labs.
-
Inspektor Gadget - Hello world gadget with Wasm inspektor-gadget.io
An introductory guide to writing image-based eBPF gadgets and performing post-processing with WASM.
-
Inspektor Gadget - Hello world gadget inspektor-gadget.io
An introductory guide to writing image-based eBPF gadgets and sharing them via OCI registries.
-
Writing a basic continuous profiler blog.maxgio.me
A step-by-step guide to write an appliation continuous profiler leveraging the eBPF instrumentation, with a complete project as a reference.
-
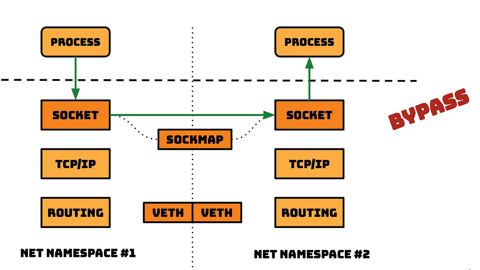
Accelerating Local Socket Communication using eBPF cloudchirp.substack.com
Learn how eBPF can speed-up local socket communication up to 30%.
-
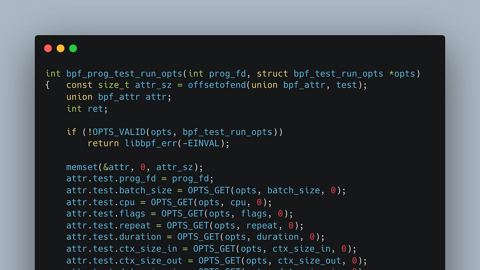
Unit Testing eBPF Programs ebpfchirp.substack.com
Learn how you can unit test your eBPF programs using libbpf.
-
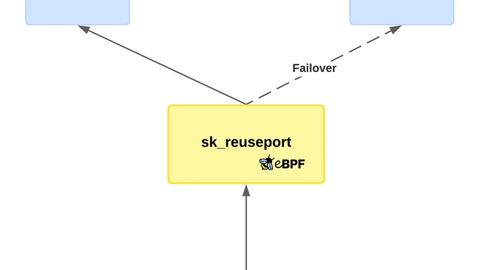
eBPF-Powered Load Balancing cloudchirp.substack.com
Learn how eBPF can infer custom load-balancing for services listening on the same port, through the SO_REUSEPORT TCP option.
-
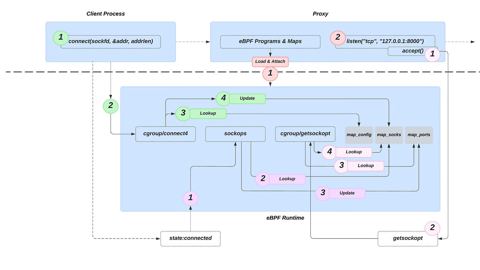
Transparent Proxy Implementation using eBPF and Go cloudchirp.substack.com
A step-by-step guide on how to implement a transparent proxy using eBPF.
-
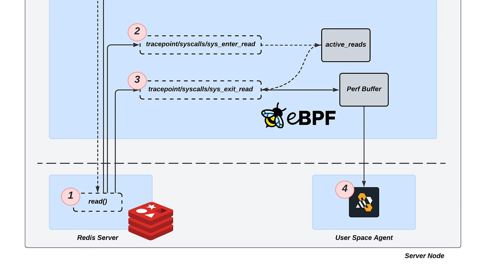
Can eBPF Detect Redis Message Patterns Before They Become Problems? cloudchirp.substack.com
A step-by-step guide how eBPF can observe Redis communication between client and server.
-
What Insights Can eBPF Provide into Real-Time SSL/TLS Encrypted Traffic and How? cloudchirp.substack.com
A step-by-step guide how eBPF can observe encrypted network traffic.
-
Loops and Iterators in eBPF cloudchirp.substack.com
Newsletter about all the ways to loop and iterate in eBPF.
-
Catch Performance Regressions in eBPF bencher.dev
A step-by-step guide to benchmarking both the client and kernel eBPF code written in Rust.
-
eBPF Developer Tutorial - Learn eBPF by examples eunomia.dev
Start with eBPF basics and progress to advanced topics using 20+ hands-on tutorials and examples. Covers performance, networking, and security with libbpf and CO-RE. Available in Chinese and English.
-
A Deep Dive into eBPF: Writing an Efficient DNS Monitoring. medium.com
A detailed explanation of methods used to capture DNS requests at the socket filter layer.
-
Firewalling with BPF/XDP: Examples and Deep Dive arthurchiao.art
A simple guide to build basic firewalls with TC and XDP.
-
All your tracing are belong to BPF blog.trailofbits.com
A step-by-step walkthrough to integrate tracing capabilities in your C++ applications with the LLVM libraries.
-
XDP for the Rest of Us netdevconf.org
Second edition, with new contents.
-
Open NFP platform open-nfp.org
Operated by Netronome: some tutorials for network-related eBPF use cases, including an eBPF Offload Starting Guide.
-
Tracing a packet journey using Linux tracepoints, perf and eBPF blog.yadutaf.fr
Troubleshooting ping requests and replies with perf and bcc programs.
-
How I ended up writing opensnoop in pure C using eBPF bolinfest.github.io
A thorough walk-through of how to write eBPF programs, first using only bpf() syscall, and then libbpf library, with reproducible code examples.
-
Building BPF applications with libbpf-bootstrap nakryiko.com
Helps generate minimal or advanced templates to bootstrap your own applications (kernel side and user space management for maps and programs) with features like CO-RE, global variables, and ring buffer.
-
bcc Python Developer Tutorial github.com
Comes with bcc, but targets the Python bits across seventeen "lessons".
-
eBPF Party ebpf.party
Browser-based playground to learn, write, compile, and run eBPF programs.
-
Delilah: eBPF-offload on Computational Storage dl.acm.org
Delilah is a Computational Storage Processor (CSP) built for eBPF offload to storage devices.
-
Comprehensive XDP offload---Handling the edge cases netdevconf.org
An update on the topic above.
-
eBPF/XDP hardware offload to SmartNICs netdevconf.org
Hardware offload for eBPF with TC or XDP (Linux kernel 4.9+), introduced by Netronome.
-
Libpcap filters syntax biot.com
-
Introducing Cloudflare's BPF Tools blog.cloudflare.com
Usage of BPF bytecode with the xt_bpf module for iptables.
-
-
Linux' packet mmap(2), BPF, and Netsniff-NG borkmann.ch
-
The FreeBSD manual page about BPF freebsd.org
- next page of items loading…