eBPF
251 items from zoidbergwill/awesome-ebpf ★5,181
-
The BSD Packet Filter: A New Architecture for User-level Packet Capture tcpdump.org
The original paper about (classic) BPF.
-
What is BTF (BPF Type Format) cloudchirp.substack.com
A community-authored newsletter enriched with useful code illustrations and hands-on examples.
-
Enhancing the Linux kernel with BTF type information facebookmicrosites.github.io
A description of the work done with BTF to provide debugging information for BPF programs.
-
BPF Type Format (BTF) kernel.org
Kernel documentation about BTF, explaining how to use it.
-
Fast Packet Processing in Linux with AF_XDP archive.fosdem.org
-
AF_XDP kernel.org
Kernel documentation on the AF_XDP address family.
-
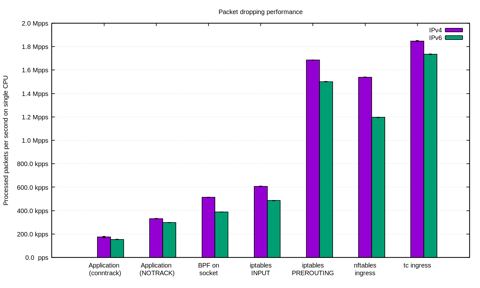
How to drop 10 million packets per second blog.cloudflare.com
Cloudflare's blog post talking about their move to using XDP for packet filtering.
-
High Speed Packet Filtering on Linux cdn.shopify.com
About packet filtering on Linux, DDoS protection, packet processing in the kernel, kernel bypass, XDP and eBPF.
-
-
XDP now with REDIRECT people.netfilter.org
Update on XDP, and in particular on the redirect actions.
-
XDP for the Rest of Us netdevconf.org
How to get started with eBPF and XDP for normal humans. Also summarized by Julia Evans on her blog.
-
Memory vs. Networking, Provoking and fixing memory bottlenecks people.netfilter.org
Advanced details about current memory issues faced by XDP developers.
-
XDP – eXpress Data Path, Used for DDoS protection people.netfilter.org
Details and use cases about XDP, with benchmark results, and code snippets for benchmarking as well as for basic DDoS protection with eBPF/XDP (based on an IP blacklisting scheme).
-
Network Performance Workshop netdevconf.org
Additional hints about XDP internals and expected evolution.
-
XDP − eXpress Data Path, Intro and future use-cases people.netfilter.org
Linux Kernel's fight against DPDK. Future plans (as of this writing) for XDP and comparison with DPDK.
-
eXpress Data Path slideshare.net
Contains some benchmark results obtained with the mlx4 driver.
-
eXpress Data Path (XDP) github.com
The first presentation about XDP.
-
XDP Project overview iovisor.org
-
Work-in-progress documentation for XDP prototype-kernel.readthedocs.io
-
The eXpress Data Path blogs.igalia.com
A very accessible introduction to XDP, providing sample code to show how to process packets.
-
Linux BPF Superpowers brendangregg.com
article.
-
Linux Kernel Tracing slideshare.net
Systemtap, Kernelshark, trace-cmd, LTTng, perf-tool, ftrace, hist-trigger, perf, function tracer, tracepoint, kprobe/uprobe, and more.
-
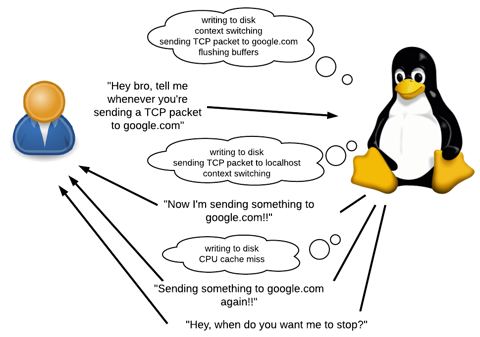
Meet-cute between eBPF and Kernel Tracing slideshare.net
Kprobes, uprobes, ftrace.
-
Full-system dynamic tracing on Linux using eBPF and bpftrace joyfulbikeshedding.com
A detailed introduction to tracing with eBPF, from listing the available trace points to running bpftrace programs.
-
Linux Networking Explained slideshare.net
Linux networking internals, with a part about eBPF.
-
Linux tc and eBPF archive.fosdem.org
-
On getting tc classifier fully programmable with cls_bpf netdevconf.org
Introduction to eBPF, including several features (map management, tail calls, verifier). The full paper is also available here.
-
cls_bpf/eBPF updates since netdev 1.1 netdevconf.org
Part of this tc workshop.
-
Advanced programmability and recent updates with tc's cls_bpf netdevconf.org
Details on eBPF, its use for tunneling and encapsulation, direct packet access, and more.
-
-
ebpf.io blog ebpf.io
Links to many community blogs posts.
-
Linux Extended BPF (eBPF) Tracing Tools brendangregg.com
An in-depth collection of information around examples of performance analysis tools using eBPF. Contains also a section at the end of the page about other resources.
-
Cloudflare's blog posts on eBPF blog.cloudflare.com
Different blog posts about networking use cases and low-level aspects of eBPF.
-
eBPF - From a Programmer's Perspective researchgate.net
A short paper describing the fundamentals of eBPF and how to get started with writing eBPF programs.
-
Linux Kernel Observability through eBPF sematext.com
A blog post covering the basics of eBPF as well as code samples in Go on how to build and load a minimal eBPF program into the kernel.
-
Using BPF to do Packet Transformation blogs.oracle.com
One eBPF usage about packet transformation.
-
The BPF Bytecode and the BPF Verifier blogs.oracle.com
How does BPF ensure that programs are safe?
-
Building BPF Programs blogs.oracle.com
Setting up your environment to build BPF programs.
-
Communicating with Userspace blogs.oracle.com
How BPF communicates with userspace - BPF maps, perf events, bpf_trace_printk.
-
BPF helper functions blogs.oracle.com
A review of the kernel functions that can be called from within eBPF programs.
-
A Tour of Program Types blogs.oracle.com
A description of all existing hooks for BPF program types, and of their interest.
-
Extending extended BPF lwn.net
A blog post from 2014 on the development of BPF and demonstrating what can be done with it, using an example of stateful socket filtering by attaching an eBPF program to a socket.
-
BPF -- in-kernel virtual machine vger.kernel.org
Presentation by the author of eBPF.
-
IO Visor socallinuxexpo.org
Also introduces IO Visor project.
-
Linux BPF Superpowers slideshare.net
An introduction mostly covering the tracing aspects, first part with flame graphs.
-
BPF: tracing and more slideshare.net
An introduction mostly covering the tracing aspects.
-
The BSD Packet Filter speakerdeck.com
An introduction mostly covering the tracing aspects.
-
A BPF reference guide github.com
About BPF C and bcc Python helpers, from bcc repository.
-
Part 2: Syscall and Map Types ferrisellis.com
-
Part 1: Past, Present, and Future ferrisellis.com
- next page of items loading…