A Deep Dive into eBPF: Writing an Efficient DNS Monitoring.
A detailed explanation of methods used to capture DNS requests at the socket filter layer.
- from
- eBPF
- added
- 2026-10-10
- likes
- 0
similar
-
The BSD Packet Filter: A New Architecture for User-level Packet Capture tcpdump.org
The original paper about (classic) BPF.
-
DEEP-mon slideshare.net
Helps with measuring power consumption for servers and uses eBPF programs for in-kernel aggregation of data.
-
Extending extended BPF lwn.net
A blog post from 2014 on the development of BPF and demonstrating what can be done with it, using an example of stateful socket filtering by attaching an eBPF program to a socket.
-
-
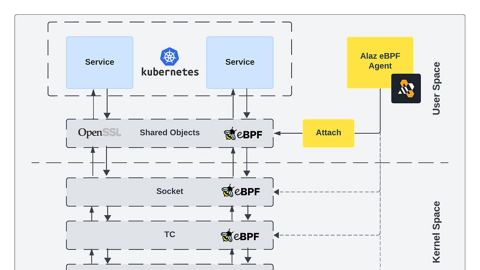
What Insights Can eBPF Provide into Real-Time SSL/TLS Encrypted Traffic and How? cloudchirp.substack.com
A step-by-step guide how eBPF can observe encrypted network traffic.
-
eBPF › Tutorials: “A detailed explanation of methods used to capture DNS requests at the socket filter layer.”