Back-End Development
4,701 items in 32 lists
-
RFC #4122: UUID - Security Considerations rfc-editor.org
“Do not assume that UUIDs are hard to guess; they should not be used as security capabilities (identifiers whose mere possession grants access)”. UUIDs are designed to be unique, not to be random or unpredictable: do not use UUIDs as a secret.
-
The despair and darkness of people will get to you restofworld.org
Moderation of huge social networks is performed by an army of outsourced subcontractors. These people are exposed to the worst and generally ends up with PTSD.
-
An AWS IAM Security Tooling Reference ramimac.me
A comprehensive list of (maintained) tools for AWS IAM.
-
The new NIST password guidance pciguru.wordpress.com
A summary of NIST Special Publication 800-63B covering new password complexity guidelines.
-
Remove password masking passwordmasking.com
Summarizes the results from an academic study investigating the impact removing password masking has on consumer trust.
-
JOSE is a Bad Standard That Everyone Should Avoid paragonie.com
The standards are either completely broken or complex minefields hard to navigate.
-
Why Authorization is Hard osohq.com
Because it needs multiple tradeoffs on Enforcement which is required in so many places, on Decision architecture to split business logic from authorization logic, and on Modeling to balance power and complexity.
-
Authorization Academy osohq.com
An in-depth, vendor-agnostic treatment of authorization that emphasizes mental models. This guide shows the reader how to think about their authorization needs in order to make good decisions about their authorization architecture and model.
-
Investigation into the Unusual Signups openstreetmap.lu
A really detailed analysis of suspicious contributor signups on OpenStreetMap. This beautiful and high-level report demonstrating an orchestrated and directed campaign might serve as a template for fraud reports.
-
What's the Difference Between OAuth, OpenID Connect, and SAML? okta.com
Identity is hard. Another take on the different protocol is always welcome to help makes sense of it all.
-
Separate the account, user and login/auth details news.ycombinator.com
Sound advice to lay down the foundation of a future-proof IAM API.
-
How to change the hashing scheme of already hashed user's passwords news.ycombinator.com
Good news: you're not stuck with a legacy password saving scheme. Here is a trick to transparently upgrade to stronger hashing algorithm.
-
Tidbits on AWS Cloud HSM hardware news.ycombinator.com
AWS CloudHSM Classic is backed by SafeNet's Luna HSM, current CloudHSM rely on Cavium's Nitrox, which allows for partitionable "virtual HSMs".
-
Google paper's author compares Macaroons and JWTs news.ycombinator.com
As a consumer/verifier of macaroons, they allow you (through third-party caveats) to defer some authorization decisions to someone else. JWTs don't.
-
You either die an MVP or live long enough to build content moderation mux.com
“You can think about the solution space for this problem by considering three dimensions: cost, accuracy and speed. And two approaches: human review and machine review. Humans are great in one of these dimensions: accuracy. The downside is that humans are expensive and slow…
-
As a user, I want… mobile.twitter.com
A meta-critic of account management, in which features expected by the business clash with real user needs, in the form of user stories written by a fictional project manager.
-
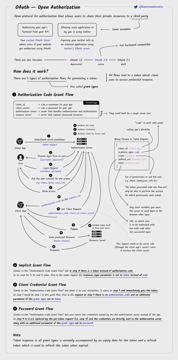
OAuth in one picture mobile.twitter.com
A nice summary card.
-
MISP taxonomies and classification misp-project.org
Tags to organize information on “threat intelligence including cyber security indicators, financial fraud or counter-terrorism information.”
-
A Comparative Long-Term Study of Fallback Authentication maximiliangolla.com
Key take-away: “schemes based on email and SMS are more usable. Mechanisms based on designated trustees and personal knowledge questions, on the other hand, fall short, both in terms of convenience and efficiency.”
-
Compromising online accounts by cracking voicemail systems martinvigo.com
Or why you should not rely on automated phone calls as a method to reach the user and reset passwords, 2FA or for any kind of verification. Not unlike SMS-based 2FA, it is currently insecure and can be compromised by the way of its weakest link: voicemail systems.
-
Identity Beyond Usernames lord.io
On the concept of usernames as identifiers, and the complexities introduced when unicode characters meets uniqueness requirements.
-
PKCE Explained loginradius.com
“PKCE is used to provide one more security layer to the authorization code flow in OAuth and OpenID Connect.”
-
What the Heck is Trust and Safety? linkedin.com
A couple of real use-case to demonstrate the role of a TnS team.
-
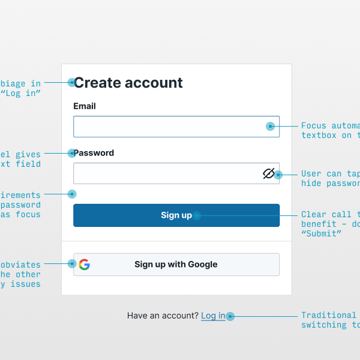
11 Tips for Better Signup / Login UX learnui.design
Some basic tips on the login form.
-
Hostnames and usernames to reserve ldpreload.com
List of all the names that should be restricted from registration in automated systems.
-
Cryptographic Right Answers latacora.micro.blog
An up to date set of recommendations for developers who are not cryptography engineers. There's even a shorter summary available.
-
Introduction to JSON Web Tokens jwt.io
Get up to speed on JWT with this article.
-
SAML is insecure by design joonas.fi
Not only weird, SAML is also insecure by design, as it relies on signatures based on XML canonicalization, not XML byte stream. Which means you can exploit XML parser/encoder differences.
-
Is SMS 2FA Secure? No. issms2fasecure.com
Definitive research project demonstrating successful attempts at SIM swapping.
-
Things end users care about but programmers don't instadeq.com
In the same spirit as above, but broader: all the little things we overlook as developers but users really care about. In the top of that list lies account-centric features, diverse integration and import/export tools. I.e. all the enterprise customers needs to cover.
-
AWS IAM Roles, a tale of unnecessary complexity infosec.rodeo
The history of fast-growing AWS explains how the current scheme came to be, and how it compares to GCP's resource hierarchy.
-
Enterprise Information Security infosec.mozilla.org
Mozilla's security and access guidelines.
-
Open-Sourcing BuzzFeed's SSO Experience increment.com
OAuth2-friendly adaptation of the Central Authentication Service (CAS) protocol. You'll find there good OAuth user flow diagrams.
-
Webauthn and security keys imperialviolet.org
Describe how authentication works with security keys, details the protocols, and how they articulates with WebAuthn. Key takeaway: “There is no way to create a U2F key with webauthn however. (…) So complete the transition to webauthn of your login process first, then transition…
-
The Laws of Identity identityblog.com
Is this paper aims at identity metasystem, its laws still provides great insights at smaller scale, especially the first law: to always allow user control and ask for consent to earn trust.
-
reCaptcha google.com
💸 Still an effective, economical and quick solution when your company can't afford to have a dedicated team to fight bots and spammers at internet scale.
-
Discover UI Design Decisions Of Leading Companies goodui.org
From Leaked Screenshots & A/B Tests.
-
Paper we love: Privacy github.com
A collection of scientific studies of schemes providing privacy by design.
-
Papers we love: Cryptography github.com
Foundational papers of cryptography.
-
Stack Overflow stackoverflow.com
Slim Framework questions over Stack Overflow.
-
User Guide slimframework.com
The official documentation for Slim Framework.
-
IntelliJ Slim plugins.jetbrains.com
Provides boilerplate codes for easier new project creation using skeleton.
-
Slim 4 - ReactPHP odan.github.io
Slim in combination with ReactPHP for the performance boost.
-
Slim 4 - GraphQL odan.github.io
Creating a modern HTTP APIs usig GraphQL.
-
Confusable Homoglyphs git.sr.ht
🆓 Homoglyphs is a common phishing trick.
-
General List of Reserved Words gist.github.com
This is a general list of words you may want to consider reserving, in a system where users can pick any name.
-
xkeyscorerules100.txt gist.github.com
NSA's XKeyscore matching rules for TOR and other anonymity preserving tools.
-
PKI for busy people gist.github.com
Quick overview of the important stuff.
-
common-domain-prefix-suffix-list.tsv gist.github.com
Top-5000 most common domain prefix/suffix list.
-
#1 gist.github.com
, #2, #3.
- next page of items loading…