The new NIST password guidance
A summary of NIST Special Publication 800-63B covering new password complexity guidelines.
- from
- IAM
- added
- 2026-10-10
- likes
- 0
similar
-
Dumb Password Rules github.com
🆓 Shaming sites with dumb password rules.
-
Practical Recommendations for Stronger, More Usable Passwords andrew.cmu.edu
This study recommend the association of: blocklist checks against commonly leaked passwords, password policies without character-class requirements, minimum-strength policies.
-
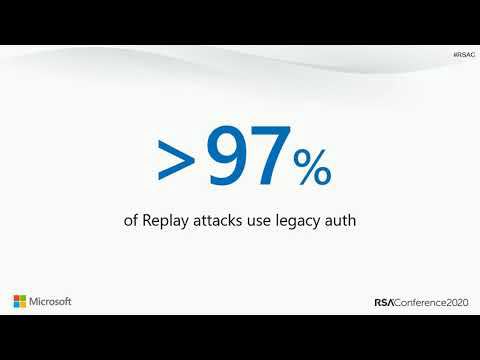
Breaking Password Dependencies: Challenges in the Final Mile at Microsoft youtube.com
The primary source of account hacks is password spraying (on legacy auth like SMTP, IMAP, POP, etc.), second is replay attack. Takeaway: password are insecure, use and enforce MFA.
-
Password expiration is dead techcrunch.com
Recent scientific research calls into question the value of many long-standing password-security practices such as password expiration policies, and points instead to better alternatives such as enforcing banned-password lists and MFA.
-
-
Beyond Passwords: 2FA, U2F and Google Advanced Protection troyhunt.com
An excellent walk-trough over all these technologies.
IAM › Password-based auth: “A summary of NIST Special Publication 800-63B covering new password complexity guidelines.”