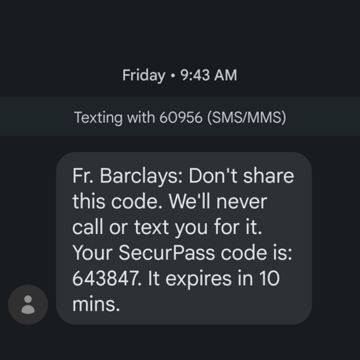
Is SMS 2FA Secure? No.
Definitive research project demonstrating successful attempts at SIM swapping.
- from
- IAM
- added
- 2026-10-10
- likes
- 0
similar
-
SMS: The most popular and least secure 2FA method allthingsauth.com
-
SMS 2FA auth is deprecated by NIST techcrunch.com
NIST has said that 2FA via SMS is bad and awful since 2016.
-
A Comparative Long-Term Study of Fallback Authentication maximiliangolla.com
Key take-away: “schemes based on email and SMS are more usable. Mechanisms based on designated trustees and personal knowledge questions, on the other hand, fall short, both in terms of convenience and efficiency.”
-
SMS Multifactor Authentication in Antarctica brr.fyi
Doesn't work because there are no cellphone towers at stations in Antarctica.
-
Simulating SMS Messages on Android appiumpro.com
-
Compromising online accounts by cracking voicemail systems martinvigo.com
Or why you should not rely on automated phone calls as a method to reach the user and reset passwords, 2FA or for any kind of verification. Not unlike SMS-based 2FA, it is currently insecure and can be compromised by the way of its weakest link: voicemail systems.
IAM › Multi-factor auth > SMS-based: “Definitive research project demonstrating successful attempts at SIM swapping.”