-
Efficient and automatic instrumentation for packed binaries link.springer.com
(June 2009)
-
BitBlaze: A new approach to computer security via binary analysis link.springer.com
(December 2008)
-
A study of the packer problem and its solutions link.springer.com
(September 2008)
-
Symbolic deobfuscation: From virtualized code back to the original link.springer.com
(July 2018)
-
Packer identification using hidden Markov model link.springer.com
(November 2017)
-
RAMBO: Run-Time packer analysis with multiple branch observation link.springer.com
(July 2016)
-
AppSpear: Bytecode decrypting and DEX reassembling for packed Android malware link.springer.com
(November 2015)
-
DexHunter: Toward extracting hidden code from packed Android applications link.springer.com
(September 2015)
-
Highlighting the impact of packed executable alterations with unsupervised learning link.springer.com
(April 2025) :star:
-
Assessing static and dynamic features for packing detection link.springer.com
(October 2024) :star:
-
Unpacking malware in the real world: A step-by step guide link.springer.com
(July 2024) :star:
-
Evading packing detection: Breaking heuristic-based static detectors link.springer.com
(July 2024) :star:
-
Experimental toolkit for manipulating executable packing link.springer.com
(June 2024) :star: :star:
-
Original entry point detection based on graph similarity link.springer.com
(April 2024) :star:
-
A machine-learning-based framework for supporting malware detection and analysis link.springer.com
(September 2021) :star:
-
VABox: A virtualization-based analysis framework of virtualization-obfuscated packed executables link.springer.com
(June 2021) :star:
-
Generic black-box end-to-end attack against state of the art API call based malware classifiers link.springer.com
(September 2018) :star:
-
On the (Im)possibility of obfuscating programs link.springer.com
(August 2001)
-
Boosting scalability in anomaly-based packed executable filtering link.springer.com
(November 2011)
-
Structural feature based anomaly detection for packed executable identification link.springer.com
(June 2011)
-
Eureka: A framework for enabling static malware analysis link.springer.com
(October 2008)
-
Challenging anti-virus through evolutionary malware obfuscation link.springer.com
(April 2016)
-
PEzoNG: Advanced packer for automated evasion on Windows link.springer.com
(December 2022) :star:
-
Anti-emulation trends in modern packers: A survey on the evolution of anti-emulation techniques in UPA packers link.springer.com
(May 2018)
-
Packer identification using byte plot and Markov plot link.springer.com
(September 2015)
-
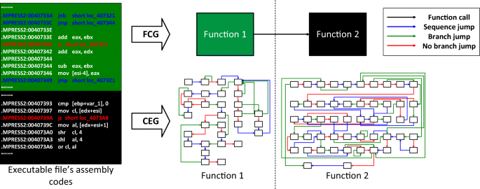
2-SPIFF: A 2-stage packer identification method based on function call graph and file attributes link.springer.com
(December 2021) :star:
-
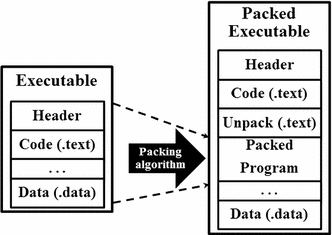
A survey on run-time packers and mitigation techniques link.springer.com
(November 2023) :star: :star:
-
Entropy analysis to classify unknown packing algorithms for malware detection link.springer.com
(May 2016) :star:
-
An efficient block-discriminant identification of packed malware link.springer.com
(August 2015)
-
Secure and advanced unpacking using computer emulation link.springer.com
(August 2007)
-
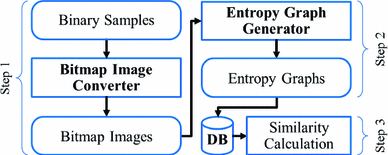
Malware analysis using visualized images and entropy graphs link.springer.com
(February 2015)
-
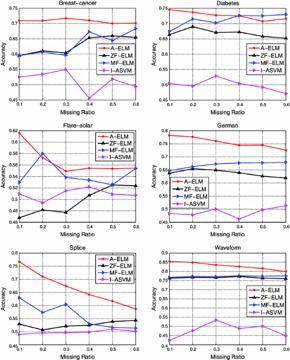
Absent extreme learning machine algorithm with application to packed executable identification link.springer.com
(January 2016)
-
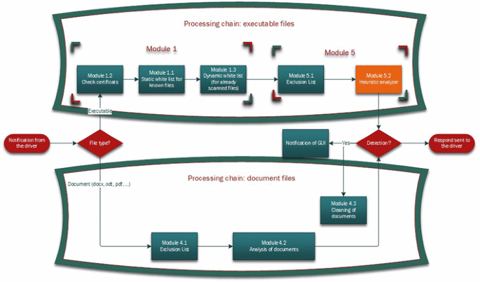
Construction and evaluation of the new heuristic malware detection mechanism based on executable files static analysis link.springer.com
(August 2018)
-
Structural analysis of binary executable headers for malware detection optimization link.springer.com
(May 2017)
-
Singular value decomposition and metamorphic detection link.springer.com
(November 2015)
-
Structural entropy and metamorphic malware link.springer.com
(November 2013)
-
Hunting for metamorphic engines link.springer.com
(November 2006)
-
An entropy-based distance measure for analyzing and detecting metamorphic malware link.springer.com
(June 2018)
-
Unknown malcode detection using OPCODE representation link.springer.com
(December 2008)
-
Deobfuscation of virtualization-obfuscated code through symbolic execution and compilation optimization link.springer.com
(April 2018)
-
Measuring and defeating anti-instrumentation-equipped malware link.springer.com
(June 2017)
-
Detection of metamorphic malware packers using multilayered LSTM networks link.springer.com
(November 2020) :star:
-
LIAPP liapp.lockincomp.com
Easiest and most powerful mobile app security solution.
-
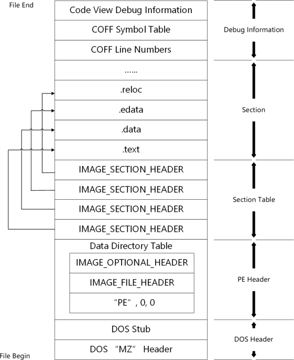
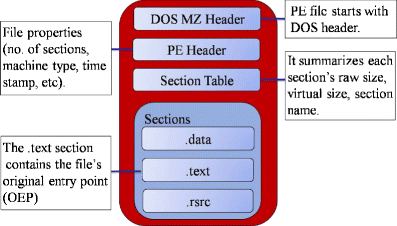
PE format - Win32 apps learn.microsoft.com
-
Laturi laturi.haxor.fi
Linker and compressor intended to be used for macOS 1k, 4k and perhaps 64K intros.
-
An original entry point detection method with candidate-sorting for more effective generic unpacking jstage.jst.go.jp
(January 2015)
-
An empirical evaluation of an unpacking method implemented with dynamic binary instrumentation jstage.jst.go.jp
(September 2011)
-
BareUnpack: Generic unpacking on the bare-metal operating system jstage.jst.go.jp
(December 2018)
-
An accurate packer identification method using support vector machine jstage.jst.go.jp
(January 2014)
-
- next page of items loading…