Structural analysis of binary executable headers for malware detection optimization
(May 2017)
- from
- Executable Packing
- added
- 2026-10-10
- likes
- 0
similar
-
Encoded executable file detection technique via executable file header analysis earticle.net
(April 2009)
-
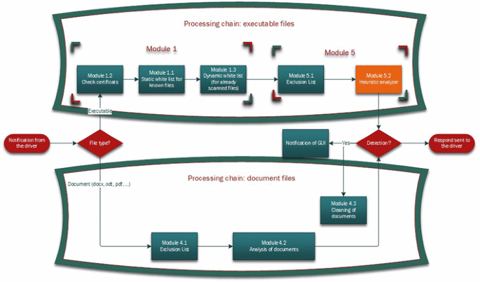
Construction and evaluation of the new heuristic malware detection mechanism based on executable files static analysis link.springer.com
(August 2018)
-
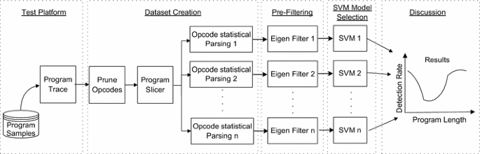
Detecting obfuscated malware using reduced opcode set and optimised runtime trace security-informatics.springeropen.com
(May 2016)
-
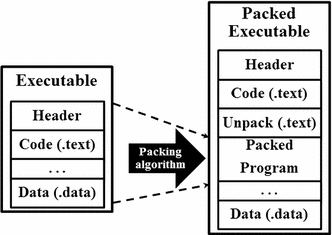
Entropy analysis to classify unknown packing algorithms for malware detection link.springer.com
(May 2016) :star:
-
-
Malware makeover: Breaking ML-based static analysis by modifying executable bytes arxiv.org
(May 2021) :star:
Executable Packing › :books: Literature > Scientific Research: “(May 2017)”