Indirect Prompt Injection Attacks: Hidden AI Risks
CrowdStrike's Dec 2025 analysis of IPI TTPs targeting enterprise GenAI, including attacker-controlled document poisoning, RAG context manipulation, and practical detection signals for SOC workflows.
- from
- Prompt Injection
- added
- 2026-10-10
- likes
- 0
similar
-
Prompt Injection 2.0: Hybrid AI Threats arxiv.org
Jul 2025 paper showing how prompt injections now combine with XSS, CSRF, AI worm propagation, and multi-agent infections to evade traditional WAFs entirely. Evaluates Preamble's classifier, data-tagging, and RL-based defenses against these hybrid scenarios.
-
MCP Prompt Injection: How AI Gets Hacked youtube.com
Nov 2025 hands-on walkthrough showing how prompt injection exploits tool metadata and trust boundaries in Model Context Protocol-integrated agents, which remain a primary attack surface as MCP adoption widens.
-
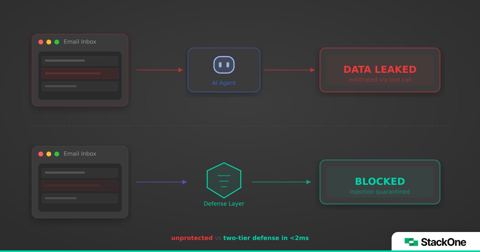
Indirect Prompt Injection Through MCP Tools: A Defense Guide stackone.com
Feb 2026 guide explaining why any MCP tool that reads data written outside your trust boundary (CRM notes, calendar invites, API responses) is an injection vector, with concrete mitigations per tool category.
-
CrowdStrike AI Unlocked crowdstrike.com
Released Feb 2026, designed to train security, developer, and AI teams on prompt injection against increasingly capable agents. Built by CrowdStrike's Counter Adversary Operations team.
-
How Microsoft Defends Against Indirect Prompt Injection Attacks microsoft.com
Microsoft MSRC's Jul 2025 post on FIDES, an information-flow control system enforcing privilege separation and prompt isolation to deterministically block IPI in Copilot-class agents.
-
The Landscape of Prompt Injection Threats in LLM Agents (SoK) arxiv.org
Feb 2026 systematization-of-knowledge paper with a unified taxonomy covering attack payload strategies (heuristic vs. optimisation-based) and defense intervention stages (text, model, execution). Introduces the AgentPI benchmark for context-dependent agent tasks that all prior…
Prompt Injection › Articles and Blog posts: “CrowdStrike's Dec 2025 analysis of IPI TTPs targeting enterprise GenAI, including attacker-controlled document poisoning, RAG context manipulation, and practical detection signals for SOC workflows.”