The Landscape of Prompt Injection Threats in LLM Agents (SoK)
Feb 2026 systematization-of-knowledge paper with a unified taxonomy covering attack payload strategies (heuristic vs. optimisation-based) and defense intervention stages (text, model, execution). Introduces the AgentPI benchmark for context-dependent agent tasks that all prior…
- from
- Prompt Injection
- added
- 2026-10-10
- likes
- 0
similar
-
Prompt Injection 2.0: Hybrid AI Threats arxiv.org
Jul 2025 paper showing how prompt injections now combine with XSS, CSRF, AI worm propagation, and multi-agent infections to evade traditional WAFs entirely. Evaluates Preamble's classifier, data-tagging, and RL-based defenses against these hybrid scenarios.
-
Securing AI Agents Against Prompt Injection Attacks arxiv.org
Nov 2025 benchmark of 847 adversarial test cases across 5 attack categories against 7 LLMs. The combined defense framework reduces attack success from 73.2% to 8.7% while retaining 94.3% of baseline task performance.
-
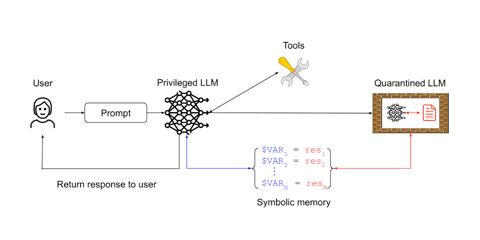
Design Patterns for Securing LLM Agents against Prompt Injections simonwillison.net
Overview of various strategies to mitigate the risk of prompt injection.
-
Prompt-Injection Cascades in a Multi-Agent Enterprise (ATLAS) doi.org
Forensic study in which one poisoned support ticket drives four agents across three model families to a fraudulent transfer in 17 of 18 trials, with no model jailbroken. Argues the failure is topological rather than per-model. Synthetic data, CC BY 4.0.
-
New Prompt Injection Papers: Agents Rule of Two and The Attacker Moves Second simonwillison.net
Simon Willison's Nov 2025 commentary on both landmark papers, including the finding that 12 published defenses were bypassed at >90% success rate using gradient descent and RL-based adaptive attacks.
-
Not what you've signed up for: Compromising Real-World LLM-Integrated Applications with Indirect Prompt Injection arxiv.org
This paper explores the concept of Indirect Prompt Injection attacks on Large Language Models (LLMs) through their integration with various applications. It identifies significant security risks, including remote data theft and ecosystem contamination, present in both…
Prompt Injection › Research Papers: “Feb 2026 systematization-of-knowledge paper with a unified taxonomy covering attack payload strategies (heuristic vs. optimisation-based) and defense intervention stages (text, model, execution). Introduces the AgentPI benchmark for context-dependent agent tasks that all prior…”