Detecting obfuscated malware using reduced opcode set and optimised runtime trace
(May 2016)
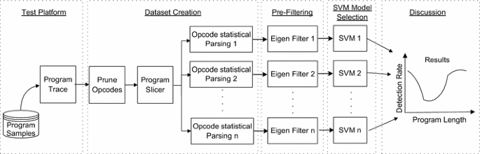
- from
- Executable Packing
- added
- 2026-10-10
- likes
- 0
similar
-
-
Structural analysis of binary executable headers for malware detection optimization link.springer.com
(May 2017)
-
Instructions-based detection of sophisticated obfuscation and packing ieeexplore.ieee.org
(October 2014)
-
-
Malware detection through opcode sequence analysis using machine learning api.semanticscholar.org
(June 2015)
-
Detecting unknown malicious code by applying classification techniques on opcode patterns doi.org
(February 2012)
Executable Packing › :books: Literature > Scientific Research: “(May 2016)”