Security
5,347 items in 29 lists
-
Elastic Yara Signatures github.com
Elastic's YARA signatures, which run on the Elastic endpoint agent.
-
Elastic Endpoint Behavioral Rules github.com
Elastic's endpoint behavioral (prevention) rules written in EQL, natively for the Elastic endpoint agent.
-
Elastic Endpoint Ransomware Artifact github.com
Elastic's ransomware artifact, which runs on the Elastic endpoint agent.
-
Elastic Detection Rules github.com
Elastic's detection rules written natively for the Elastic SIEM. Can easily be converted for use by other SIEMs using Uncoder.
-
Elastic's Detection Engineering Behavior Maturity Model elastic.co
Elastic's qualitative and quantitative approach to measuring threat detection program maturity.
-
Elastic Common Schema elastic.co
Elastic's proprietary model used as a framework for normalizing security data.
-
Splunk Common Information Model (CIM) docs.splunk.com
Splunk's proprietary model used as a framework for normalizing security data.
-
GCP Security Command Center Findings docs.cloud.google.com
A list of all GCP Security Command Center Findings, their descriptions, and associated data sources.
-
AWS GuardDuty Findings docs.aws.amazon.com
A list of all AWS GuardDuty Findings, their descriptions, and associated data sources.
-
Detections Digest | Sergey Polzunov detections-digest.rulecheck.io
A newsletter that features updates from many popular detection content sources listed here.
-
Detection Engineering Field Manual | Zack Allen detectionengineering.net
a series of posts exploring the various foundational components of Detection Engineering.
-
Detection Engineering Weekly | Zack Allen detectionengineering.net
A newsletter dedicated to news and how-tos for Detection Engineering.
-
Detection Engineering Maturity Matrix | Kyle Bailey detectionengineering.io
A detailed matrix that serves as a tool to measure the overall maturity of an organization's Detection Engineering program.
-
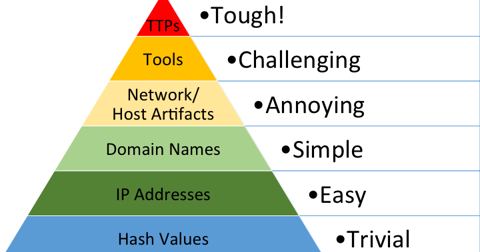
The Pyramid of Pain | David J Bianco detect-respond.blogspot.com
A model used to describe various categorizations of indicator's of compromise and their level of effectiveness in detecting threat actors.
-
How Google Does It: Making threat detection high-quality, scalable, and modern | Anton Chuvakin, Tim Nguyen cloud.google.com
The team at Google highlights 5 key principles for building a high quality, scalable and modern threat detection program.
-
CAR Coverage Comparison car.mitre.org
A matrix of MITRE ATT&CK technique IDs and links to available Splunk Security Content, Elastic detection rules, Sigma rules, and CAR content.
-
MITRE Cyber Analytics Repository (CAR) car.mitre.org
MITRE's well-maintained repository of detection content.
-
The Zen of Security Rules | Justin Ibarra br0k3nlab.com
Outlines 19 aphorisms that serve as universal principles for the creation of high quality detection content.
-
MaGMa (Management, Growth and Metrics & Assessment) Use Case Definition Model betaalvereniging.nl
A business-centric approach for defining threat detection use cases.
-
AttackRuleMap attackrulemap.com
Mapping of open-source detection rules and atomic tests.
-
MITRE ATT&CK Data Sources List attack.mitre.org
Data source objects added to MITRE ATT&CK as part of v10.
-
MITRE ATT&CK attack.mitre.org
The foundational framework of adversary tactics, techniques, and procedures based on real-world observations.
-
CTI Analyst Field Manual | Andrey Pautov 1200km.com
Practical CTI-to-detection reference covering evidence labels, source reliability, ATT&CK mapping gates, hunting hypotheses, and detection backlog workflow.
-
Suricata-Check suricata-check.teuwen.net
A command-line utility to provide feedback on Suricata rules. It can detect issues such as covering syntax validity, interpretability, rule specificity, rule coverage, and efficiency.
-
Stamus Lateral Movement Detection Rules stamus-networks.com
Suricata ruleset to detect lateral movement.
-
sidallocation.org sidallocation.org
Sid Allocation working group, list of SID ranges.
-
EveBox Rules rules.evebox.org
Suricata Rule Browser, indexes many free rulesets, including rules from the Suricata Ruleset Index.
-
PAW Patrules pawpatrules.fr
Another free (CC BY-NC-SA) collection of rules for the Suricata engine.
-
NF IDS rules networkforensic.dk
-
NF Scanners IDS Rules networkforensic.dk
-
NF SCADA IDS Rules networkforensic.dk
-
InfluxDB Suricata Input Plugin github.com
Input Plugin for Telegraf to collect and forward Suricata stats logs (included out of the box in recent Telegraf releases).
-
Quantum Insert detection for Suricata github.com
Suricata rules accompanying Fox-IT's QUANTUM 2015 blog/BroCon talk.
-
CDMCS github.com
Cyber Defence Monitoring Course: Rule-based Threat Detection.
-
3CORESec NIDS - Sinkholes dtection.io
Suricata ruleset focused on a curated list of public malware sinkholes (free).
-
3CORESec NIDS - Lateral Movement dtection.io
Suricata ruleset focusing on lateral movement techniques (paid).
-
Lawmaker 3coresec.com
Suricata IDS rule and fleet management system.
-
Elevation of Privilege (EOP) by Microsoft web.archive.org
A card game based on Microsoft's threat modeling framework "STRIDE" (Spoofing, Tampering etc.). The card deck is available as PDF from Microsoft. Adam Shostack, the author of EoP has also a git repo for EoP.
-
Security Cards securitycards.cs.washington.edu
A card game encouraging to think broadly and creatively about computer security threats. Four dimensions are covered: Human Impact, Adversary's Motivations, Adversary's Resources, Adversary's Methods.
-
Tabletop Simulations to Improve Your Information Security Program redcanary.com
Red Canary's write-up about tabletop exercises for information security programs.
-
Game On: Tabletop Games to Teach Cyber and Information Security Concepts linkedin.com
List of tabletop games to teach cyber and information security concepts.
-
Crypto Go cryptogogame.com
An educational card game designed to teach up to date symmetric cryptography. Crypto Go deck consists of cards representing modern cryptographic tools.
-
Cornucopia cornucopia.owasp.org
OWASP® Cornucopia is a threat modeling tool in the form of a card game to assist software development teams identify security requirements in Agile, conventional and formal development processes. It's based on OWASP's Top 10, ASVS/MASVS/MASTG, CAPEC and SAFECode. The card…
-
Backdoors & Breaches blackhillsinfosec.com
An incident response card game. It helps you conduct incident response tabletop exercises and learn attack tactics, tools, and methods.
-
Tabletop Security Games & Cards adam.shostack.org
List of security card games created and maintained by Adam Shostack.
-
Know your risks aca.edu.au
Learn what information is safe to share online and understand the risks. Learn about whether to share, not share or be cautious with different pieces of information.
-
WeakPass weakpass.com
Collection of large wordlists.
-
-
-
- next page of items loading…