Security
5,347 items in 29 lists
-
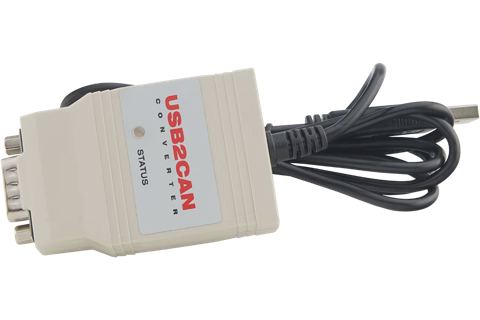
USB2CAN 8devices.com
Cheap USB to CAN connector that will register a device on linux that you can use to get data from a CAN network.
-
-
Counteractive Playbooks github.com
Counteractive PLaybooks collection.
-
AWS Incident Response Runbook Samples github.com
AWS IR Runbook Samples meant to be customized per each entity using them. The three samples are: "DoS or DDoS attack", "credential leakage", and "unintended access to an Amazon S3 bucket".
-
The Appliance for Digital Investigation and Analysis (ADIA) forensics.cert.org
VMware-based appliance used for digital investigation and acquisition and is built entirely from public domain software. Among the tools contained in ADIA are Autopsy, the Sleuth Kit, the Digital Forensics Framework, log2timeline, Xplico, and Wireshark. Most of the system…
-
GetData Forensic Imager forensicimager.com
Windows based program that will acquire, convert, or verify a forensic image in one of the following common forensic file formats.
-
Memoryze fireeye.com
Free memory forensic software that helps incident responders find evil in live memory. Memoryze can acquire and/or analyze memory images, and on live systems, can include the paging file in its analysis.
-
IOC Finder fireeye.com
Free tool from Mandiant for collecting host system data and reporting the presence of Indicators of Compromise (IOCs). Support for Windows only. No longer maintained. Only fully supported up to Windows 7 / Windows Server 2008 R2.
-
Highlighter fireeye.com
Free Tool available from Fire/Mandiant that will depict log/text file that can highlight areas on the graphic, that corresponded to a key word or phrase. Good for time lining an infection and what was done post compromise.
-
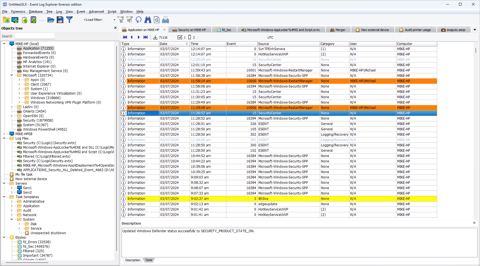
Event Log Explorer eventlogxp.com
Tool developed to quickly analyze log files and other data.
-
Eric Zimmerman Tools ericzimmerman.github.io
An updated list of forensic tools created by Eric Zimmerman, an instructor for SANS institute.
-
Microsoft ProcDump docs.microsoft.com
Dumps any running Win32 processes memory image on the fly.
-
Digital Forensics Discord Server discordapp.com
Community of 8,000+ working professionals from Law Enforcement, Private Sector, and Forensic Vendors. Additionally, plenty of students and hobbyists! Guide here.
-
How we abused Slack's TURN servers to gain access to internal services enablesecurity.com
-
SANS Investigative Forensic Toolkit (SIFT) Workstation digital-forensics.sans.org
Demonstrates that advanced incident response capabilities and deep dive digital forensic techniques to intrusions can be accomplished using cutting-edge open-source tools that are freely available and frequently updated.
-
HackDig en.hackdig.com
-
The Bug Hunters Methodology v2.1 docs.google.com
-
Slack DFIR channel dfircommunity.slack.com
Slack DFIR Communitiy channel - Signup here.
-
SSRF bible. Cheatsheet docs.google.com
-
How do we Stop Spilling the Beans Across Origins? docs.google.com
-
CVE-2017-2446 or JSC::JSGlobalObject::isHavingABadTime. doar-e.github.io
-
DFIR ORC dfir-orc.github.io
DFIR ORC is a collection of specialized tools dedicated to reliably parse and collect critical artifacts such as the MFT, registry hives or event logs. DFIR ORC collects data, but does not analyze it: it is not meant to triage machines. It provides a forensically relevant…
-
-
Scrutiny datarift.blogspot.tw
-
Dark Reading darkreading.com
-
XSS via a spoofed React element danlec.com
-
Cyber Triage cybertriage.com
Cyber Triage collects and analyzes host data to determine if it is compromised. It's scoring system and recommendation engine allow you to quickly focus on the important artifacts. It can import data from its collection tool, disk images, and other collectors (such as KAPE). It…
-
csp evaluator csper.io
-
Csper csper.io
-
Laravel CSP Generator csp-generator.shakiltech.com
-
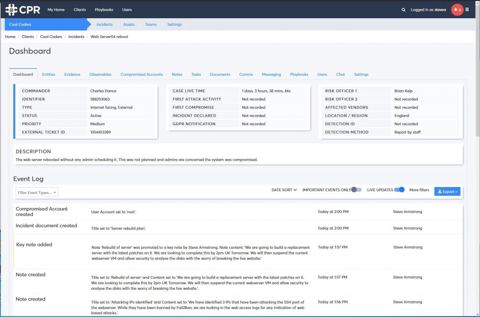
CyberCPR cybercpr.com
Community and commercial incident management tool with Need-to-Know built in to support GDPR compliance while handling sensitive incidents.
-
What is a Side-Channel Attack ? csoonline.com
-
Certificate Search crt.sh
-
ARTist artist.cispa.saarland
a flexible open-source instrumentation and hybrid analysis framework for Android apps and Android's Java middleware. It is based on the Android Runtime's (ART) compiler and modifies code during on-device compilation.
-
CrowdSec crowdsec.net
-
Crowd Response crowdstrike.com
Lightweight Windows console application designed to aid in the gathering of system information for incident response and security engagements. It features numerous modules and output formats.
-
AppSweep by Guardsquare appsweep.guardsquare.com
Free, fast Android application security testing for developers
-
Poor RichFaces codewhitesec.blogspot.com
-
AppUse appsec-labs.com
custom build for penetration testing
-
Censys censys.io
-
Computer Aided Investigative Environment (CAINE) caine-live.net
Contains numerous tools that help investigators during their analysis, including forensic evidence collection.
-
How we exploited a remote code execution vulnerability in math.js capacitorset.github.io
-
Live Response Collection brimorlabs.com
Automated tool that collects volatile data from Windows, OSX, and *nix based operating systems.
-
-
IBM Security AppScan Mobile Analyzer appscan.bluemix.net
not free
-
BRETT BUERHAUS buer.haus
-
grayhatwarfare buckets.grayhatwarfare.com
-
Broken Browser brokenbrowser.com
-
IREC binalyze.com
All-in-one IR Evidence Collector which captures RAM Image, $MFT, EventLogs, WMI Scripts, Registry Hives, System Restore Points and much more. It is FREE, lightning fast and easy to use.
-
approver approver.talos-sec.com
Approver is a fully automated security analysis and risk assessment platform for Android and iOS apps. Not free.
- next page of items loading…