Security
5,347 items in 29 lists
-
docker-metasploit hub.docker.com
-
official Kali Linux hub.docker.com
-
OWASP WrongSecrets hub.docker.com
-
Cyware Threat Response Docker hub.docker.com
-
OWASP Juice Shop hub.docker.com
-
Holistic Info-Sec for Web Developers holisticinfosecforwebdevelopers.com
Free and downloadable book series with very broad and deep coverage of what Web Developers and DevOps Engineers need to know in order to create robust, reliable, maintainable and secure software, networks and other, that are delivered continuously, on time, with no nasty…
-
Hardening Windows 10 hardenwindows10forsecurity.com
Guide for hardening Windows 10
-
Glastopf glastopf.org
Glastopf is a Honeypot which emulates thousands of vulnerabilities to gather data from attacks targeting web applications. The principle behind it is very simple: Reply the correct response to the attacker exploiting the web application.
-
Spam Scanner github.com
Anti-Spam Scanning Service and Anti-Spam API by @niftylettuce.
-
Stealth fbb-git.gitlab.io
File integrity checker that leaves virtually no sediment. Controller runs from another machine, which makes it hard for an attacker to know that the file system is being checked at defined pseudo random intervals over SSH. Highly recommended for small to medium deployments.
-
Fail2Ban fail2ban.org
Scans log files and takes action on IPs that show malicious behavior.
-
PACKET_MMAP/TPACKET/AF_PACKET elixir.bootlin.com
It's fine to use PACKET_MMAP to improve the performance of the capture and transmission process in Linux.
-
httpry dumpsterventures.com
httpry is a specialized packet sniffer designed for displaying and logging HTTP traffic. It is not intended to perform analysis itself, but to capture, parse, and log the traffic for later analysis. It can be run in real-time displaying the traffic as it is parsed, or as a…
-
T-Pot Honeypot Distro dtag-dev-sec.github.io
T-Pot is based on the network installer of Ubuntu Server 16/17.x LTS. The honeypot daemons as well as other support components being used have been containerized using docker. This allows us to run multiple honeypot daemons on the same network interface while maintaining a…
-
Internet Storm Center dshield.org
The ISC was created in 2001 following the successful detection, analysis, and widespread warning of the Li0n worm. Today, the ISC provides a free analysis and warning service to thousands of Internet users and organizations, and is actively working with Internet Service…
-
DrKeithJones.com drkeithjones.com
A blog on cyber security and network security monitoring.
-
Emerging Threats - Open Source doc.emergingthreats.net
Emerging Threats began 10 years ago as an open source community for collecting Suricata and SNORT® rules, firewall rules, and other IDS rulesets. The open source community still plays an active role in Internet security, with more than 200,000 active users downloading the…
-
Denyhosts denyhosts.sourceforge.net
Thwart SSH dictionary based attacks and brute force attacks.
-
Cyware Threat Intelligence Feeds cyware.com
Cyware’s Threat Intelligence feeds brings to you the valuable threat data from a wide range of open and trusted sources to deliver a consolidated stream of valuable and actionable threat intelligence. Our threat intel feeds are fully compatible with STIX 1.x and 2.0, giving you…
-
Best Linux Penetration Testing Distributions @ CyberPunk cyberpunk.rs
Description of main penetration testing distributions
-
Conpot conpot.org
ICS/SCADA Honeypot. Conpot is a low interactive server side Industrial Control Systems honeypot designed to be easy to deploy, modify and extend. By providing a range of common industrial control protocols we created the basics to build your own system, capable to emulate…
-
How to Hack Like a Pornstar books2read.com
A step by step process for breaking into a BANK, Sparc Flow, 2017
-
How to Investigate Like a Rockstar books2read.com
Live a real crisis to master the secrets of forensic analysis, Sparc Flow, 2017
-
Security Onion blog.securityonion.net
Security Onion is a Linux distro for intrusion detection, network security monitoring, and log management. It's based on Ubuntu and contains Snort, Suricata, Zeek, OSSEC, Sguil, Squert, Snorby, ELSA, Xplico, NetworkMiner, and many other security tools. The easy-to-use Setup…
-
AlienVault Open Threat Exchange alienvault.com
AlienVault Open Threat Exchange (OTX), to help you secure your networks from data loss, service disruption and system compromise caused by malicious IP addresses.
-
Live HTTP headers addons.mozilla.org
Live HTTP headers is a free firefox addon to see your browser requests in real time. It shows the entire headers of the requests and can be used to find the security loopholes in implementations.
-
abuse.ch abuse.ch
ZeuS Tracker / SpyEye Tracker / Palevo Tracker / Feodo Tracker tracks Command&Control servers (hosts) around the world and provides you a domain- and an IP-blocklist.
-
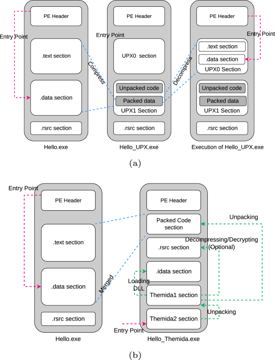
Packing induced bias in deep learning malware classifiers: A systematic experimental study ieeexplore.ieee.org
(February 2026)
-
A packer identification method based on section-entropy plot link.springer.com
(February 2026) :star:
-
Security Monitoring Labs | cybersecurity101.net cybersecurity101.net
48 free, step-by-step labs that build a small Wazuh monitoring stack on your own VMs, connect Linux and Windows (Sysmon) log sources, then write and tune detection rules, test them with simulated events, triage alerts and report on coverage. No account or hosted platform.
-
Clankerusecase clankerusecase.com
Threat-led library of 7,800+ MITRE ATT&CK-mapped detections in Defender/Sentinel KQL, Sigma, Splunk SPL, Datadog, Falcon LogScale, and AWS CloudWatch, generated from public threat-intel reporting and schema-validated before publish.
-
disclosedby disclosedby.com
-
RansomLeak GDPR Training ransomleak.com