Security
287 items from sbilly/awesome-security ★14,971
-
Docker Bench for Security hub.docker.com
-
OWASP WebGoat Project docker image hub.docker.com
-
OWASP Mutillidae II Web Pen-Test Practice Application hub.docker.com
-
Damn Vulnerable Web Application (DVWA) hub.docker.com
-
Gophish getgophish.com
An Open-Source Phishing Framework.
-
DPDK dpdk.org
DPDK is a set of libraries and drivers for fast packet processing.
-
Security @ Distrowatch distrowatch.com
Website dedicated to talking about, reviewing and keeping up to date with open source operating systems
-
Cuckoo Sandbox cuckoosandbox.org
Cuckoo Sandbox is an Open Source software for automating analysis of suspicious files. To do so it makes use of custom components that monitor the behavior of the malicious processes while running in an isolated environment.
-
ClamAv clamav.net
ClamAV® is an open-source antivirus engine for detecting trojans, viruses, malware & other malicious threats.
-
fwknop cipherdyne.org
Protects ports via Single Packet Authorization in your firewall.
-
HoneyDrive bruteforce.gr
HoneyDrive is the premier honeypot Linux distro. It is a virtual appliance (OVA) with Xubuntu Desktop 12.04.4 LTS edition installed. It contains over 10 pre-installed and pre-configured honeypot software packages such as Kippo SSH honeypot, Dionaea and Amun malware honeypots…
-
AIEngine bitbucket.org
AIEngine is a next generation interactive/programmable Python/Ruby/Java/Lua packet inspection engine with capabilities of learning without any human intervention, NIDS(Network Intrusion Detection System) functionality, DNS domain classification, network collector, network…
-
AutoShun autoshun.org
AutoShun is a Snort plugin that allows you to send your Snort IDS logs to a centralized server that will correlate attacks from your sensor logs with other snort sensors, honeypots, and mail filters from around the world.
-
OSSIM alienvault.com
OSSIM provides all of the features that a security professional needs from a SIEM offering – event collection, normalization, and correlation.
-
Real World Cryptography manning.com
This early-access book teaches you applied cryptographic techniques to understand and apply security at every level of your systems and applications.
-
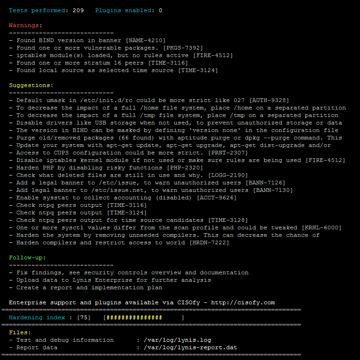
Lynis is an open source security auditing tool including Docker auditing cisofy.com
an open source security auditing tool for Linux/Unix.
-
Docker Security - Quick Reference binarymist.io
A book on understanding the Docker security defaults, how to improve them (theory and practical), along with many tools and techniques.
-
shai-hulud-scanner github.com
Detect indicators of compromise from the Shai Hulud 2.0 npm supply chain attack that compromised 796+ packages. Performs comprehensive security checks for malicious files, hashes, and patterns.
-
cve-ape github.com
A non-intrusive CVE scanner for embedding in test and CI environments that can scan package lists and individual packages for existing CVEs via locally stored CVE database. Can also be used as an offline CVE scanner for e.g. OT/ICS.
-
react2shell-scanner github.com
Detect CVE-2025-55182 (React2Shell) RCE vulnerability in React Server Components. Scans React 19.x and Next.js projects for critical remote code execution flaws.
-
Sigma2SPL github.com
A repository of all SIGMA rules converted to SPL that runs on a weekly schedule to update the repository and align with the up to date version of the SIGMA rules repository.
-
Xplico xplico.org
The goal of Xplico is extract from an internet traffic capture the applications data contained. For example, from a pcap file Xplico extracts each email (POP, IMAP, and SMTP protocols), all HTTP contents, each VoIP call (SIP), FTP, TFTP, and so on. Xplico isn’t a network…
-
Workbench workbench.readthedocs.org
A scalable python framework for security research and development teams.
-
SecMobi Wiki wiki.secmobi.com
A collection of mobile security resources which including articles, blogs, books, groups, projects, tools and conferences. *
-
w3af w3af.org
w3af is a Web Application Attack and Audit Framework. The project’s goal is to create a framework to help you secure your web applications by finding and exploiting all web application vulnerabilities.
-
Threat Jammer threatjammer.com
REST API service that allows developers, security engineers, and other IT professionals to access curated threat intelligence data from a variety of sources.
-
SSHGuard sshguard.net
A software to protect services in addition to SSH, written in C
-
Sqreen sqreen.io
Sqreen is a Runtime Application Self-Protection (RASP) solution for software teams. An in-app agent instruments and monitors the app. Suspicious user activities are reported and attacks are blocked at runtime without code modification or traffic redirection.
-
sqlmap sqlmap.org
sqlmap is an open source penetration testing tool that automates the process of detecting and exploiting SQL injection flaws and taking over of database servers. It comes with a powerful detection engine, many niche features for the ultimate penetration tester and a broad range…
-
SBL / XBL / PBL / DBL / DROP / ROKSO spamhaus.org
The Spamhaus Project is an international nonprofit organization whose mission is to track the Internet's spam operations and sources, to provide dependable realtime anti-spam protection for Internet networks, to work with Law Enforcement Agencies to identify and pursue spam and…
-
SpamAssassin spamassassin.apache.org
A powerful and popular email spam filter employing a variety of detection technique.
-
Bifrozt sourceforge.net
Bifrozt is a NAT device with a DHCP server that is usually deployed with one NIC connected directly to the Internet and one NIC connected to the internal network. What differentiates Bifrozt from other standard NAT devices is its ability to work as a transparent SSHv2 proxy…
-
The Security Engineer Handbook securityhandbook.io
A short read that discusses the dos and dont's of working in a security team, and the many tricks and tips that can help you in your day-to-day as a security engineer.
-
Scammer-List scammerlist.now.sh
A free open source AI based Scam and Spam Finder with a free API
-
sagan sagan.quadrantsec.com
Sagan uses a 'Snort like' engine and rules to analyze logs (syslog/event log/snmptrap/netflow/etc).
-
Rudder rudder-project.org
Rudder is an easy to use, web-driven, role-based solution for IT Infrastructure Automation & Compliance. Automate common system administration tasks (installation, configuration); Enforce configuration over time (configuring once is good, ensuring that configuration is valid…
-
Linux Malware Detect rfxn.com
A malware scanner for Linux designed around the threats faced in shared hosted environments.
-
Usable Security Course pt.coursera.org
Usable Security course at coursera. Quite good for those looking for how security and usability intersects.
-
Project Honey Pot projecthoneypot.org
Project Honey Pot is the first and only distributed system for identifying spammers and the spambots they use to scrape addresses from your website. Using the Project Honey Pot system you can install addresses that are custom-tagged to the time and IP address of a visitor to…
-
Portswigger portswigger.net
PortSwigger offers tools for web application security, testing & scanning. Choose from a wide range of security tools & identify the very latest vulnerabilities.
-
PhishTank phishtank.com
PhishTank is a collaborative clearing house for data and information about phishing on the Internet. Also, PhishTank provides an open API for developers and researchers to integrate anti-phishing data into their applications at no charge.
-
OWASP Testing Checklist v4 owasp.org
List of some controls to test during a web vulnerability assessment. Markdown version may be found here.
-
OSSEC ossec.github.io
Comprehensive Open Source HIDS. Not for the faint of heart. Takes a bit to get your head around how it works. Performs log analysis, file integrity checking, policy monitoring, rootkit detection, real-time alerting and active response. It runs on most operating systems…
-
OpenVAS NVT Feed openvas.org
The public feed of Network Vulnerability Tests (NVTs). It contains more than 35,000 NVTs (as of April 2014), growing on a daily basis. This feed is configured as the default for OpenVAS.
-
OpenVAS openvas.org
OpenVAS is a framework of several services and tools offering a comprehensive and powerful vulnerability scanning and vulnerability management solution.
-
OpenFPC openfpc.org
OpenFPC is a set of tools that combine to provide a lightweight full-packet network traffic recorder & buffering system. It's design goal is to allow non-expert users to deploy a distributed network traffic recorder on COTS hardware while integrating into existing alert and log…
-
PF_RING ZC (Zero Copy) ntop.org
PF_RING ZC (Zero Copy) is a flexible packet processing framework that allows you to achieve 1/10 Gbit line rate packet processing (both RX and TX) at any packet size. It implements zero copy operations including patterns for inter-process and inter-VM (KVM) communications.
-
Node.js Secure Coding: Prevention and Exploitation of Path Traversal Vulnerabilities nodejs-security.com
Master secure coding in Node.js with real-world vulnerable dependencies and experience firsthand secure coding techniques against Path Traversal vulnerabilities.
-
Node.js Secure Coding: Defending Against Command Injection Vulnerabilities nodejs-security.com
Learn secure coding conventions in Node.js by executing command injection attacks on real-world npm packages and analyzing vulnerable code.
-
ngrep ngrep.sourceforge.net
ngrep strives to provide most of GNU grep's common features, applying them to the network layer. ngrep is a pcap-aware tool that will allow you to specify extended regular or hexadecimal expressions to match against data payloads of packets. It currently recognizes IPv4/6, TCP…
- next page of items loading…