Xplico
The goal of Xplico is extract from an internet traffic capture the applications data contained. For example, from a pcap file Xplico extracts each email (POP, IMAP, and SMTP protocols), all HTTP contents, each VoIP call (SIP), FTP, TFTP, and so on. Xplico isn’t a network…
- from
- Security
- added
- 2026-10-10
- likes
- 0
similar
-
Xplico xplico.org
The goal of Xplico is extract from an internet traffic capture the applications data contained. For example, from a pcap file Xplico extracts each email (POP, IMAP, and SMTP protocols), all HTTP contents, each VoIP call (SIP), FTP, TFTP, and so on. Xplico isn't a network…
-
Tracexy rockxy.io
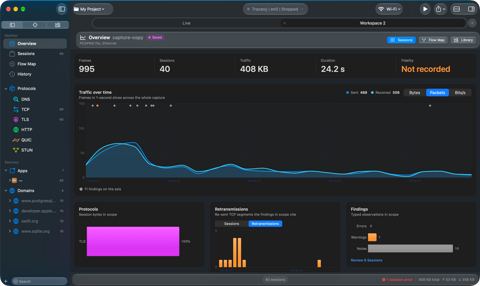
Open-source, session-based network intelligence for capturing live traffic and investigating PCAP/PCAPNG files locally.
-
pcapfex github.com
Packet CAPture Forensic Evidence eXtractor (pcapfex) is a tool that finds and extracts files from packet capture files. Its power lies in its ease of use. Just provide it a pcap file, and it will try to extract all of the files. It is an extensible platform, so additional file…
-
XPA web.archive.org
DOS executable packer.
-
tcpxtract tcpxtract.sourceforge.net
is a tool for extracting files from network traffic based on file signatures. Extracting files based on file type headers and footers (sometimes called "carving") is an age old data recovery technique.
-
Xplot xplot.org
The program xplot was written in the late 1980s to support the analysis of TCP packet traces.
Security › Network > Full Packet Capture / Forensic: “The goal of Xplico is extract from an internet traffic capture the applications data contained. For example, from a pcap file Xplico extracts each email (POP, IMAP, and SMTP protocols), all HTTP contents, each VoIP call (SIP), FTP, TFTP, and so on. Xplico isn’t a network…”