Networking
473 items in 5 lists
-
Zeek zeek.org
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
-
tcpdump tcpdump.org
Packet analyzer for network traffic capture.
-
Suricata suricata-ids.org
Suricata is a high performance Network IDS, IPS and Network Security Monitoring engine. Open Source and owned by a community run non-profit foundation, the Open Information Security Foundation (OISF). Suricata is developed by the OISF and its supporting vendors.
-
Snort snort.org
Snort is a free and open source network intrusion prevention system (NIPS) and network intrusion detection system (NIDS)created by Martin Roesch in 1998. Snort is now developed by Sourcefire, of which Roesch is the founder and CTO. In 2009, Snort entered InfoWorld's Open Source…
-
FOSDEM fosdem.org
Annual open source event in Brussels.
-
Cilium cilium.io
project (GitHub repository) is a technology relying on eBPF and XDP to provide "fast in-kernel networking and security policy enforcement for containers based on eBPF programs generated on the fly". Many presentations available (with overlap):
-
Wazo wazo-platform.org
VoIP API platform built on top of Asterisk, Kamailio and RTPEngine.
-
SIP3 sip3.io
VoIP & RTC traffic monitoring and analysis platform.
-
Routr routr.io
Lightweight SIP proxy, location server, and registrar written in Node.js.
-
OpenSIPS opensips.org
Open source SIP server, tracing its roots in OpenSER (presently Kamailio).
-
Janus janus.conf.meetecho.com
Lightweight open source, general purpose, WebRTC gateway.
-
FusionPBX fusionpbx.com
Multitenant system built on top of FreeSWITCH.
-
FreeSWITCH freeswitch.org
Open source multi-protocol, cross-platform and software switch.
-
FreePBX freepbx.org
Web Manager for Asterisk.
-
Asterisk asterisk.org
PBX framework supporting multiple protocols and platforms.
-
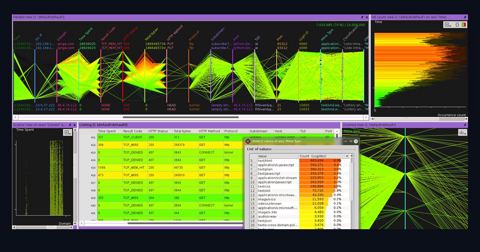
Squey squey.org
Interactive visualization software designed to explore large PCAPs to detect anomalies / weak signals.
-
tcpxtract tcpxtract.sourceforge.net
is a tool for extracting files from network traffic based on file signatures. Extracting files based on file type headers and footers (sometimes called "carving") is an age old data recovery technique.
-
tcpick tcpick.sourceforge.net
is a textmode sniffer libpcap-based that can track, reassemble and reorder tcp streams. Tcpick is able to save the captured flows in different files or displays them in the terminal, and so it is useful to sniff files that are transmitted via ftp or http. It can display all the…
-
usbmon kernel.org
USB capture for Linux.
-
ntopng ntop.org
Ntopng is a network traffic probe that shows the network usage, similar to what the popular top Unix command does.
-
PF_RING ntop.org
PF_RING is a new type of network socket that dramatically improves the packet capture speed.
-
DPDK dpdk.org
DPDK is a set of libraries and drivers for fast packet processing.
-
AIEngine bitbucket.org
AIEngine is a next generation interactive/programmable Python/Ruby/Java/Lua packet inspection engine with capabilities of learning without any human intervention, NIDS(Network Intrusion Detection System) functionality, DNS domain classification, network collector, network…
-
PJSIP pjsip.org
Multi-protocol RTC library written in C.
-
Kamailio kamailio.org
Open source SIP server widely deployed by carriers and providers. Formerly known as OpenSER.
-
WebRTC webrtc.org
Supports video, voice, and generic data to be sent between peers.
-
User Group groups.google.com
Discuss all user issues related to using Vert.x.
-
SNMP++ agentpp.com
a C++ API which supports SNMP v1/2c/v3. [custom permissive license]
-
AGENT++ agentpp.com
C++ framework provides a complete tri-lingual SNMP v1/2c/3 protocol engine and dispatcher for the development of SNMP agents. [Apache-2.0]
-
A generic introduction to Cilium opensource.googleblog.com
Generic introduction to Cilium.
- next page of items loading…