Incident Response
218 items from meirwah/awesome-incident-response ★9,444
-
NullSec Linux github.com
Security-focused Linux distribution with 140+ pre-installed forensic and offensive security tools, custom hardened kernel, and integrated incident response workflows.
-
NullSec LogReaper github.com
High-speed log analysis and forensics tool with multi-format parsing, pattern matching, timeline reconstruction and anomaly detection for incident response.
-
Rekall rekall-forensic.com
Open source tool (and library) for the extraction of digital artifacts from volatile memory (RAM) samples.
-
any.run app.any.run
Interactive online malware analysis service for dynamic and static research of most types of threats using any environment.
-
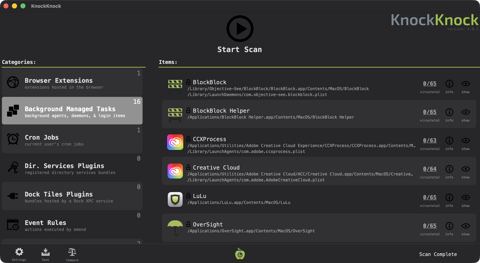
KnockKnock objective-see.com
See what's persistently installed on your Mac.
-
osquery osquery.io
osquery is an instrumentation framework that expose the operating system as a high-performance relational database.
-
SPECTR3 github.com
Acquire, triage and investigate remote evidence via portable iSCSI readonly access
-
Panorama github.com
Fast incident overview on live Windows systems.
-
traceroute-circl github.com
Extended traceroute to support the activities of CSIRT (or CERT) operators. Usually CSIRT team have to handle incidents based on IP addresses received. Created by Computer Emergency Response Center Luxembourg.
-
PyaraScanner github.com
Very simple multi-threaded many-rules to many-files YARA scanning Python script for malware zoos and IR.
-
domfind github.com
Python DNS crawler for finding identical domain names under different TLDs.
-
TheHive thehive-project.org
Scalable 3-in-1 open source and free solution designed to make life easier for SOCs, CSIRTs, CERTs and any information security practitioner dealing with security incidents that need to be investigated and acted upon swiftly.
-
PagerDuty Incident Response Documentation response.pagerduty.com
Documents that describe parts of the PagerDuty Incident Response process. It provides information not only on preparing for an incident, but also what to do during and after. Source is available on GitHub.
-
Redline fireeye.com
Provides host investigative capabilities to users to find signs of malicious activity through memory and file analysis, and the development of a threat assessment profile.
-
Hybrid Analysis hybrid-analysis.com
Free powerful online sandbox by CrowdStrike.
-
CRITs crits.github.io
Web-based tool which combines an analytic engine with a cyber threat database.
-
Intezer analyze.intezer.com
Intezer Analyze dives into Windows binaries to detect micro-code similarities to known threats, in order to provide accurate yet easy-to-understand results.
-
Zenduty zenduty.com
Zenduty is a novel incident management platform providing end-to-end incident alerting, on-call management and response orchestration, giving teams greater control and automation over the incident management lifecycle.
-
The Future of Incident Response youtube.com
Presented by Bruce Schneier at OWASP AppSecUSA 2015.
-
Yomi yomi.yoroi.company
Free MultiSandbox managed and hosted by Yoroi.
-
X-Ways Forensics x-ways.net
Forensics tool for Disk cloning and imaging. It can be used to find deleted files and disk analysis.
-
WindowsSCOPE windowsscope.com
Memory forensics and reverse engineering tool used for analyzing volatile memory offering the capability of analyzing the Windows kernel, drivers, DLLs, and virtual and physical memory.
-
Valkyrie Comodo valkyrie.comodo.com
Valkyrie uses run-time behavior and hundreds of features from a file to perform analysis.
-
The ESF Playground themittenmac.com
A tool to view the events in Apple Endpoint Security Framework (ESF) in real time.
-
Kaspersky CyberTrace support.kaspersky.com
Threat intelligence fusion and analysis tool that integrates threat data feeds with SIEM solutions. Users can immediately leverage threat intelligence for security monitoring and incident report (IR) activities in the workflow of their existing security operations.
-
PALADIN sumuri.com
Modified Linux distribution to perform various forensics task in a forensically sound manner. It comes with many open source forensics tools included.
-
Open Computer Forensics Architecture sourceforge.net
Another popular distributed open-source computer forensics framework. This framework was built on Linux platform and uses postgreSQL database for storing data.
-
NST - Network Security Toolkit sourceforge.net
Linux distribution that includes a vast collection of best-of-breed open source network security applications useful to the network security professional.
-
The Sleuth Kit & Autopsy sleuthkit.org
Unix and Windows based tool which helps in forensic analysis of computers. It comes with various tools which helps in digital forensics. These tools help in analyzing disk images, performing in-depth analysis of file systems, and various other things.
-
Reverse.IT reverse.it
Alternative domain for the Hybrid-Analysis tool provided by CrowdStrike.
-
X-Ray 2.0 raymond.cc
Windows utility (poorly maintained or no longer maintained) to submit virus samples to AV vendors.
-
RaQet raqet.github.io
Unconventional remote acquisition and triaging tool that allows triage a disk of a remote computer (client) that is restarted with a purposely built forensic operating system.
-
Stalk percona.com
Collect forensic data about MySQL when problems occur.
-
CORTEX XSOAR paloaltonetworks.com
Paloalto security orchestration, automation and response platform with full Incident lifecycle management and many integrations to enhance automations.
-
OSForensics osforensics.com
Tool to acquire live memory on 32-bit and 64-bit systems. A dump of an individual process’s memory space or physical memory dump can be done.
-
PMDump ntsecurity.nu
Tool that lets you dump the memory contents of a process to a file without stopping the process.
-
Scout2 nccgroup.github.io
Security tool that lets Amazon Web Services administrators assess their environment's security posture.
-
Metadefender Cloud metadefender.com
Free threat intelligence platform providing multiscanning, data sanitization and vulnerability assessment of files.
-
Introduction to DFIR medium.com
By Scott J. Roberts.
-
Cyphon medevel.com
Cyphon eliminates the headaches of incident management by streamlining a multitude of related tasks through a single platform. It receives, processes and triages events to provide an all-encompassing solution for your analytic workflow — aggregating data, bundling and…
-
MAGNET DumpIt magnetforensics.com
Fast memory acquisition tool for Windows (x86, x64, ARM64). Generate full memory crash dumps of Windows machines.
-
Magnet ACQUIRE magnetforensics.com
ACQUIRE by Magnet Forensics allows various types of disk acquisitions to be performed on Windows, Linux, and OS X as well as mobile operating systems.
-
Magnet RAM Capture magnetforensics.com
Free imaging tool designed to capture the physical memory of a suspect’s computer. Supports recent versions of Windows.
-
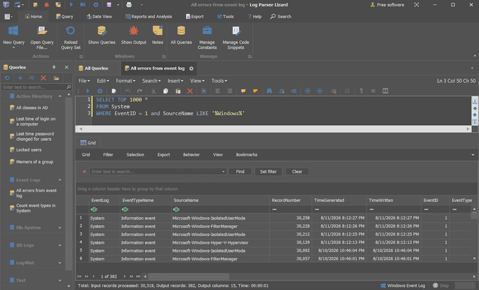
Log Parser Lizard lizard-labs.com
Execute SQL queries against structured log data: server logs, Windows Events, file system, Active Directory, log4net logs, comma/tab separated text, XML or JSON files. Also provides a GUI to Microsoft LogParser 2.2 with powerful UI elements: syntax editor, data grid, chart…
-
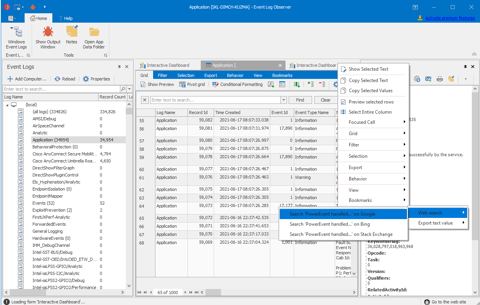
Event Log Observer lizard-labs.com
View, analyze and monitor events recorded in Microsoft Windows event logs with this GUI tool.
-
Limacharlie limacharlie.io
Endpoint security platform composed of a collection of small projects all working together that gives you a cross-platform (Windows, OSX, Linux, Android and iOS) low-level environment for managing and pushing additional modules into memory to extend its functionality.
-
KAPE kroll.com
Kroll Artifact Parser and Extractor (KAPE) by Eric Zimmerman. A triage tool that finds the most prevalent digital artifacts and then parses them quickly. Great and thorough when time is of the essence.
-
Joe Sandbox (Community) joesandbox.com
Joe Sandbox detects and analyzes potential malicious files and URLs on Windows, Android, Mac OS, Linux, and iOS for suspicious activities; providing comprehensive and detailed analysis reports.
-
IPASIS ipasis.com
Real-time IP reputation and email validation API for investigating suspicious interactions. Returns an Interaction Trust Score (0-100) combining VPN/proxy/Tor detection with email risk assessment in a single API call.
-
Guymager guymager.sourceforge.net
Free forensic imager for media acquisition on Linux.
- next page of items loading…