Executable Packing
759 items from dhondta/awesome-executable-packing ★1,628
-
Anti-emulation trends in modern packers: A survey on the evolution of anti-emulation techniques in UPA packers link.springer.com
(May 2018)
-
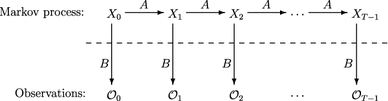
Packer identification using byte plot and Markov plot link.springer.com
(September 2015)
-
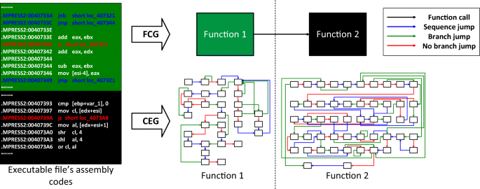
2-SPIFF: A 2-stage packer identification method based on function call graph and file attributes link.springer.com
(December 2021) :star:
-
A survey on run-time packers and mitigation techniques link.springer.com
(November 2023) :star: :star:
-
Entropy analysis to classify unknown packing algorithms for malware detection link.springer.com
(May 2016) :star:
-
An efficient block-discriminant identification of packed malware link.springer.com
(August 2015)
-
Secure and advanced unpacking using computer emulation link.springer.com
(August 2007)
-
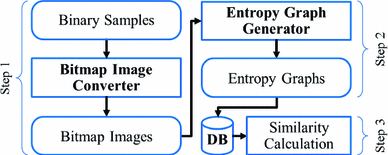
Malware analysis using visualized images and entropy graphs link.springer.com
(February 2015)
-
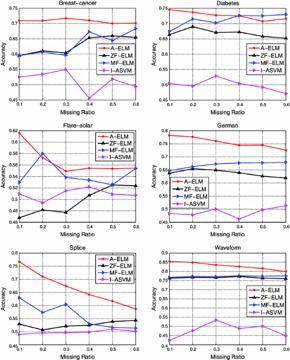
Absent extreme learning machine algorithm with application to packed executable identification link.springer.com
(January 2016)
-
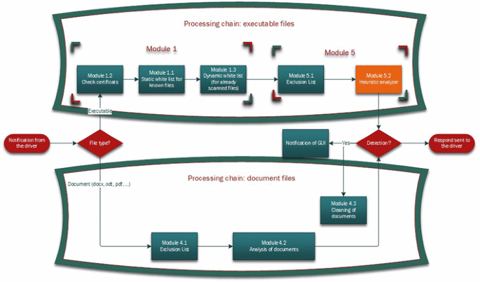
Construction and evaluation of the new heuristic malware detection mechanism based on executable files static analysis link.springer.com
(August 2018)
-
Structural analysis of binary executable headers for malware detection optimization link.springer.com
(May 2017)
-
Singular value decomposition and metamorphic detection link.springer.com
(November 2015)
-
Structural entropy and metamorphic malware link.springer.com
(November 2013)
-
Hunting for metamorphic engines link.springer.com
(November 2006)
-
An entropy-based distance measure for analyzing and detecting metamorphic malware link.springer.com
(June 2018)
-
Unknown malcode detection using OPCODE representation link.springer.com
(December 2008)
-
Deobfuscation of virtualization-obfuscated code through symbolic execution and compilation optimization link.springer.com
(April 2018)
-
Measuring and defeating anti-instrumentation-equipped malware link.springer.com
(June 2017)
-
Detection of metamorphic malware packers using multilayered LSTM networks link.springer.com
(November 2020) :star:
-
LIAPP liapp.lockincomp.com
Easiest and most powerful mobile app security solution.
-
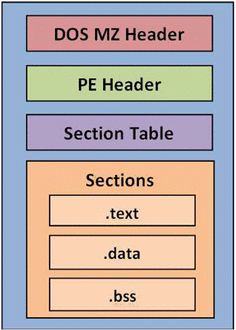
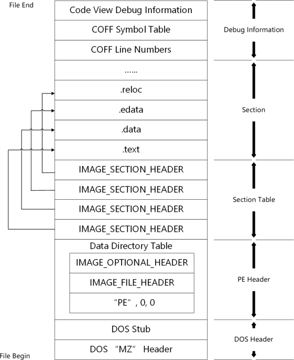
PE format - Win32 apps learn.microsoft.com
-
Laturi laturi.haxor.fi
Linker and compressor intended to be used for macOS 1k, 4k and perhaps 64K intros.
-
An original entry point detection method with candidate-sorting for more effective generic unpacking jstage.jst.go.jp
(January 2015)
-
An empirical evaluation of an unpacking method implemented with dynamic binary instrumentation jstage.jst.go.jp
(September 2011)
-
BareUnpack: Generic unpacking on the bare-metal operating system jstage.jst.go.jp
(December 2018)
-
An accurate packer identification method using support vector machine jstage.jst.go.jp
(January 2014)
-
-
ZProtect jiami.net
Renames metadata entities and supports advanced obfuscation methods that harden protection scheme and foil reverse engineering altogether.
-
Mal-XT: Higher accuracy hidden-code extraction of packed binary executable iopscience.iop.org
(November 2018)
-
Mal-xtract: Hidden code extraction using memory analysis iopscience.iop.org
(January 2017)
-
Pin intel.com
Dynamic binary instrumentation framework for the IA-32, x86-64 and MIC instruction-set architectures that enables the creation of dynamic program analysis tools.
-
Tutorial: An overview of malware detection and evasion techniques inria.hal.science
(December 2018)
-
Chosen-instruction attack against commercial code virtualization obfuscators ink.library.smu.edu.sg
(April 2022) :star:
-
Unpacking, reversing, patching infosecinstitute.com
-
-
Opcodes as predictor for malware inderscienceonline.com
(January 2008)
-
BinStat tool for recognition of packed executables ijofcs.org
(September 2010)
-
PE file features in detection of packed executables ijcte.org
(January 2012)
-
A survey on malware analysis techniques: Static, dynamic, hybrid and memory analysis ijaseit.insightsociety.org
(September 2018)
-
Hashing-based encryption and anti-debugger support for packing multiple files into single executable ijarcs.info
(February 2018)
-
Evading anti-malware engines with deep reinforcement learning ieeexplore.ieee.org
(March 2019) :star:
-
A survey on machine learning-based detection and classification technology of malware ieeexplore.ieee.org
(September 2021) :star:
-
A comprehensive solution for obfuscation detection and removal based on comparative analysis of deobfuscation tools ieeexplore.ieee.org
(October 2021) :star:
-
Enhanced metamorphic techniques-A case study against havex malware ieeexplore.ieee.org
(August 2021) :star:
-
BODMAS: An open dataset for learning based temporal analysis of PE malware ieeexplore.ieee.org
(May 2021) :star:
-
Functionality-preserving black-box optimization of adversarial windows malware ieeexplore.ieee.org
(May 2021) :star:
-
Packer identification method for multi-layer executables with k-Nearest neighbor of entropies ieeexplore.ieee.org
(October 2020) :star:
-
Bypassing anti-analysis of commercial protector methods using DBI tools ieeexplore.ieee.org
(January 2021) :star:
-
Experimental comparison of machine learning models in malware packing detection ieeexplore.ieee.org
(September 2020) :star:
-
DroidPDF: The obfuscation resilient packer detection framework for Android Apps ieeexplore.ieee.org
(July 2020)
- next page of items loading…