Full-system dynamic tracing on Linux using eBPF and bpftrace
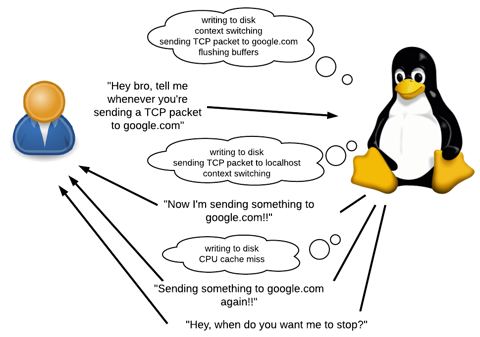
A detailed introduction to tracing with eBPF, from listing the available trace points to running bpftrace programs.
- from
- eBPF
- added
- 2026-10-10
- likes
- 0
similar
-
bpftrace bpftrace.org
A tool for tracing with its own high-level tracing language. It is flexible enough to be envisioned as a Linux replacement for DTrace and SystemTap.
-
linux/kernel/trace/bpf_trace.c git.kernel.org
Functions and eBPF helpers related to tracing and monitoring (kprobes, tracepoints, etc.).
-
Linux Extended BPF (eBPF) Tracing Tools brendangregg.com
An in-depth collection of information around examples of performance analysis tools using eBPF. Contains also a section at the end of the page about other resources.
-
All your tracing are belong to BPF blog.trailofbits.com
A step-by-step walkthrough to integrate tracing capabilities in your C++ applications with the LLVM libraries.
-
-
Tracee github.com
A runtime security and forensics tool for Linux which uses eBPF technology to trace the system and applications at runtime, and analyze collected events to detect suspicious behavioral patterns.
eBPF › Articles and Presentations > Kernel Tracing: “A detailed introduction to tracing with eBPF, from listing the available trace points to running bpftrace programs.”