DevSecOps
147 items from taptuit/awesome-devsecops ★1,746
-
Vault vaultproject.io
An encrypted datastore secure enough to hold environment and application secrets.
-
SonarQube Server sonarqube.org
SonarQube empowers development teams with a code quality and security solution that deeply integrates into your enterprise environment; enabling you to deploy clean code consistently and reliably. SonarQube provides a free and open source Community Build.
-
LGTM lgtm.com
copyright: — Find security vulnerabilities, variants, and critical code quality issues using CodeQL queries over source code. Automatic PR code review; free for open source. Formerly semmle. It supports public Git repositories hosted on Bitbucket Cloud, GitHub.com, GitLab.com.
-
Dependabot dependabot.com
GitHub - Automatically scan GitHub repositories for vulnerabilities and create pull requests to merge in patched dependencies.
-
Secure Coding Guidelines wiki.mozilla.org
Mozilla - A guideline containing specific secure development standards for secure web application development.
-
GitGuardian gitguardian.com
GitGuardian - A web-based solution that scans and monitors public and private git repositories for secrets.
-
ESLint eslint.org
JS Foundation - Linting tool for JavaScript with multiple security linting rules available.
-
Cybrary cybrary.it
Cybrary - Subscription based online courses with dedicated categories for cybersecurity and DevSecOps.
-
Portswigger Web Security Academy portswigger.net
PortSwigger - A set of materials and labs to learn and exploit common web vulnerabilities.
-
PentesterLab pentesterlab.com
Variety of VM and online challenges (paid).
-
Damn Vulnerable Web Application dvwa.co.uk
PHP/MySQL web application that is damn vulnerable.
-
Security Checklist by OWASP owasp.org
A checklist by OWASP for testing web applications based on assurance level. Covers multiple topics like Architecture, IAM, Sanitization, Cryptography and Secure Configuration.
-
Shift Security Left shift-security-left.curated.co
Cossack Labs - A free biweekly newsletter for security-aware developers covering application security, secure architecture, DevSecOps, cryptography, incidents, etc. that can be useful for builders and (to a lesser extent) for breakers.
-
terraform-compliance terraform-compliance.com
A lightweight, compliance- and security focused, BDD test framework against Terraform.
-
SonarQube for IDE sonarlint.org
SonarQube for IDE (formerly SonarLint) is a free IDE extension available for IntelliJ, VS Code, Visual Studio, and Eclipse, to find and fix coding issues in real-time, flagging issues as you code, just like a spell-checker. More than a linter, it also delivers rich contextual…
-
Semgrep semgrep.dev
A fast, open-source, static analysis tool for finding bugs and enforcing code standards at editor, commit, and CI time. Its rules look like the code you already write; no abstract syntax trees or regex wrestling. Supports 17+ languages.
-
RIPS ripstech.com
copyright: — A static source code analyser for vulnerabilities in PHP scripts.
-
Key Management Service (KMS) aws.amazon.com
Amazon AWS - Create and manage cryptographic keys in AWS.
-
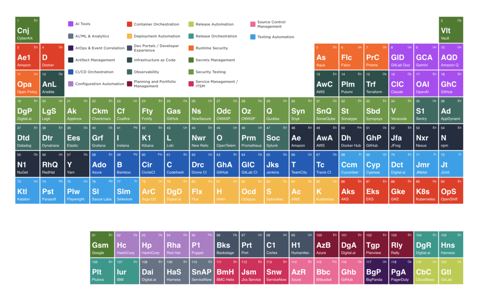
Periodic Table of DevOps Tools xebialabs.com
XebiaLabs - A collection of DevSecOps tooling categorised by tool functionality.
-
Alice and Bob Learn Application Security wiley.com
Tanya Janca - An accessible and thorough resource for anyone seeking to incorporate, from the beginning of the System Development Life Cycle, best security practices in software development.
-
Coding Standards wiki.sei.cmu.edu
CERT - A collection of secure development standards for C, C++, Java and Android development.
-
WeHackPuple wehackpurple.com
WeHackPurple - Online courses that teach application security theory and hands-on technical lessons.
-
Threatspec threatspec.org
Threatspec - Define threat modelling as code.
-
TAG Security tag-security.cncf.io
Cloud Native Computing Foundation - TAG Security facilitates collaboration to discover and produce resources that enable secure access, policy control, and safety for operators, administrators, developers, and end-users across the cloud native ecosystem.
-
Security Training for Everyone sudo.pagerduty.com
Pager Duty - A presentation created and open-sourced by PagerDuty to provide security training employees.
-
Security Training for Engineers sudo.pagerduty.com
Pager Duty - A presentation created and open-sourced by PagerDuty to provide security training to software engineers.
-
Streamdal streamdal.com
Streamdal - Embed privacy controls in your application code to detect and monitor PII as it enters and leaves your systems, preventing it from reaching unintended databases, data streams, or pipelines.
-
Spectral DeepConfig spectralops.io
Spectral - Find misconfiguration both in infrastructure as well as apps as early as commit time.
-
SpectralOps spectralops.io
Spectral - Automated code security, secrets, tokens and sensitive data scanning.
-
DevSecOps: Making Security Central To Your DevOps Pipeline spacelift.io
Spacelift - An article explains what DevSecOps aims to achieve, why it’s advantageous, and how the DevSecOps lifecycle looks.
- next page of items loading…