DevSecOps
147 items from taptuit/awesome-devsecops ★1,746
-
terraform-compliance terraform-compliance.com
A lightweight, compliance- and security focused, BDD test framework against Terraform.
-
SonarQube for IDE sonarlint.org
SonarQube for IDE (formerly SonarLint) is a free IDE extension available for IntelliJ, VS Code, Visual Studio, and Eclipse, to find and fix coding issues in real-time, flagging issues as you code, just like a spell-checker. More than a linter, it also delivers rich contextual…
-
Semgrep semgrep.dev
A fast, open-source, static analysis tool for finding bugs and enforcing code standards at editor, commit, and CI time. Its rules look like the code you already write; no abstract syntax trees or regex wrestling. Supports 17+ languages.
-
RIPS ripstech.com
copyright: — A static source code analyser for vulnerabilities in PHP scripts.
-
Key Management Service (KMS) aws.amazon.com
Amazon AWS - Create and manage cryptographic keys in AWS.
-
Periodic Table of DevOps Tools xebialabs.com
XebiaLabs - A collection of DevSecOps tooling categorised by tool functionality.
-
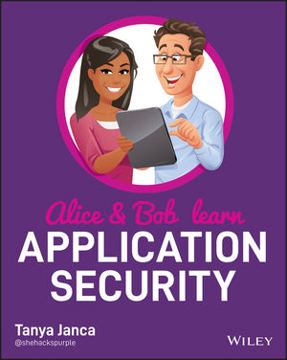
Alice and Bob Learn Application Security wiley.com
Tanya Janca - An accessible and thorough resource for anyone seeking to incorporate, from the beginning of the System Development Life Cycle, best security practices in software development.
-
Coding Standards wiki.sei.cmu.edu
CERT - A collection of secure development standards for C, C++, Java and Android development.
-
WeHackPuple wehackpurple.com
WeHackPurple - Online courses that teach application security theory and hands-on technical lessons.
-
Threatspec threatspec.org
Threatspec - Define threat modelling as code.
-
TAG Security tag-security.cncf.io
Cloud Native Computing Foundation - TAG Security facilitates collaboration to discover and produce resources that enable secure access, policy control, and safety for operators, administrators, developers, and end-users across the cloud native ecosystem.
-
Security Training for Everyone sudo.pagerduty.com
Pager Duty - A presentation created and open-sourced by PagerDuty to provide security training employees.
-
Security Training for Engineers sudo.pagerduty.com
Pager Duty - A presentation created and open-sourced by PagerDuty to provide security training to software engineers.
-
Streamdal streamdal.com
Streamdal - Embed privacy controls in your application code to detect and monitor PII as it enters and leaves your systems, preventing it from reaching unintended databases, data streams, or pipelines.
-
Spectral DeepConfig spectralops.io
Spectral - Find misconfiguration both in infrastructure as well as apps as early as commit time.
-
SpectralOps spectralops.io
Spectral - Automated code security, secrets, tokens and sensitive data scanning.
-
DevSecOps: Making Security Central To Your DevOps Pipeline spacelift.io
Spacelift - An article explains what DevSecOps aims to achieve, why it’s advantageous, and how the DevSecOps lifecycle looks.
-
DevSecOps Podcast Series soundcloud.com
OWASP - Discussions with thought leaders and practitioners to integrate security into the development lifecycle.
-
Snyk Open Source snyk.io
Snyk - Automated vulnerable dependency monitoring and upgrades using Snyk's dedicated vulnerability database.
-
Snyk Container snyk.io
Snyk - Scan Docker and Kubernetes applications for security vulnerabilities during CI/CD or via continuous monitoring.
-
DevSecOps Hub snyk.io
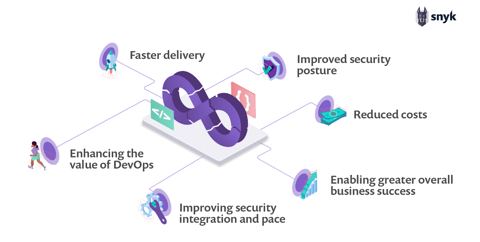
Snyk - Introduction to key DevSecOps concepts, processes and technologies.
-
Sigstore sigstore.dev
sigstore is a set of free to use and open source tools, including fulcio, cosign and rekor, handling digital signing, verification and checks for provenance needed to make it safer to distribute and use open source software.
-
SD Elements securitycompass.com
Security Compass - Identify and rank threats, generate actionable tasks and track related tickets.
-
SecureFlag secureflag.com
OWASP - Hands-on secure coding training for Developers and Build/Release Engineers.
-
Secure Code Warrior securecodewarrior.com
Secure Code Warrior - Gamified and hands-on secure development training with support for courses, assessments and tournaments.
-
CredScan secdevtools.azurewebsites.net
Microsoft - A credential scanning tool that can be run as a task in Azure DevOps pipelines.
-
SANS - A poster containing the Securing Web Application Technologies (SWAT) Checklist, SANS Cloud Security Curriculum, Cloud Security Top 10, Top 12 Kubernetes Threats, and Secure DevOps Toolchain.
-
Fundamental Practices for Secure Software Development safecode.org
SAFECode - Guidelines for implementing key secure development practices throughout the SDLC.
-
Requires.io requires.io
Olivier Mansion & Alexis Tabary - Automated vulnerable dependency monitoring and upgrades for Python projects.
-
Renovate renovate.whitesourcesoftware.com
WhiteSource - Automatically monitor and update software dependencies for multiple frameworks and languages using a CLI or git repository apps.
-
Practical DevSecOps practical-devsecops.com
Practical DevSecOps - Learn DevSecOps concepts, tools, and techniques from industry experts with practical DevSecOps using state of the art browser-based labs.
-
BurpSuite Enterprise Edition portswigger.net
PortSwigger - BurpSuite's web application vulnerability scanner used widely by penetration testers, modified with CI/CD integration and continuous monitoring over multiple web applications.
-
Application Security Podcast podcast.securityjourney.com
Security Journey - Interviews with industry experts about specific application security concepts.
-
Pentest-Ground pentest-ground.com
Pentest-Tools.com - Pentest-Ground is a free playground with deliberately vulnerable web applications and network services.
-
Our Approach to Employee Security Training pagerduty.com
Pager Duty - Guidelines to running security training within an organisation.
-
Vulnerable Web Apps Directory owasp.org
OWASP - A collection of vulnerable web applications for learning purposes.
-
Threat Dragon owasp.org
OWASP - Threat model diagramming tool.
-
Proactive Controls owasp.org
OWASP - OWASP's list of top ten controls that should be implemented in every software development project.
-
Dependency-Check owasp.org
OWASP - Scans dependencies for publicly disclosed vulnerabilities using CLI or build server plugins.
-
Secure Coding Practices Quick Reference Guide owasp.org
OWASP - A checklist to verify that secure development standards have been followed.
-
Nightfall nightfall.ai
Nightfall - A web-based platform that monitors for sensitive data disclosure across several SDLC tools, including GitHub repositories.
-
The Secure Developer mydevsecops.io
Snyk - Discussion about security tools and best practices for software developers.
-
Threat Modelling Tool microsoft.com
Microsoft - Threat model diagramming tool.
-
Secure Development Lifecycle microsoft.com
Microsoft - A collection of tools and practices that serve as a framework for the secure development lifecycle.
-
Kubescape kubescape.io
Cloud Native Computing Foundation - An open-source Kubernetes security platform for your IDE, CI/CD pipelines, and clusters.
-
SecureFlag Knowledge Base knowledge-base.secureflag.com
OWASP - A repository of information about software vulnerabilities and how to prevent them.
-
JFrog XRay jfrog.com
JFrog - Security and compliance analysis for artifacts stored in JFrog Artifactory.
-
IriusRisk iriusrisk.com
IriusRisk - Draw threat models and capture threats and countermeasures and manage risk.
-
SecuriCAD foreseeti.com
Forseeti - Treat modelling and attack simulations for IT infrastructure.
-
NPM Audit docs.npmjs.com
NPM - Vulnerable package auditing for node packages built into the npm CLI.
- next page of items loading…