Detection Engineering
78 items from infosecb/awesome-detection-engineering ★1,357
-
Blue-team-as-Code - the Spiral of Joy | Den Iuzvyk, Oleg Kolesnikov sansorg.egnyte.com
Blue-Team-as-Code: Lessons From Real-world Red Team Detection Automation Using Logs.
-
Detection Maturity Level (DML) Model | Ryan Stillions ryanstillions.blogspot.com
Defines and describes 8 different levels of an organization's threat detection program maturity.
-
Rulehound rulehound.com
An index of publicly available and open-source threat detection rulesets.
-
Detection at Scale Podcast | Jack Naglieri podcasts.apple.com
A detection engineering-focused podcast featuring many thought leaders in the specialization.
-
ATT&CK Navigator | MITRE mitre-attack.github.io
MITRE's open-source tool that can be used to track detection coverage, visibility, and other efforts and their relationship to the ATT&CK framework.
-
Prioritizing Detection Engineering | Ryan McGeehan medium.com
A longtime detection engineer outlines how a detection engineering program should be built from the ground up.
-
Threat Detection Maturity Framework | Haider Dost of Snowflake medium.com
A maturity matrix to measure the success of your threat detection program.
-
Detection Development Lifecycle | Haider Dost et al. medium.com
Snowflake’s implementation of the Detection Development Lifecycle.
-
MITRE ATT&CK Data Sources Blog Post medium.com
MITRE describes various data sources and how they relate to the TTPs found in the MITRE ATT&CK framework.
-
DETT&CT: MAPPING YOUR BLUE TEAM TO MITRE ATT&CK™ mbsecure.nl
Outlines a methodology measuring security data visibility and detection coverage against the MITRE ATT&CK framework.
-
Windows Logging Cheatsheets malwarearchaeology.com
Multiple cheatsheets outlined recommendations for Windows Event logging at various levels of granularity.
-
Living Off the Living Off the Land lolol.farm
A collection of resources for thriving off the land.
-
Cyber Kill Chain | Lockheed Martin lockheedmartin.com
Lockheed Martin's framework that outlines the 7 stages commonly observed in a cyber attack.
-
Microsoft XDR Advanced Hunting Schema learn.microsoft.com
To help with multi-table queries, you can use the advanced hunting schema, which includes tables and columns with event information and details about devices, alerts, identities, and other entity types.
-
Azure Defender for Cloud Security Alerts learn.microsoft.com
A list of all Azure Security for Cloud Alerts, their descriptions, and associated data sources.
-
InnerWarden innerwarden.com
Autonomous security agent for Linux with real-time threat detection and response via 38 eBPF hooks, 48 detectors, and 23 correlation rules.
-
Detection Engineering AI Maturity Framework | Brendan Chamberlain infosecb.github.io
A community framework with four maturity levels across ten dimensions for assessing how organizations apply AI and LLMs across a detection engineering program, from foundations through the detection lifecycle.
-
Panther Labs Detection Rules github.com
Panther Lab's native detection rules.
-
Open Threat Informed Detection Engineering aka OpenTide' github.com
an all-in-one Detection Engineering Operations framework created and maintained by the European Commission to convert your CTI into an actionable detection coverage graph combining threat vectors with detection objectives, and manage your entire detection library from a central…
-
Linux auditd Detection Ruleset github.com
Linux auditd ruleset that produces telemetry required for threat detection use cases.
-
Splunk ES Correlation Searches Best Practices | OpsTune github.com
A highly detailed guide to producing high quality detection content in the Splunk Enterprise Security app.
-
Elastic Yara Signatures github.com
Elastic's YARA signatures, which run on the Elastic endpoint agent.
-
Elastic Endpoint Behavioral Rules github.com
Elastic's endpoint behavioral (prevention) rules written in EQL, natively for the Elastic endpoint agent.
-
Elastic Endpoint Ransomware Artifact github.com
Elastic's ransomware artifact, which runs on the Elastic endpoint agent.
-
Elastic Detection Rules github.com
Elastic's detection rules written natively for the Elastic SIEM. Can easily be converted for use by other SIEMs using Uncoder.
-
Elastic's Detection Engineering Behavior Maturity Model elastic.co
Elastic's qualitative and quantitative approach to measuring threat detection program maturity.
-
Elastic Common Schema elastic.co
Elastic's proprietary model used as a framework for normalizing security data.
-
Splunk Common Information Model (CIM) docs.splunk.com
Splunk's proprietary model used as a framework for normalizing security data.
-
GCP Security Command Center Findings docs.cloud.google.com
A list of all GCP Security Command Center Findings, their descriptions, and associated data sources.
-
AWS GuardDuty Findings docs.aws.amazon.com
A list of all AWS GuardDuty Findings, their descriptions, and associated data sources.
-
Detections Digest | Sergey Polzunov detections-digest.rulecheck.io
A newsletter that features updates from many popular detection content sources listed here.
-
Detection Engineering Field Manual | Zack Allen detectionengineering.net
a series of posts exploring the various foundational components of Detection Engineering.
-
Detection Engineering Weekly | Zack Allen detectionengineering.net
A newsletter dedicated to news and how-tos for Detection Engineering.
-
Detection Engineering Maturity Matrix | Kyle Bailey detectionengineering.io
A detailed matrix that serves as a tool to measure the overall maturity of an organization's Detection Engineering program.
-
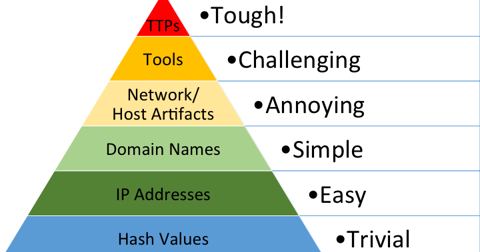
The Pyramid of Pain | David J Bianco detect-respond.blogspot.com
A model used to describe various categorizations of indicator's of compromise and their level of effectiveness in detecting threat actors.
-
How Google Does It: Making threat detection high-quality, scalable, and modern | Anton Chuvakin, Tim Nguyen cloud.google.com
The team at Google highlights 5 key principles for building a high quality, scalable and modern threat detection program.
-
CAR Coverage Comparison car.mitre.org
A matrix of MITRE ATT&CK technique IDs and links to available Splunk Security Content, Elastic detection rules, Sigma rules, and CAR content.
-
MITRE Cyber Analytics Repository (CAR) car.mitre.org
MITRE's well-maintained repository of detection content.
-
The Zen of Security Rules | Justin Ibarra br0k3nlab.com
Outlines 19 aphorisms that serve as universal principles for the creation of high quality detection content.
-
MaGMa (Management, Growth and Metrics & Assessment) Use Case Definition Model betaalvereniging.nl
A business-centric approach for defining threat detection use cases.
-
AttackRuleMap attackrulemap.com
Mapping of open-source detection rules and atomic tests.
-
MITRE ATT&CK Data Sources List attack.mitre.org
Data source objects added to MITRE ATT&CK as part of v10.
-
MITRE ATT&CK attack.mitre.org
The foundational framework of adversary tactics, techniques, and procedures based on real-world observations.
-
CTI Analyst Field Manual | Andrey Pautov 1200km.com
Practical CTI-to-detection reference covering evidence labels, source reliability, ATT&CK mapping gates, hunting hypotheses, and detection backlog workflow.
-
Security Monitoring Labs | cybersecurity101.net cybersecurity101.net
48 free, step-by-step labs that build a small Wazuh monitoring stack on your own VMs, connect Linux and Windows (Sysmon) log sources, then write and tune detection rules, test them with simulated events, triage alerts and report on coverage. No account or hosted platform.
-
Clankerusecase clankerusecase.com
Threat-led library of 7,800+ MITRE ATT&CK-mapped detections in Defender/Sentinel KQL, Sigma, Splunk SPL, Datadog, Falcon LogScale, and AWS CloudWatch, generated from public threat-intel reporting and schema-validated before publish.
-
Ridgeline Detection Library github.com
Production-validated detections across nine platforms (KQL, Sigma, Splunk, Athena, PowerShell, Velociraptor, YARA, Suricata, osquery), each with triggers, false positives, tuning guidance, and validation steps. Apache-2.0.
-
Control Assurance Lab | Gyubin Lee github.com
Runs reproducible matched-intervention experiments that distinguish target-control failures from failures masked by downstream safeguards.