-
Keeping your GitHub Actions and workflows secure Part 1: Preventing pwn requests securitylab.github.com
Combining pull_request_target workflow trigger with an explicit checkout of an untrusted PR may lead to repository compromise.
-
CloudQuarry: Digging for secrets in public AMIs securitycafe.ro
Researchers found 500GB of credentials, private repos, and keys in public AWS AMIs, impacting various industries.
-
Duo duo.com
State Of Identity Security Report (2025) - Analyzes the state of identity security and the challenges IT and security leaders face in 2025. Key findings reveal low confidence in identity providers and significant gaps in MFA adoption, despite a growing awareness of AI-driven…
-
Risk Explorer for Software Supply Chains riskexplorer.endorlabs.com
-
Duha duha.co
State of Security Vendors RSAC (2026) - Examines the current landscape of cybersecurity vendors at the RSA Conference, focusing on marketing trends, booth design strategies, and the prevalence of artificial intelligence terminology. Key findings reveal that 37 percent of the…
-
Publicly Exposed AWS Document DB Snapshots ramimac.me
Publicly exposed AWS DocumentDB snapshot of Cinemark Brazil revealed millions of customer records.
-
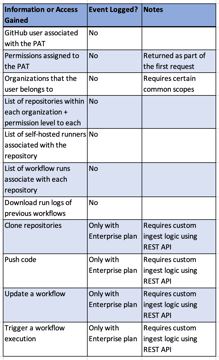
From Self-Hosted GitHub Runner to Self-Hosted Backdoor praetorian.com
Attackers exploit misconfigured runners and weak PAT security to gain persistence, escalate privileges, and move laterally.
-
DSCI & Seqrite dsci.in
India Cyber Threat Report (2025) - Analyzes the evolving cyber threat landscape in India using telemetry collected from 8.44 million endpoints across the country. Key findings reveal over 369 million security detections during 2024, with Trojans emerging as the most prevalent…
-
-
Drata drata.com
State of GRC (2025) - Focuses on the evolving role of Governance, Risk Management, and Compliance, transitioning from a cost center to a strategic business driver. A key finding highlights the challenges GRC teams face in balancing compliance complexity and business growth…
-
Unpinnable Actions: How Malicious Code Can Sneak into Your GitHub Actions Workflows paloaltonetworks.com
GitHub Actions, even when pinned to a commit SHA, can still pull in malicious code via mutable dependencies like Docker images, unlocked packages, or external scripts.
-
All the Small Things: Azure CLI Leakage and Problematic Usage Patterns paloaltonetworks.com
Azure CLI leaks secrets to CI/CD logs due to usage patterns.
-
Dragos dragos.com
OT Cybersecurity Report A Year in Review (2026) - Examines the rising sophistication of operational technology threat groups that actively map control loops to disrupt physical processes. Key findings reveal that ransomware impacted over 3300 industrial organizations in 2025…
-
Abusing Repository Webhooks to Access Internal CI/CD Systems at Scale paloaltonetworks.com
Repository webhooks, used to trigger CI/CD pipelines, can be abused to access internal systems.
-
New Zealand dpmc.govt.nz
Cyber Security Action Plan 2026pdf (2026) - Examines national cyber security strategy and threat mitigation across critical infrastructure, establishing immediate government priorities and regulatory frameworks for the coming years. Key findings outline fifteen targeted…
-
The GitHub Actions Worm: Compromising GitHub Repositories Through the Actions Dependency Tree paloaltonetworks.com
A novel GitHub Actions worm exploits the action dependency tree. Attackers compromise an action, then infect dependent actions via branch pushes or tag overwrites, spreading malware recursively.
-
How I hacked into Google's internal corporate assets observationsinsecurity.com
More ways to find dependencies in code for Dependency Confusion.
-
Office of the Director of National Intelligence dni.gov
Annual Threat Assessment (2026) - Assesses the global threat landscape facing the United States, focusing on transnational organized crime, illicit drug trafficking, and emerging technological challenges. Key findings indicate that synthetic opioid-related overdose deaths…
-
Hidden GitHub Commits and How to Reveal Them neodyme.io
A tool that can reveal deleted GitHub commits that potentially contain sensitive information and are not accessible via the public Git history.
-
Guardz digitalisationworld.com
State of MSP Threat Report (2026) - Examines the evolving MSP threat landscape and analyzes identity-driven attacks, artificial intelligence-powered threats, and endpoint vulnerabilities observed across managed SMB environments. Key findings reveal a 190% surge in ransomware…
-
10 real-world stories of how we've compromised CI/CD pipelines nccgroup.com
Examples include exploiting S3 misconfigurations, Jenkins plugin flaws, GitLab runner privilege escalations, Kubernetes pod annotation vulnerabilities, and compromised developer laptops.
-
Digital AI digital.ai
Application Security Threat Report (2025) - Quantifies evolving risks in modern application security. Key findings highlight industry trends, attack data categorized by industry and OS, and regional variations in attack rates.
-
AWS Targeted by a Package Backfill Attack mend.io
Scan commit history for internal packages to execute dependency confusion.
-
DigiCert digicert.com
Ultraddos Biannual Report (2025) - Analyzes the landscape of distributed denial of service attacks during the first half of 2025, documenting a significant shift in threat actor behavior and infrastructure capacity. Key findings reveal an 84.37 percent decrease in total attack…
-
PPE — Poisoned Pipeline Execution medium.com
Poisoned Pipeline Execution (PPE) lets attackers run malicious code in a CI/CD system without direct access.
-
Digi Americas digiamericas.org
Financial Sector Threat Landscape (2025) - Investigates the cybersecurity landscape of the Latin American financial sector, focusing on systemic vulnerabilities, regulatory gaps, and the tactics of prominent threat actors. Findings reveal that the region faces a…
-
Malicious code analysis: Abusing SAST (mis)configurations to hack CI systems medium.com
Misconfigured SAST tools can be exploited to execute malicious code on CI systems, allowing attackers to steal credentials or deploy malicious artifacts.
-
Department of Homeland Security dhs.gov
Threat Assessment (2025) - Analyzes homeland security threats in 2025, focusing on terrorism, transnational crime, and threats to critical infrastructure. Key concerns include the evolving tactics of nation-state actors, the persistent threat of cyberattacks targeting critical…
-
Bypassing required reviews using GitHub Actions medium.com
GitHub Actions can bypass required reviews, allowing malicious code pushes to protected branches.
-
Dependency Confusion: How I Hacked Into Apple, Microsoft and Dozens of Other Companies medium.com
Researchers uploaded malicious packages with internal company names, gaining access to Apple, Microsoft, and others due to dependency confusion.
-
Descope descope.com
State of Customer Identity Report (2025) - Analyzes the pervasive authentication stagnation noting 87% of organizations use passwords despite only 2% viewing them as effective. Highlights that open-source solutions nearly double revenue loss compared to commercial platforms…
-
Zuckerpunch - Abusing Self Hosted GitHub Runners at Facebook marcyoung.us
Hide commits in a GitHub PR.
-
How to completely own an airline in 3 easy steps maia.crimew.gay
Misconfigured CI system accessible from the internet.
-
Deloitte deloitte.com
Global Cyber Threat Intelligence Report (2025) - Analyzes global cyber threat trends throughout 2024, focusing on the evolution of ransomware, nation-state espionage, and shifting initial access techniques. Key findings include the continued dominance of ransomware driven by…
-
Vulnerable GitHub Actions Workflows Part 1: Privilege Escalation Inside Your CI/CD Pipeline legitsecurity.com
GitHub Actions workflow_run PE.
-
Deloitte deloitte.com
NASCIO Cybersecurity Study (2026) - Analyzes the evolving cybersecurity landscape for state governments, focusing on the impact of sophisticated threats, artificial intelligence, and shifting resource allocations. Key findings reveal that the percentage of state chief…
-
How We Hacked a Software Supply Chain for $50K landh.tech
Scraped JavaScript front-end files of the target and used ASTs to identify import/require statements which lead to discovering a public container with NPM credentials.
-
How a Single Vulnerability Can Bring Down the JavaScript Ecosystem landh.tech
Cache poisoning attack on the NPM registry rendering packages unavailable.
-
Deloitte deloitte.com
Future of Cyber Survey (2025) - Surveys the state of global cybersecurity leadership, analyzing strategic paradoxes and organizational maturity across various industries. Key findings reveal that 17 percent of surveyed enterprises qualify as frontrunners with advanced…
-
Leaking Secrets From GitHub Actions: Reading Files And Environment Variables, Intercepting Network/Process… karimrahal.com
Leaking secrets from vulnerable GitHub Actions workflows is possible via several methods: reading files/environment variables, intercepting communication, and dumping runner memory.
-
Cyber Edge delinea.com
Cyberthreat Defense Report (2025) - Analyzes the current state of cybersecurity defenses and the perceptions of IT security professionals. Key insights reveal a plateauing trend in successful cyberattacks, a significant preference for AI in security products, and persistent…
-
Fixing typos and breaching microsoft's perimeter johnstawinski.com
Bypass GitHub workflow approval requirement by becoming a contributor.
-
Delinea delinea.com
State Of Ransomware Report (2025) - Analyzes the evolving ransomware threat landscape and organizational responses, highlighting key trends and challenges. Key findings indicate a surge in ransomware breaches and data extortion, alongside increasing executive concern despite…
-
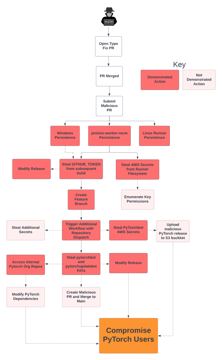
Playing with Fire – How We Executed a Critical Supply Chain Attack on PyTorch johnstawinski.com
Researchers exploited a critical PyTorch vulnerability via a malicious pull request to execute code on self-hosted runners.
-
Forging signed commits on GitHub iter.ca
A bug in GitHub's API allowed forging signed commits. By exploiting a regex flaw in an internal Codespaces API endpoint, an attacker could create commits signed by any user, despite GitHub's web flow signature.
-
Delinea delinea.com
AI In Identity Security Report (2025) - Analyzes the widespread adoption of AI in IT operations and the associated risks, emphasizing the necessity for updated identity governance frameworks to manage agentic and generative AI entities. Key findings indicate that while 94% of…
-
Grep.app grep.app
Search GitHub using regex.
-
United States Air Force defenseinnovationmarketplace.dtic.mil
Science and Technology Vision (2025) - Examines the cyberspace science and technology vision of the United States Air Force across multiple operational domains through the year 2025. Key insights detail strategic planning across 10 core sections to address escalating threats…
-
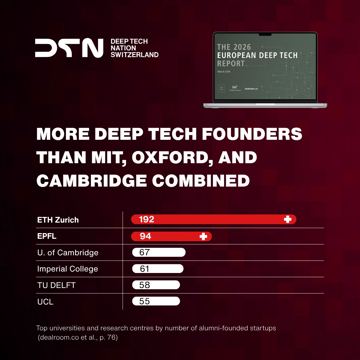
TableMedia deeptechnation.ch
European Deep Tech Report (2026) - Examines the state of European Deep Tech, focusing on its funding landscape, talent pool, and market opportunities. Key findings reveal that European Deep Tech VC funding reached $20.3 billion, comprising an.
-
Deepstrike deepstrike.io
Vulnerabilities Statistics (2025) - Analyzes the global surge in cybersecurity vulnerabilities throughout 2025, documenting a record pace of disclosures and the increasing speed of weaponization by threat actors. Key findings reveal that over 21,500 vulnerabilities were…
- next page of items loading…