-
Carloop carloop.io
Open source development kit that makes it easy to connect your car to the Internet. Lowest cost car hacking tool that is compatible with SocketCAN and can-utils. No OBD-II to serial cable required.
-
DEFCON Car Hacking Village carhackingvillage.com
Car Hacking exercises from DEFCON 24.
-
CANtact cantact.io
"The Open Source Car Tool" designed to help you hack your car. You can buy one or make your own following the guide here.
-
canopen canopen.readthedocs.io
Python module to communicate with CANopen devices
-
canbushack: Hack Your Car canbushack.com
course on Vehicle Hacking methodology.
-
CANBus Triple canb.us
General purpose Controller Area Network swiss army knife and development platform.
-
Tesla Motors bugcrowd.com
on Bugcrowd - Coordinated disclosure submissions accepted, paid bounties offered
-
Stellantis bugcrowd.com
on Bugcrowd - Coordinated disclosure submissions accepted, paid bounties offered
-
Car Hacking in 30 Minutes or Less brysonpayne.com
Using VirtualBox and Kali Linux, you can start car hacking using completely free open-source software and tools, including can-utils, ICSim, ScanTool, Wireshark, and tcpdump
-
Reverse engineering of the Nitro OBD2 blog.quarkslab.com
Reverse engineering of CAN diagnostic tools.
-
IOActive's Tools and Data blog.ioactive.com
Chris Valasek and Charlie Miller release some of their tools and data for hacking into vehicles in an effort to get more people into vehicle security research.
-
Big Bugs Podcast Episode 1: Auto Bugs - Critical Vulns found in Cars with Jason Haddix blog.bugcrowd.com
Jason Haddix explores major vulnerabilities found in cars.
-
FREE-FALL: HACKING TESLA FROM WIRELESS TO CAN BUS blackhat.com
Zeronights 2016 and later BlackHat talk by Sen Nie, Ling Liu, and Yuefeng Du from Tencent and KEEN Security lab
-
Pentesting vehicles with YACHT (Yet Another Car Hacking Tool) blackhat.com
A presentation that discusses different attack surfaces of a vehicle, then continues to describe an approach to car hacking along with tools needed to analyse and gather useful information.
-
CANSPY bitbucket.org
A platform giving security auditors to audit CAN devices. It can be used to block, forward or modify CAN frames on the fly autonomously as well as interactively.
-
Automobile Driver Fingerprinting, 2016 autosec.org
-
-
U.S. Automotve Cyber Security Summit automotivecybersecurity.com
European Automotive Cyber Security Summit - Conference series dedicated to automotive cyber security involving many OEMs, Tier 1s, academics, consultants, etc.
-
Automotive Security Research Group asrg.io
The Automotive Security Research Group (ASRG) is a non-profit initiative to promote the development of security solutions for automotive products.
-
ASRG asrg.io
The ASRG Disclosure Process is to support responsible disclosure when direct communication with the responsible company is unavailable or not responsive.
-
-
-
-
Inside Radio: An Attack and Defense Guide amazon.com
This book discusses the security issues in a wide range of wireless devices and systems,Chapter 4 433/315MHz Communication (4.3 4.4 4.5 is about car keys Security)
-
Embedded Networking with CAN and CANopen amazon.com
From 2003, this book fills in gaps in CAN literature and will educate you further on CAN networks and working with embedded systems.
-
Controller Area Network Prototyping with Arduino amazon.com
This book guides you through prototyping CAN applications on Arduinos, which can help when working with CAN on your own car.
-
A Comprehensible Guide to Controller Area Network amazon.com
An older book from 2005, but still a comprehensive guide on CAN buses and networking in vehicles.
-
2014 Car Hacker's Handbook amazon.com
Free guide to hacking vehicles from 2014.
-
2016 Car Hacker's Handbook amazon.com
Latest version of the Car Hacker's handbook with updated information to hack your own vehicle and learning vehicle security. For a physical copy as well unlimited PDF, MOBI, and EPUB copies of the book, buy it at No Starch Press. Sections are available online here.
-
智能汽车安全攻防大揭秘 amazon.cn
This book first introduced some basic knowledge of security for automotive R&D personnel, such as encryption and decryption, security authentication, digital signatures, common attack types, and methods. Then it introduced the working principles of some smart cars for security…
-
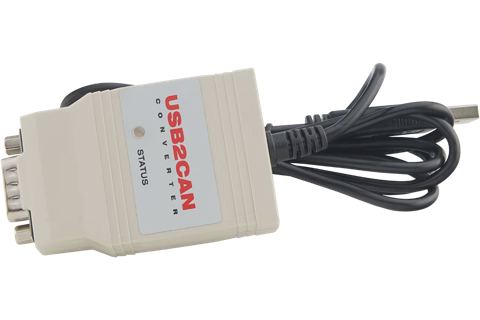
USB2CAN 8devices.com
Cheap USB to CAN connector that will register a device on linux that you can use to get data from a CAN network.
-
-
Counteractive Playbooks github.com
Counteractive PLaybooks collection.
-
AWS Incident Response Runbook Samples github.com
AWS IR Runbook Samples meant to be customized per each entity using them. The three samples are: "DoS or DDoS attack", "credential leakage", and "unintended access to an Amazon S3 bucket".
-
The Appliance for Digital Investigation and Analysis (ADIA) forensics.cert.org
VMware-based appliance used for digital investigation and acquisition and is built entirely from public domain software. Among the tools contained in ADIA are Autopsy, the Sleuth Kit, the Digital Forensics Framework, log2timeline, Xplico, and Wireshark. Most of the system…
-
GetData Forensic Imager forensicimager.com
Windows based program that will acquire, convert, or verify a forensic image in one of the following common forensic file formats.
-
Memoryze fireeye.com
Free memory forensic software that helps incident responders find evil in live memory. Memoryze can acquire and/or analyze memory images, and on live systems, can include the paging file in its analysis.
-
IOC Finder fireeye.com
Free tool from Mandiant for collecting host system data and reporting the presence of Indicators of Compromise (IOCs). Support for Windows only. No longer maintained. Only fully supported up to Windows 7 / Windows Server 2008 R2.
-
Highlighter fireeye.com
Free Tool available from Fire/Mandiant that will depict log/text file that can highlight areas on the graphic, that corresponded to a key word or phrase. Good for time lining an infection and what was done post compromise.
-
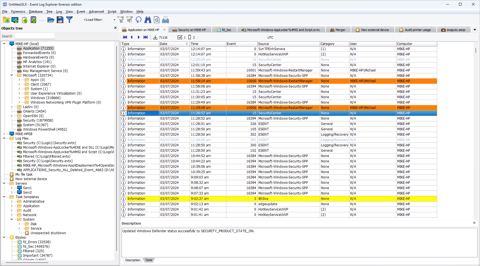
Event Log Explorer eventlogxp.com
Tool developed to quickly analyze log files and other data.
-
Eric Zimmerman Tools ericzimmerman.github.io
An updated list of forensic tools created by Eric Zimmerman, an instructor for SANS institute.
-
Microsoft ProcDump docs.microsoft.com
Dumps any running Win32 processes memory image on the fly.
-
Digital Forensics Discord Server discordapp.com
Community of 8,000+ working professionals from Law Enforcement, Private Sector, and Forensic Vendors. Additionally, plenty of students and hobbyists! Guide here.
-
How we abused Slack's TURN servers to gain access to internal services enablesecurity.com
-
SANS Investigative Forensic Toolkit (SIFT) Workstation digital-forensics.sans.org
Demonstrates that advanced incident response capabilities and deep dive digital forensic techniques to intrusions can be accomplished using cutting-edge open-source tools that are freely available and frequently updated.
-
HackDig en.hackdig.com
-
The Bug Hunters Methodology v2.1 docs.google.com
-
Slack DFIR channel dfircommunity.slack.com
Slack DFIR Communitiy channel - Signup here.
-
SSRF bible. Cheatsheet docs.google.com
-
How do we Stop Spilling the Beans Across Origins? docs.google.com
- next page of items loading…