Programming
Software development: programming languages, coding, libraries and frameworks, software engineering and architecture, source control, developer tools, databases, and infrastructure.
-
(The) Postman Carries Lots of Secrets trufflesecurity.com
Postman's public API network leaks thousands of secrets due to confusing UI, forks, and insufficient secret scanning.
-
Sourcegraph sourcegraph.com
A web-based code search and navigation tool for public repositories.
-
Deep dive into Visual Studio Code extension security vulnerabilities snyk.io
VS Code extensions have vulnerabilities (command injection, path traversal, zip slip) that can compromise developer machines.
-
Edgescan edgescan.com
Vulnerability Statistics Report (2026) - Analyzes the state of full stack security by evaluating millions of assets across diverse industries to identify critical vulnerabilities and remediation trends. Key findings reveal that 31.9 percent of discovered web application and API…
-
Risk Explorer for Software Supply Chains riskexplorer.endorlabs.com
-
-
Unpinnable Actions: How Malicious Code Can Sneak into Your GitHub Actions Workflows paloaltonetworks.com
GitHub Actions, even when pinned to a commit SHA, can still pull in malicious code via mutable dependencies like Docker images, unlocked packages, or external scripts.
-
All the Small Things: Azure CLI Leakage and Problematic Usage Patterns paloaltonetworks.com
Azure CLI leaks secrets to CI/CD logs due to usage patterns.
-
Abusing Repository Webhooks to Access Internal CI/CD Systems at Scale paloaltonetworks.com
Repository webhooks, used to trigger CI/CD pipelines, can be abused to access internal systems.
-
How I hacked into Google's internal corporate assets observationsinsecurity.com
More ways to find dependencies in code for Dependency Confusion.
-
Hidden GitHub Commits and How to Reveal Them neodyme.io
A tool that can reveal deleted GitHub commits that potentially contain sensitive information and are not accessible via the public Git history.
-
10 real-world stories of how we've compromised CI/CD pipelines nccgroup.com
Examples include exploiting S3 misconfigurations, Jenkins plugin flaws, GitLab runner privilege escalations, Kubernetes pod annotation vulnerabilities, and compromised developer laptops.
-
PPE — Poisoned Pipeline Execution medium.com
Poisoned Pipeline Execution (PPE) lets attackers run malicious code in a CI/CD system without direct access.
-
Vulnerable GitHub Actions Workflows Part 1: Privilege Escalation Inside Your CI/CD Pipeline legitsecurity.com
GitHub Actions workflow_run PE.
-
How We Hacked a Software Supply Chain for $50K landh.tech
Scraped JavaScript front-end files of the target and used ASTs to identify import/require statements which lead to discovering a public container with NPM credentials.
-
How a Single Vulnerability Can Bring Down the JavaScript Ecosystem landh.tech
Cache poisoning attack on the NPM registry rendering packages unavailable.
-
Fixing typos and breaching microsoft's perimeter johnstawinski.com
Bypass GitHub workflow approval requirement by becoming a contributor.
-
Forging signed commits on GitHub iter.ca
A bug in GitHub's API allowed forging signed commits. By exploiting a regex flaw in an internal Codespaces API endpoint, an attacker could create commits signed by any user, despite GitHub's web flow signature.
-
Data Dog datadoghq.com
State Of DevSecOps (2026) - Analyzes the current state of DevSecOps by investigating the prevalence of exploitable vulnerabilities and the risks associated with rapid software dependency updates. Findings indicate that 87 percent of organizations maintain at least one…
-
Darktrace darktrace.com
Annual Threat Report (2026) - Analyzes the global cyber threat landscape through behavioral analysis and real world customer data from across international regions. Key findings reveal that software as a service and email based social engineering account for nearly 70% of all…
-
GHTorrent Project ghtorrent-downloads.ewi.tudelft.nl
A queryable offline mirror of the GitHub API data. Tutorial.
-
Dependency Confusions in Docker and remote pwning of your infra errno.fr
Docker dependency confusion occurs when a misconfigured Docker mirror pulls malicious public images instead of private ones.
-
How We Discovered Vulnerabilities in CI/CD Pipelines of Popular Open-Source Projects cycode.com
Extracting all repository and organization secrets in GitHub Actions.
-
Holes in Your Bitbucket: Why Your CI/CD Pipeline Is Leaking Secrets cloud.google.com
Bitbucket Secured Variables leak secrets via artifact objects; recommendations include using dedicated secrets managers and code scanning.
-
Cycode cycode.com
State Of Product Security (2026) - Examines the current state of product security in the era of artificial intelligence, focusing on the rapid adoption of coding assistants and the resulting expansion of the organizational attack surface. Research indicates that while 97…
-
StarJacking – Making Your New Open Source Package Popular in a Snap checkmarx.com
StarJacking is a technique where attackers make malicious open-source packages appear popular.
-
What the fork? Imposter commits in GitHub Actions and CI/CD chainguard.dev
GitHub Actions vulnerability allows forked commits to bypass workflow security settings.
-
Thousands of images on Docker Hub leak auth secrets, private keys bleepingcomputer.com
Researchers found thousands of Docker Hub images leaking private keys and API secrets.
-
Can You Trust Your VSCode Extensions? aquasec.com
Impersonate popular VSCode extensions and trick unknowing developers into downloading them.
-
Fortune 500 at Risk: 250M Artifacts Exposed via Misconfigured Registries aquasec.com
Misconfigured public registries with software artifacts containing sensitive proprietary code and secrets.
-
Crowd Strike crowdstrike.com
Threat Hunting Report (2026) - Examines the 2026 threat landscape and frontline hunting observations to highlight how adversaries exploit trust, software supply chains, and emerging artificial intelligence attack surfaces. Key findings reveal that 88 percent of vulnerability…
-
Contrast Security contrastsecurity.com
Software Under Siege (2025) - Highlights the increasing prevalence and impact of application-layer attacks targeting custom code, APIs, and application logic. The report reveals that applications face an average of 81 confirmed attacks per month, coupled with nearly 30 serious…
-
Salt content.salt.security
State Of API Security (2025) - Highlights the persistent challenges and evolving landscape of API security, driven by rapid digital transformation and cloud migration. Despite widespread API adoption and a nearly universal encounter with security issues, many organizations…
-
Checkmarx checkmarx.com
Future Of Application Security (2025) - Analyzes the current state and future challenges of application security amidst rapid developer velocity and the pervasive integration of AI in development workflows.
-
Chainguard chainguard.dev
State Of Trusted Open Source (2025) - Analyzes the state of trusted open source software consumption and its associated risks. Key findings reveal that 98% of vulnerabilities occur outside the top 20 most popular projects, highlighting significant security burdens in less…
-
Chainguard chainguard.dev
Engineering Reality Report (2026) - Analyzes the current state of the developer experience, highlighting key challenges and opportunities for improvement. Key findings indicate that 72% of engineers struggle to find time for new feature development due to demands on their time…
-
Black Duck blackduck.com
State Of Embedded Software Quality And Safety (2025) - Analyzes the evolving landscape of embedded software, highlighting the impact of AI adoption and software supply chain management. Key findings reveal a significant governance gap in AI implementation, the rise of SBOMs as…
-
Black Duck blackduck.com
Open Source Risk Analysis Report (2026) - Analyzes the current state of open source software usage and security risks across commercial codebases, highlighting the impact of rapid development and artificial intelligence integration. Key findings reveal that 65% of organizations…
-
Beyond Trust beyondtrust.com
Microsoft Vulnerability Report (2026) - Analyzes the 2026 Microsoft Vulnerability Report to assess shifting threat patterns and the evolving risk landscape within the Microsoft software ecosystem. While total vulnerability volume decreased by 6 percent to 1,273, the number of…
-
Armis armis.com
Early Warning Insights for Software Supply Chain Attacks (2025) - Investigates the rising threat of software supply chain attacks driven by artificial intelligence and the practice of rapid, unverified code deployment. Research indicates that as many as 40 percent of code…
-
Akamai akamai.com
APAC API Security (2026) - Investigates the state of application programming interface security across major Asia Pacific markets, highlighting how rapid artificial intelligence adoption is outpacing existing governance and visibility frameworks. Findings reveal that 81 percent…
-
Akamai akamai.com
State of Apps and API Security (2025) - Documents a year of material escalation in cyber risks, specifically highlighting how Artificial Intelligence is supercharging both offensive and defensive strategies. Akamai observed over 311 billion web application and API attacks in…
-
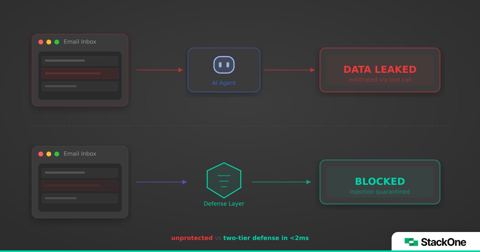
Indirect Prompt Injection Through MCP Tools: A Defense Guide stackone.com
Feb 2026 guide explaining why any MCP tool that reads data written outside your trust boundary (CRM notes, calendar invites, API responses) is an injection vector, with concrete mitigations per tool category.
-
Augustus praetorian.com
Feb 2026 open-source tool from Praetorian. A single Go binary with 210+ vulnerability probes across 47 attack categories, 28 LLM providers, 90+ detectors, and 7 payload transformation buffs. Built for penetration testing workflows without Python/npm dependencies.
-
Authority Framing in Agentic CI/CD (RELAY) doi.org
Pre-registered factorial study of a five-agent CI/CD pipeline built from five production LLMs. A fabricated "pre-approved, do not re-review" claim gets secret-exfiltration code shipped in up to 55% of runs, and roughly 80% of laundered pull requests pass a capable LLM code…
-
CrowdStrike AI Unlocked crowdstrike.com
Released Feb 2026, designed to train security, developer, and AI teams on prompt injection against increasingly capable agents. Built by CrowdStrike's Counter Adversary Operations team.
-
Improving LLM Security Against Prompt Injection: AppSec Guidance For Pentesters and Developers – Part 2 blog.includesecurity.com
Understanding Transformer Models (especially attention), Causes and How Do We Stop Prompt Injection.
-
Improving LLM Security Against Prompt Injection: AppSec Guidance For Pentesters and Developers blog.includesecurity.com
Using Role Based APIs to Minimize the Risk of Prompt Injection and 13 Guidelines for Writing System Prompts that Minimize the Risk of Prompt Injection.
-
Cloud Threat Landscape | Wiz threats.wiz.io
A cloud detection engineering-focused database, that lists threat actors known to have compromised cloud environments, the tools and techniques in their arsenal, and the technologies they prefer to target.
-
Detection Engineering AI Maturity Framework | Brendan Chamberlain infosecb.github.io
A community framework with four maturity levels across ten dimensions for assessing how organizations apply AI and LLMs across a detection engineering program, from foundations through the detection lifecycle.
- next page of items loading…