How AI Prompt Injection Works | Hands-on with LLMs
Jan 2026 AppSecEngineer tutorial with a code-level demo of injecting against a real LLM application and live testing of LLM Guard detection. One of the most practical end-to-end tutorials published to date.
- from
- Prompt Injection
- added
- 2026-10-10
- likes
- 0
similar
-
Improving LLM Security Against Prompt Injection: AppSec Guidance For Pentesters and Developers – Part 2 blog.includesecurity.com
Understanding Transformer Models (especially attention), Causes and How Do We Stop Prompt Injection.
-
Prompt Injection in LLM Agents (ReAct, Langchain) youtube.com
Theory and hands-on lab on prompt injection against Langchain ReAct agents.
-
MCP Prompt Injection: How AI Gets Hacked youtube.com
Nov 2025 hands-on walkthrough showing how prompt injection exploits tool metadata and trust boundaries in Model Context Protocol-integrated agents, which remain a primary attack surface as MCP adoption widens.
-
Securing AI Agents Against Prompt Injection Attacks arxiv.org
Nov 2025 benchmark of 847 adversarial test cases across 5 attack categories against 7 LLMs. The combined defense framework reduces attack success from 73.2% to 8.7% while retaining 94.3% of baseline task performance.
-
Improving LLM Security Against Prompt Injection: AppSec Guidance For Pentesters and Developers blog.includesecurity.com
Using Role Based APIs to Minimize the Risk of Prompt Injection and 13 Guidelines for Writing System Prompts that Minimize the Risk of Prompt Injection.
-
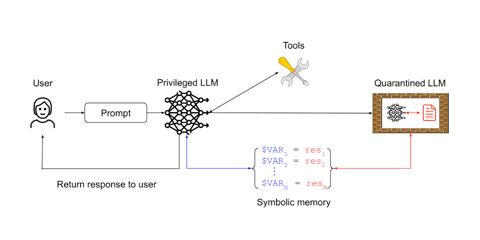
Design Patterns for Securing LLM Agents against Prompt Injections simonwillison.net
Overview of various strategies to mitigate the risk of prompt injection.
Prompt Injection › Tutorials: “Jan 2026 AppSecEngineer tutorial with a code-level demo of injecting against a real LLM application and live testing of LLM Guard detection. One of the most practical end-to-end tutorials published to date.”