Metadata recovery from obfuscated programs using machine learning
(December 2016)
- from
- Executable Packing
- added
- 2026-10-10
- likes
- 0
similar
-
Absent extreme learning machine algorithm with application to packed executable identification link.springer.com
(January 2016)
-
-
Malware detection through opcode sequence analysis using machine learning api.semanticscholar.org
(June 2015)
-
An application of machine learning to analysis of packed mac malware scholar.dsu.edu
(May 2022) :star:
-
-
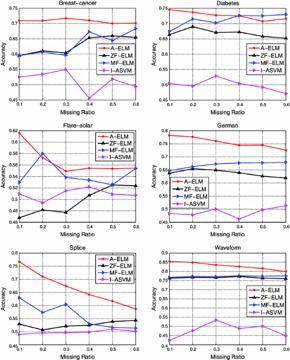
Executable Packing › :books: Literature > Scientific Research: “(December 2016)”