Snyk
A developer security platform that integrates directly into development tools, workflows, and automation pipelines.
- from
- Static Analysis & Code Quality, Angular, Cybersecurity Blue Team, Developer-First Products, Open Source Supporters
- added
- 2026-10-10
- likes
- 0
similar
-
Snyk Open Source snyk.io
Snyk - Automated vulnerable dependency monitoring and upgrades using Snyk's dedicated vulnerability database.
-
The Secure Developer mydevsecops.io
Snyk - Discussion about security tools and best practices for software developers.
-
-
Snyk Container snyk.io
Snyk - Scan Docker and Kubernetes applications for security vulnerabilities during CI/CD or via continuous monitoring.
-
Snyk snyk.io
Cloud Native Application Security Report (2026) - Examines the state of cloud native application security, highlighting deployment practices and vulnerability management trends. Key findings reveal that over 56 percent of organizations experienced a security incident involving…
-
Snyk Test Action github.com
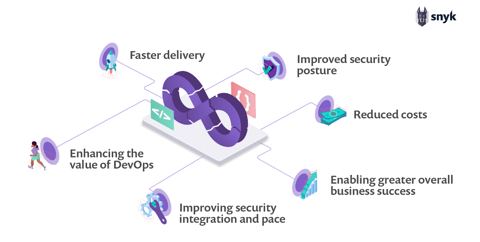
Static Analysis & Code Quality › Multiple languages: “copyright: — Snyk Code finds security vulnerabilities based on AI. Its speed of analysis allow us to analyse your code in real time and deliver results when you hit the save button in your IDE. Supported languages are Java, JavaScript, Python, PHP, C#, Go and TypeScript…”
Angular › Security and Authentication > Security Best Practices: “A developer security platform that integrates directly into development tools, workflows, and automation pipelines.”
Cybersecurity Blue Team › DevSecOps: “Finds and fixes vulnerabilities and license violations in open source dependencies and container images.”
Developer-First Products › Security: “Vulnerability scanner for code, dependencies, containers, and infrastructure as code.”
Open Source Supporters › Dependency Management: “Continuous dependency vulnerability assessment.”