compose-lint
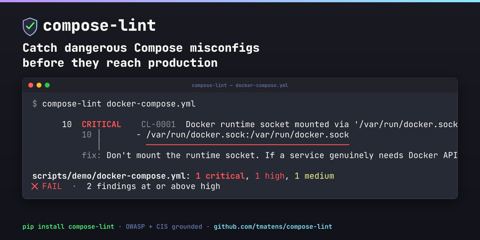
Security linter for Docker Compose files. Checks compose.yaml against 27 rules taken from the OWASP Docker Security Cheat Sheet and the CIS Docker Benchmark: mounted Docker socket, privileged mode, missing no-new-privileges, extra capabilities, writable root filesystem, ports…
- from
- Static Analysis & Code Quality
- added
- 2026-10-19
- likes
- 0
similar
-
compose-lint github.com
Lints Docker Compose files for security misconfigurations — privileged containers, unpinned images, Docker socket mounts, plaintext credentials — grounded in OWASP and the CIS Docker Benchmark.
-
Dockadvisor github.com
Lightweight Dockerfile linter with 60+ rules, quality scoring, and security checks.
-
Hadolint github.com
A Dockerfile linter that checks for best practices, common mistakes, and is also able to lint any bash written in RUN instructions;.
-
Dockle github.com
Container Image Linter for Security helping build the Best-Practice Docker Image. Scans Docker images for security vulnerabilities and CIS Benchmark compliance. Checks for secrets, credential exposure, and security best practices. Provides multiple severity levels (FATAL, WARN…
-
Docker bench security github.com
The Docker Bench for Security is a script that checks for dozens of common best-practices around deploying Docker containers in production.
-
Docker Commander github.com
A self-hosted Docker management and monitoring UI with multi-host support, Compose management, aggregated logs, alerts, RBAC, vulnerability scanning, and MCP integration.
Static Analysis & Code Quality › Other: “Security linter for Docker Compose files. Checks compose.yaml against 27 rules taken from the OWASP Docker Security Cheat Sheet and the CIS Docker Benchmark: mounted Docker socket, privileged mode, missing no-new-privileges, extra capabilities, writable root filesystem, ports…”